| @@ -1,10 +1,33 @@ |
| 1 | 1 | <div style="font-size: 0.85em; color: #656d76; margin-bottom: 1em; padding: 0.5em; background: #f6f8fa; border-radius: 4px;"> |
| 2 | | -📄 Source: <a href="https://github.com/chipsalliance/caliptra-sw/blob/10d4f5891650a6ae38150cac3ffbbe220b7db8ac/runtime/README.md" target="_blank">chipsalliance/caliptra-sw/runtime/README.md</a> @ <code>10d4f58</code> |
| 2 | +📄 Source: <a href="https://github.com/chipsalliance/caliptra-sw/blob/1b5589b23cfc2957a3c5934792643babc599aabc/runtime/README.md" target="_blank">chipsalliance/caliptra-sw/runtime/README.md</a> @ <code>1b5589b</code> |
| 3 | 3 | </div> |
| 4 | 4 | |
| 5 | | -# Caliptra Runtime Firmware v1.2 |
| 5 | +# Caliptra Runtime Firmware v2.0.1 |
| 6 | + |
| 7 | +*Spec version: 0.3* |
| 6 | 8 | |
| 7 | 9 | This specification describes the Caliptra Runtime Firmware. |
| 10 | + |
| 11 | +## Changelog |
| 12 | + |
| 13 | +v1.1: |
| 14 | + |
| 15 | +* [LMS Signature Verification](#lms_signature_verify-new-in-11) |
| 16 | + |
| 17 | +v1.2: |
| 18 | + |
| 19 | +* [Manifest-Based Image Authorization](#manifest-based-image-authorization-new-in-12) |
| 20 | + |
| 21 | +v2.0: |
| 22 | + |
| 23 | +* Add support for passive mode (same as 1.x) and subsystem (or active) mode |
| 24 | +* [MCU Runtime loading](#boot-and-initialization) (subsystem mode) |
| 25 | +* [Cryptographic mailbox commands](#cryptographic-mailbox-commands-new-in-20) |
| 26 | +* `ECDSA384_SIGNATURE_VERIFY` and `LMS_SIGNATURE_VERIFY` require the hash to be included in the message, as the SHA accelerator registers are no longer accessible outside Caliptra. These commands return a non-approved FIPS status because the caller supplies the digest. |
| 27 | + |
| 28 | +## Spec Opens |
| 29 | + |
| 30 | +* Cryptographic Mailbox: ML-KEM support |
| 8 | 31 | |
| 9 | 32 | ## Runtime Firmware environment |
| 10 | 33 | |
| @@ -16,11 +39,11 @@ |
| 16 | 39 | |
| 17 | 40 | * Initialize the [DICE Protection Environment (DPE)](#dice-protection-environment-dpe) |
| 18 | 41 | * Initialize any SRAM structures used by Runtime Firmware |
| 42 | +* Upload the firmware to the Manufacturer Control Unit (2.0, subsystem mode only) |
| 19 | 43 | |
| 20 | 44 | For behavior during other types of reset, see [Runtime firmware updates](#runtime-firmware-updates). |
| 21 | 45 | |
| 22 | | -If Runtime Firmware detects that Caliptra was reset during the execution of an operation, Runtime Firmware calls `DISABLE_ATTESTATION` because the internal state of Caliptra may |
| 23 | | -be corrupted. |
| 46 | +If Runtime Firmware detects that Caliptra was reset during the execution of an operation, Runtime Firmware calls `DISABLE_ATTESTATION` because the internal state of Caliptra may be corrupted. |
| 24 | 47 | |
| 25 | 48 | ### Main loop |
| 26 | 49 | |
| @@ -62,7 +85,98 @@ |
| 62 | 85 | possible; however, it will have its own copies of all of these drivers linked into |
| 63 | 86 | the Runtime Firmware binary. |
| 64 | 87 | |
| 65 | | -## Manifest-Based Image Authorization (new in 1.2) |
| 88 | +## Cryptographic Mailbox Commands (new in 2.0) |
| 89 | + |
| 90 | +Cryptographic mailbox (CM) commands are a flexible set of mailbox commands that provide access to Caliptra's cryptographic cabilities. |
| 91 | +This is meant for offloaded key storage and use, supporting protocols like SPDM and OCP LOCK. |
| 92 | + |
| 93 | +These commands are not meant to be high-performance as they are accessed via mailbox commands. |
| 94 | + |
| 95 | +CM itself does not provide any storage for the keys: when generated, they are returned to the caller in encrypted form, and must be passed back to be used. |
| 96 | + |
| 97 | +These mailbox commands provide SHA, HMAC, HKDF, AES, RNG, MLDSA, and ECDSA services. |
| 98 | + |
| 99 | +Note that while MLDSA and ECDSA keys can be imported, generated, and used in the cryptographic mailbox commands (i.e., `CM_*` commands) through CMKs, these keys are *NOT* tied DICE or DPE, so their use may be restricted for certain purposes. |
| 100 | + |
| 101 | +MLDSA and ECDSA keys managed by DPE use the separate `ECDSA384_SIGNATURE_VERIFY`, `LMS_SIGNATURE_VERIFY`, and `MLDSA87_SIGNATURE_VERIFY` mailbox commands, which do not use the cryptographic mailbox system and are not managed by CMKs. |
| 102 | + |
| 103 | + |
| 104 | +### References |
| 105 | + |
| 106 | +* [SPDM 1.3.1 (DSP0274)](https://www.dmtf.org/sites/default/files/standards/documents/DSP0274_1.3.1.pdf), dated 2024-07-01. |
| 107 | +* [OCP Attestation v1.1](https://docs.google.com/document/d/1wA0hbJdtCpcQ1NvsVsYr2IeCkwQbgC7e/edit) |
| 108 | +* [RFC 5869 (HKDF)](https://www.rfc-editor.org/rfc/rfc5869.html) |
| 109 | +* [RFC 8446](https://datatracker.ietf.org/doc/html/rfc8446) Section 7.4.2 & IEEE 1363 (TLS ECDH secret derivation) |
| 110 | + |
| 111 | +### Contexts |
| 112 | + |
| 113 | +Several of the methods, such as SHA and AES, support contexts so that multiple users can have in-flight requests at the same time. |
| 114 | + |
| 115 | +The contexts contain the internal structures necessary to resume operations to support data that may exceed the size of a single mailbox command. |
| 116 | + |
| 117 | +These contexts are intended to be opaque to the user, and SHALL be encrypted and authenticated if they contain sensitive internal data. |
| 118 | + |
| 119 | +### Keys |
| 120 | + |
| 121 | +Cryptographic Mailbox Key (CMKs) are used to store keys. Certain commands generate and return a new CMK. Most commands that use CMKs will also return a new CMK, as it is necessary to track CMKs so that they are not used beyond any relevant limits for their key type. |
| 122 | + |
| 123 | +They are returned from commands that generate keys and must be passed back to Caliptra to be used. These keys are encrypted and opaque to the mailbox caller. |
| 124 | + |
| 125 | +Internally, the unecrypted CMKs have the following structure: |
| 126 | + |
| 127 | +| **Name** | **Bits** | **Description** | |
| 128 | +| ------------- | -------- | -------------------------------------- | |
| 129 | +| version | 8 | CMK version. Currently always 1. | |
| 130 | +| flags | 8 | Bit 0 = FIPS valid | |
| 131 | +| length | 16 | how many bits of key material are used | |
| 132 | +| key usage | 8 | represents which kind of key this is | |
| 133 | +| id | 24 | ID number | |
| 134 | +| usage counter | 64 | how many times this key has been used | |
| 135 | +||| This MAY only be tracked for AES keys | |
| 136 | +| key material | 512 | bits used for the key material | |
| 137 | + |
| 138 | + |
| 139 | +The encrypted CMKs have the structure: |
| 140 | + |
| 141 | +| **Name** | **Bits** | **Description** | |
| 142 | +| --------------- | -------- | ------------------------------ | |
| 143 | +| domain | 32 | reserved | |
| 144 | +| domain metadata | 128 | reserved | |
| 145 | +| iv | 96 || |
| 146 | +| ciphertext | 640 | encrypted CMK data (see above) | |
| 147 | +| GCM tag | 128 || |
| 148 | + |
| 149 | + |
| 150 | +The total size of the CMK is therefore 128 bytes. |
| 151 | + |
| 152 | +Only the encrypted CMKs will appear in mailbox messages. |
| 153 | + |
| 154 | +The key used to encrypt the CMKs is randomized on reset, which means that CMKs cannot be used between resets. |
| 155 | +The IV is a randomized 1-up counter that is incremented for every key created. |
| 156 | + |
| 157 | +#### Key Usage |
| 158 | + |
| 159 | +The internal CMK structure and several commands use a key usage tag to specify how a key can be used: |
| 160 | + |
| 161 | +| **Value** | **Usage** | |
| 162 | +| --------- | --------- | |
| 163 | +| 0 | Reserved | |
| 164 | +| 1 | HMAC | |
| 165 | +| 2 | HKDF | |
| 166 | +| 3 | AES | |
| 167 | + |
| 168 | + |
| 169 | +#### Replay Prevention and Deletion |
| 170 | + |
| 171 | +To prevent replay attacks, Caliptra will have a small table that maps a CMK's internal ID to its last known usage counters. |
| 172 | +Whenever a CMK is used, this table is checked and updated. |
| 173 | + |
| 174 | +This is necessary for AES-256-GCM in particular to ensure that keys are only used a certain number of times, as per [NIST SP 800-38D, Section 8.3](https://doi.org/10.6028/NIST.SP.800-38D). |
| 175 | +Only AES-256-GCM keys need to be tracked in this table, but other keys MAY be tracked as well. |
| 176 | + |
| 177 | +This requires 96 bits of storage per AES-256-GCM key. These can stored as a sorted list in the DCCM. |
| 178 | + |
| 179 | +## Manifest-Based Image Authorization |
| 66 | 180 | |
| 67 | 181 | Caliptra's goal is to enable integrators to meet standard security requirements for creating cryptographic identity and securely reporting measurements through DICE and DPE Certificate chains and Caliptra-owned private-public key pairs. In addition, Caliptra 1.0 provides an `ECDSA384_SIGNATURE_VERIFY` command to enable an SoC RoT to verify its own FW signatures so that it can develop an SoC secure boot using Caliptra cryptography. Caliptra 1.1 expanded the verify command to a PQC-safe `LMS_SIGNATURE_VERIFY` command. In each of these cases, it is left up to the vendor to ensure that they build a secure environment for introducing and verifying FW integrity and authenticity and then executing mutable FW. |
| 68 | 182 | |
| @@ -73,7 +187,7 @@ |
| 73 | 187 | |
| 74 | 188 | Each of these abilities are tied to Caliptra Vendor and Owner FW signing keys and should be independent of any SoC RoT FW signing keys. |
| 75 | 189 | |
| 76 | | -Manifest-based image authorization is implemented via two mailbox commands: [`SET_AUTH_MANIFEST`](#set-auth-manifest) and [`AUTHORIZE_AND_STASH`](#authorize-and-stash). For image format of the manifest, please refer [this file](https://github.com/chipsalliance/caliptra-sw/blob/10d4f5891650a6ae38150cac3ffbbe220b7db8ac/auth-manifest/README.md). |
| 190 | +Manifest-based image authorization is implemented via three mailbox commands: [`SET_AUTH_MANIFEST`](#set-auth-manifest), [`SET_OWNER_AUTH_MANIFEST`](#set-owner-auth-manifest), and [`AUTHORIZE_AND_STASH`](#authorize-and-stash). A firmware ID identifies one platform firmware image and must be unique across the active vendor + owner and owner-only Image Metadata Collections. Both set commands reject a manifest containing an ID in the other active collection. `AUTHORIZE_AND_STASH` searches the vendor + owner collection first and then the owner-only collection; the provenance of the matching entry is reflected in its `auth_req_result` field. |
| 77 | 191 | |
| 78 | 192 | ### Caliptra-Endorsed Aggregated Measured Boot |
| 79 | 193 | |
| @@ -85,7 +199,7 @@ |
| 85 | 199 | |
| 86 | 200 | The Caliptra-Endorsed Local Verifier could be required by the owner only or both the vendor and the owner. |
| 87 | 201 | |
| 88 | | -The main difference between Caliptra-Endorsed Aggregated Measured Boot and Caliptra-Endorsed Local Verifier is whether the SoC RoT is relying on the Measurement Manifest for SoC Secure Boot services as opposed to using it as an additional verification. |
| 202 | +The main difference between Caliptra-Endorsed Aggregated Measured Boot and Caliptra-Endorsed Local Verifier is if the SoC RoT is relying on the Measurement Manifest for SoC Secure Boot services as opposed as using it as an additional verification. |
| 89 | 203 | |
| 90 | 204 | ### SoC RoT Enforcement of Measurement Manifest |
| 91 | 205 | |
| @@ -97,28 +211,30 @@ |
| 97 | 211 | |
| 98 | 212 | ### Unique Measurement Manifest Signing Keys |
| 99 | 213 | |
| 100 | | -In order to reduce usage of the Caliptra FW Signing keys, the measurement manifest will be signed by new key pairs: one for the owner and optionally one for the vendor. These new key pairs are endorsed once by the Caliptra FW signing keys, the signature being in the Measurement Manifest, thus allowing the measurement manifest keys to be used independently of the Caliptra FW signing keys. |
| 214 | +In order to reduce usage of the Caliptra FW Signing keys, the measurement manifest will be signed by new key pairs: one for the owner and possibly one for the vendor. These new key pairs are endorsed once using a single signature within the Measurement Manifest, thus allowing the measurement manifest keys to be used independently of the Caliptra FW signing keys. |
| 101 | 215 | |
| 102 | 216 | ### Caliptra Measurement Manifest Vendor Public Key Authenticity |
| 103 | 217 | |
| 104 | 218 | The Measurement Manifest MUST have an endorsement by the Caliptra Vendor Public Key. In order to fulfill this requirement, the Vendor has 2 options: |
| 105 | 219 | |
| 106 | | -* Vendor signing of `Image Metadata Collection` required: The Vendor creates a new Measurement keypair which will sign the measurement manifest and endorses this new public key with the Caliptra FW Vendor Private Key. The signature covers both the new public key as well as the flags field which indicates that the new Measurement Key Pair will be enforced. |
| 107 | | -* Vendor signing of `Image Metadata Collection` **not** required: Vendor leaves the Vendor public key as all zeros, and clears the flag which enforces vendor signing and then endorses these fields with a signature in the Measurement Manifest. In this case, the Vendor releases ownership of enforcing any specific FW in execution. |
| 220 | +* Vendor signing required: The Vendor creates a new Measurement keypair which will sign the measurement manifest and endorses the new public key with the Caliptra FW Vendor Private Key. The signature covers both the new public key as well as the flags field which indicates that the new Measurement Key Pair will be enforced. |
| 221 | +* Vendor signing **not** required: Vendor leaves the Vendor public key as all zeros, and clears the flag which enforces vendor signing and then endorses these fields with a signature in the Measurement Manifest. In this case, the Vendor releases ownership of enforcing any specific FW in execution. |
| 108 | 222 | |
| 109 | 223 | ### Caliptra Measurement Manifest Owner Public Key Authenticity |
| 110 | 224 | |
| 111 | 225 | Caliptra will always verify the endorsement of the Measurement Manifest Owner Public key and require that it signed the measurement manifest. |
| 112 | 226 | |
| 113 | | -This feature is accomplished by having the SoC send a manifest to Caliptra Runtime through the `SET_AUTH_MANIFEST` mailbox command. The manifest will include a set of hashes for the different SoC images. Later, the SOC will ask for authorization for its images from the Caliptra Runtime through the `AUTHORIZE_AND_STASH` new mailbox command. Caliptra Runtime will authorize the image based on whether its hash was contained in the manifest. |
| 227 | +This feature is accomplished by having the SoC send a manifest to Caliptra Runtime through the `SET_AUTH_MANIFEST` mailbox command. The manifest will include a set of hashes for the different SoC images. Later, the SOC will ask for authorization for its images from the Caliptra Runtime through the `AUTHORIZE_AND_STASH` new mailbox commands. Caliptra Runtime will authorize the image based on whether its hash was contained in the manifest. |
| 114 | 228 | |
| 115 | 229 | #### Preamble |
| 116 | 230 | |
| 117 | | -The manifest begins with the Preamble section, which contains new manifest ECC and LMS public keys of the vendor and the owner. These public keys correspond to the private keys that sign the Image Metadata Collection (IMC) section. These signatures are included in the Preamble. The Caliptra firmware's private keys endorse the manifest's public keys and these endorsements (i.e., signatures) are part of the Preamble as well. |
| 231 | +The manifest begins with the Preamble section, which contains new manifest ECC and either MLDSA or LMS public keys of the vendor and the owner. These public keys correspond to the private keys that sign the Image Metadata Collection (IMC) section. These signatures are included in the Preamble. The Caliptra firmware's private keys endorse the manifest's public keys and these endorsements (i.e., signatures) are part of the Preamble as well. |
| 118 | 232 | |
| 119 | 233 | #### Image Metadata Collection (IMC) |
| 120 | 234 | |
| 121 | 235 | The IMC is a collection of Image Metadata entries (IME). Each IME has a hash that matches one of the multiple SoC images. The manifest vendor and owner private keys sign the IMC. The Preamble holds the IMC signatures. The manifest IMC vendor signatures are optional and are validated only if the Flags field Bit 0 is set to 1. Up to 127 image hashes will be supported. |
| 236 | + |
| 237 | +An authorization manifest may set the vendor-signed `DEBUG_IMAGE` flag to identify a vendor-authorized debug manifest. `DEBUG_IMAGE` requires `VENDOR_SIGNATURE_REQUIRED`, subsystem mode, asserted `SS_DEBUG_INTENT`, and clear `SS_STRAP_GENERIC[3][31]` (`DISABLE_VENDOR_DEBUG_IMAGES`). Runtime evaluates this policy only after authenticating the firmware-vendor-signed preamble fields. Existing owner endorsement and IMC signature verification remain required. |
| 122 | 238 | |
| 123 | 239 | #### Caliptra Measurement Manifest Keys Endorsement Verification Steps |
| 124 | 240 | |
| @@ -133,6 +249,10 @@ |
| 133 | 249 | * If the owner endorsement is invalid, the `SET_AUTH_MANIFEST` command will be rejected. |
| 134 | 250 | * Otherwise, the owner public key will be trusted and Caliptra will use it to verify the overall measurement manifest. |
| 135 | 251 | |
| 252 | +#### Measurement Manifest Version Number |
| 253 | + |
| 254 | +A Measurement Manifest VN is used to ensure that some enforcement is possible if a progression of measurements is required. 32 bits of the existing unused `IDEVID_MANUF_IDENTIFIER` fuse (128 bits) can be repurposed for this. This can be accomplished by updating Caliptra's main specification to redefine the fuse definition and its usage from "Programming time" to "Field Programmable". |
| 255 | + |
| 136 | 256 | ### Image Authorization Sequence |
| 137 | 257 | |
| 138 | 258 | The diagram below illustrates how this feature is part of the Caliptra boot flow, and the order of operations needed to use the feature. |
| @@ -143,7 +263,7 @@ |
| 143 | 263 | FMC->>Runtime: Launch RT |
| 144 | 264 | Runtime->>SOC: RDY_FOR_RT |
| 145 | 265 | Note over Runtime,SOC: Manifest Load |
| 146 | | - SOC->>Runtime: SET_AUTH_MANIFEST |
| 266 | + SOC->>Runtime: SET_MANIFEST |
| 147 | 267 | Runtime-->>SOC: Success/Failure |
| 148 | 268 | Note over Runtime,SOC: Image Authorization |
| 149 | 269 | loop n times |
| @@ -161,14 +281,19 @@ |
| 161 | 281 | |
| 162 | 282 | *Table: Mailbox command result codes* |
| 163 | 283 | |
| 164 | | -| **Name** | **Value** | Description |
| 165 | | -| ------- | ----- | ----------- |
| 166 | | -| `SUCCESS` | `0x0000_0000` | Mailbox command succeeded |
| 167 | | -| `BAD_VENDOR_SIG` | `0x5653_4947` ("VSIG") | Vendor signature check failed |
| 168 | | -| `BAD_OWNER_SIG` | `0x4F53_4947` ("OSIG") | Owner signature check failed |
| 169 | | -| `BAD_SIG` | `0x4253_4947` ("BSIG") | Generic signature check failure (for crypto offload) |
| 170 | | -| `BAD_IMAGE` | `0x4249_4D47` ("BIMG") | Malformed input image |
| 171 | | -| `BAD_CHKSUM` | `0x4243_484B` ("BCHK") | Checksum check failed on input arguments |
| 284 | +| **Name** | **Value** | Description | |
| 285 | +| ---------------- | ---------------------- | ---------------------------------------------------- | |
| 286 | +| `SUCCESS` | `0x0000_0000` | Mailbox command succeeded | |
| 287 | +| `BAD_VENDOR_SIG` | `0x5653_4947` ("VSIG") | Vendor signature check failed | |
| 288 | +| `BAD_OWNER_SIG` | `0x4F53_4947` ("OSIG") | Owner signature check failed | |
| 289 | +| `BAD_SIG` | `0x4253_4947` ("BSIG") | Generic signature check failure (for crypto offload) | |
| 290 | +| `BAD_IMAGE` | `0x4249_4D47` ("BIMG") | Malformed input image | |
| 291 | +| `BAD_CHKSUM` | `0x4243_484B` ("BCHK") | Checksum check failed on input arguments | |
| 292 | +| `CME_BAD_CMK` | `0x434D_424B` ("CMBK") | Invalid CMK | |
| 293 | +| `CME_CMK_OFLW` | `0x434D_424F` ("CMBO") | CMK has been used too many times | |
| 294 | +| `CME_BAD_CTXT` | `0x434D_4243` ("CMBC") | Bad context | |
| 295 | +| `CME_FULL` | `0x434D_4546` ("CMEF") | Too many Cryptographic Mailbox usage counters in use | |
| 296 | + |
| 172 | 297 | |
| 173 | 298 | Relevant registers: |
| 174 | 299 | |
| @@ -177,115 +302,60 @@ |
| 177 | 302 | * CPTRA\_FW\_ERROR\_NON\_FATAL: Status code of mailbox command. Any result |
| 178 | 303 | other than `SUCCESS` signifies a mailbox command failure. |
| 179 | 304 | |
| 180 | | -### Mailbox command privilege levels |
| 181 | | - |
| 182 | | -Mailbox commands maintain the PL information of their caller and can allow or |
| 183 | | -disallow clients from invoking a call based on their PL level. Callers are |
| 184 | | -classified as PL0 or PL1 by comparing the mailbox PAUSER against the `pl0_pauser` |
| 185 | | -field of the signed firmware image header; see [PAUSER privilege levels](#pauser-privilege-levels). |
| 186 | | - |
| 187 | | -A command marked `PL0` is rejected outright for PL1 callers. A command marked |
| 188 | | -`PL0 or PL1` is available to every caller. `INVOKE_DPE_COMMAND` and |
| 189 | | -`INVOKE_DPE_MLDSA87` are available to both levels, but restrict a subset of the |
| 190 | | -DPE commands they carry to PL0. |
| 191 | | - |
| 192 | | -If the PL0 PAUSER flag is not set in the firmware image header, no caller is |
| 193 | | -PL0, so every PL0 command is unavailable for that firmware image. Independently |
| 194 | | -of privilege level, commands from the reserved PAUSER are rejected outright. |
| 195 | | - |
| 196 | | -Privilege level is not the only caller-dependent restriction. Commands that |
| 197 | | -operate on DPE contexts are also scoped by locality, and PAUSER maps 1:1 to |
| 198 | | -locality, so a caller can generally only reach the contexts it created. The |
| 199 | | -`PL0-only functionality` column below calls out where that matters. |
| 200 | | - |
| 201 | | -*Table: Mailbox command privilege levels* |
| 202 | | - |
| 203 | | -| **Command** | **Privilege Level** | **PL0-only functionality** |
| 204 | | -| ----------- | ------------------- | -------------------------- |
| 205 | | -| `CALIPTRA_FW_LOAD` | PL0 or PL1 | |
| 206 | | -| `CAPABILITIES` | PL0 or PL1 | |
| 207 | | -| `GET_IDEV_CERT` | PL0 or PL1 | |
| 208 | | - |
| 209 | | -| `POPULATE_IDEV_CERT` | PL0 | Entire command |
| 210 | | -| `GET_IDEV_INFO` | PL0 or PL1 | |
| 211 | | -| `GET_LDEV_CERT` | PL0 or PL1 | |
| 212 | | -| `GET_FMC_ALIAS_CERT` | PL0 or PL1 | |
| 213 | | -| `GET_RT_ALIAS_CERT` | PL0 or PL1 | |
| 214 | | -| `ECDSA384_SIGNATURE_VERIFY` | PL0 or PL1 | |
| 215 | | -| `LMS_SIGNATURE_VERIFY` | PL0 or PL1 | |
| 216 | | -| `MLDSA87_SIGNATURE_VERIFY` | PL0 or PL1 | |
| 217 | | - |
| 218 | | -| `STASH_MEASUREMENT` | PL0 | Entire command |
| 219 | | -| `DISABLE_ATTESTATION` | PL0 | Entire command |
| 220 | | -| `INVOKE_DPE_COMMAND` | PL0 or PL1 | `CertifyKey` with `format=X509`; `DeriveContext` with the `export-cdi` flag; `DeriveContext` with `change-locality` targeting the PL0 PAUSER |
| 221 | | -| `QUOTE_PCRS` | PL0 or PL1 | |
| 222 | | -| `EXTEND_PCR` | PL0 or PL1 | |
| 223 | | -| `GET_PCR_LOG` | PL0 or PL1 | |
| 224 | | -| `INCREMENT_PCR_RESET_COUNTER` | PL0 or PL1 | |
| 225 | | - |
| 226 | | -| `DPE_TAG_TCI` | PL0 or PL1 | Tags only contexts in the caller's own locality, so PL1 cannot tag a PL0 context (and vice versa) |
| 227 | | -| `DPE_GET_TAGGED_TCI` | PL0 or PL1 | Looks up by tag only; either level can read any tagged TCI |
| 228 | | -| `FW_INFO` | PL0 or PL1 | |
| 229 | | -| `VERSION` | PL0 or PL1 | |
| 230 | | -| `SELF_TEST_START` | PL0 or PL1 | |
| 231 | | -| `SELF_TEST_GET_RESULTS` | PL0 or PL1 | |
| 232 | | -| `SHUTDOWN` | PL0 or PL1 | |
| 233 | | -| `ADD_SUBJECT_ALT_NAME` | PL0 or PL1 | |
| 234 | | - |
| 235 | | -| `CERTIFY_KEY_EXTENDED` | PL0 | Entire command |
| 236 | | -| `SET_AUTH_MANIFEST` | PL0 | Entire command |
| 237 | | -| `AUTHORIZE_AND_STASH` | PL0 or PL1 | Stashing the measurement. A PL1 caller must set the `SKIP_STASH` flag; otherwise an authorized image fails when the measurement is stashed into DPE |
| 238 | | -| `GET_IDEVID_CSR` | PL0 or PL1 | |
| 239 | | -| `GET_FMC_ALIAS_CSR` | PL0 or PL1 | |
| 240 | | - |
| 241 | | -| `SIGN_WITH_EXPORTED_ECDSA` | PL0 | Entire command |
| 242 | | -| `REVOKE_EXPORTED_CDI_HANDLE` | PL0 | Entire command |
| 243 | | -| `REALLOCATE_DPE_CONTEXT_LIMITS` | PL0 | Entire command |
| 244 | | -| `SET_PQ_SEED` | PL0 | Entire command |
| 245 | | -| `GET_PQ_CSR` | PL0 or PL1 | |
| 246 | | -| `GET_PQ_INFO` | PL0 or PL1 | |
| 247 | | - |
| 248 | | -| `POPULATE_PQ_CERT` | PL0 | Entire command |
| 249 | | -| `GET_PQ_CERT` | PL0 or PL1 | |
| 250 | | - |
| 251 | | -| `INVOKE_DPE_MLDSA87` | PL0 or PL1 | Same DPE command restrictions as `INVOKE_DPE_COMMAND` |
| 252 | | -| `CERTIFY_KEY_EXTENDED_MLDSA87` | PL0 | Entire command |
| 253 | | -| `SIGN_WITH_EXPORTED_MLDSA` | PL0 | Entire command |
| 254 | | - |
| 255 | | -### CALIPTRA\_FW\_LOAD |
| 256 | | - |
| 257 | | -The `CALIPTRA_FW_LOAD` command is handled by both ROM and Runtime Firmware. |
| 305 | +Mailbox user 0xFFFF_FFFF is reserved for Caliptra internal use. All mailbox |
| 306 | +commands from that user will fail. |
| 307 | + |
| 308 | +### FW\_LOAD |
| 309 | + |
| 310 | +The `FIRMWARE_LOAD` command is handled by both ROM and Runtime Firmware. |
| 258 | 311 | |
| 259 | 312 | #### ROM behavior |
| 260 | 313 | |
| 261 | | -On cold boot, ROM exposes the `CALIPTRA_FW_LOAD` mailbox command to accept |
| 314 | +On cold boot, ROM exposes the `FIRMWARE_LOAD` mailbox command to accept |
| 262 | 315 | the firmware image that ROM will boot. This image includes Manifest, FMC, and Runtime |
| 263 | 316 | firmware. |
| 264 | 317 | |
| 265 | 318 | #### Runtime Firmware behavior |
| 266 | 319 | |
| 267 | | -Caliptra Runtime Firmware also exposes the `CALIPTRA_FW_LOAD` mailbox command for loading |
| 320 | +Caliptra Runtime Firmware also exposes the `FIRMWARE_LOAD` mailbox command for loading |
| 268 | 321 | impactless updates. For more information, see [Runtime Firmware updates](#runtime-firmware-updates). |
| 269 | 322 | |
| 270 | 323 | Command Code: `0x4657_4C44` ("FWLD") |
| 271 | 324 | |
| 272 | | -Privilege Level: PL0 or PL1 |
| 273 | | - |
| 274 | | -*Table: `CALIPTRA_FW_LOAD` input arguments* |
| 325 | +*Table: `FIRMWARE_LOAD` input arguments* |
| 275 | 326 | |
| 276 | 327 | | **Name** | **Type** | **Description** |
| 277 | 328 | | -------- | -------- | --------------- |
| 278 | 329 | | data | u8[...] | Firmware image to load. |
| 279 | 330 | |
| 280 | | -`CALIPTRA_FW_LOAD` returns no output arguments. |
| 331 | +`FIRMWARE_LOAD` returns no output arguments. |
| 332 | + |
| 333 | +### FIRMWARE\_VERIFY |
| 334 | + |
| 335 | +The `FIRMWARE_VERIFY` command is used to verify a Caliptra Firmware Bundle. |
| 336 | + |
| 337 | +Command Code: `0x4657_5652` ("FWVR") |
| 338 | + |
| 339 | +*Table: `FIRMWARE_VERIFY` input arguments* |
| 340 | + |
| 341 | +| **Name** | **Type** | **Description** |
| 342 | +| -------- | -------- | --------------- |
| 343 | +| data | u8[...] | Firmware image bundle to verify. |
| 344 | + |
| 345 | +*Table: `FIRMWARE_VERIFY` output arguments* |
| 346 | + |
| 347 | +| **Name** | **Type** | **Description** | |
| 348 | +| -------------- | -------------- | -------------------------------------------------------------------------- | |
| 349 | +| chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. | |
| 350 | +| fips_status | u32 | Indicates if the command is FIPS approved or an error. | |
| 351 | +| verify_result | u32 | VERIFY_SUCCESS (0xDEADC0DE), VERIFY_FAILED (0x21523F21) | |
| 352 | + |
| 281 | 353 | |
| 282 | 354 | ### CAPABILITIES |
| 283 | 355 | |
| 284 | 356 | Exposes a command to retrieve firmware capabilities |
| 285 | 357 | |
| 286 | 358 | Command Code: `0x4341_5053` ("CAPS") |
| 287 | | - |
| 288 | | -Privilege Level: PL0 or PL1 |
| 289 | 359 | |
| 290 | 360 | *Table: `CAPABILITIES` input arguments* |
| 291 | 361 | |
| @@ -301,15 +371,13 @@ |
| 301 | 371 | | fips\_status | u32 | Indicates if the command is FIPS approved or an error. |
| 302 | 372 | | capabilities | u8[16] | Firmware capabilities |
| 303 | 373 | |
| 304 | | -### GET\_IDEV\_CERT |
| 305 | | - |
| 306 | | -Exposes a command to reconstruct the IDEVID CERT. |
| 374 | +### GET\_IDEV\_ECC384\_CERT |
| 375 | + |
| 376 | +Exposes a command to reconstruct the ECC384 IDEV CERT. |
| 307 | 377 | |
| 308 | 378 | Command Code: `0x4944_4543` ("IDEC") |
| 309 | 379 | |
| 310 | | -Privilege Level: PL0 or PL1 |
| 311 | | - |
| 312 | | -*Table: `GET_IDEV_CERT` input arguments* |
| 380 | +*Table: `GET_IDEV_ECC384_CERT` input arguments* |
| 313 | 381 | |
| 314 | 382 | | **Name** | **Type** | **Description** |
| 315 | 383 | | -------- | -------- | --------------- |
| @@ -319,55 +387,98 @@ |
| 319 | 387 | | tbs\_size | u32 | Size of the TBS. |
| 320 | 388 | | tbs | u8[916] | TBS, with a maximum size of 916. Only bytes up to tbs_size are used. |
| 321 | 389 | |
| 322 | | -*Table: `GET_IDEV_CERT` output arguments* |
| 390 | +*Table: `GET_IDEV_ECC384_CERT` output arguments* |
| 323 | 391 | |
| 324 | 392 | | **Name** | **Type** | **Description** |
| 325 | 393 | | -------- | -------- | --------------- |
| 326 | 394 | | chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. |
| 327 | 395 | | fips\_status | u32 | Indicates if the command is FIPS approved or an error. |
| 328 | | -| cert\_size | u32 | Length in bytes of the cert field in use for the IDevId certificate. |
| 329 | | -| cert | u8[1024] | DER-encoded IDevID CERT. |
| 330 | | - |
| 331 | | -### POPULATE\_IDEV\_CERT |
| 396 | +| cert\_size | u32 | Length in bytes of the cert field in use for the IDev ECC384 certificate. |
| 397 | +| cert | u8[1024] | DER-encoded IDev ECC384 CERT. |
| 398 | + |
| 399 | +### GET\_IDEV\_MLDSA87\_CERT |
| 400 | + |
| 401 | +Exposes a command to reconstruct the MLDSA87 IDEV CERT. |
| 402 | + |
| 403 | +Command Code: `0x4944_4D43` ("IDMC") |
| 404 | + |
| 405 | +*Table: `GET_IDEV_MLDSA87_CERT` input arguments* |
| 406 | + |
| 407 | +| **Name** | **Type** | **Description** |
| 408 | +| -------- | -------- | --------------- |
| 409 | +| chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. |
| 410 | +| tbs\_size | u32 | Size of the TBS. |
| 411 | +| signature | u8[4628] | MLDSA87 signature bytes. |
| 412 | +| tbs | u8[2820] | TBS, with a maximum size of 2820. Only bytes up to tbs_size are used. |
| 413 | + |
| 414 | +*Table: `GET_IDEV_MLDSA87_CERT` output arguments* |
| 415 | + |
| 416 | +| **Name** | **Type** | **Description** |
| 417 | +| -------- | -------- | --------------- |
| 418 | +| chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. |
| 419 | +| fips\_status | u32 | Indicates if the command is FIPS approved or an error. |
| 420 | +| cert\_size | u32 | Length in bytes of the cert field in use for the IDev MLDSA87 certificate. |
| 421 | +| cert | u8[...] | DER-encoded IDev MLDSA87 CERT. |
| 422 | + |
| 423 | +### POPULATE\_IDEV\_ECC384\_CERT |
| 332 | 424 | |
| 333 | 425 | Exposes a command that allows the SoC to provide a DER-encoded |
| 334 | | -IDevId certificate on every boot. The IDevId certificate is added |
| 426 | +ECC384 IDev certificate on every boot. The ECC384 IDev certificate is added |
| 335 | 427 | to the start of the certificate chain. |
| 336 | 428 | |
| 337 | 429 | Command Code: `0x4944_4550` ("IDEP") |
| 338 | 430 | |
| 339 | | -Privilege Level: PL0 |
| 340 | | - |
| 341 | | -*Table: `POPULATE_IDEV_CERT` input arguments* |
| 431 | +*Table: `POPULATE_IDEV_ECC384_CERT` input arguments* |
| 342 | 432 | |
| 343 | 433 | | **Name** | **Type** | **Description** |
| 344 | 434 | | -------- | -------- | --------------- |
| 345 | 435 | | chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. |
| 346 | | -| cert\_size | u32 | Size of the DER-encoded IDevId certificate. |
| 347 | | -| cert | u8[1024] | DER-encoded IDevID CERT. |
| 348 | | - |
| 349 | | -*Table: `POPULATE_IDEV_CERT` output arguments* |
| 436 | +| cert\_size | u32 | Size of the DER-encoded ECC384 IDevId certificate. |
| 437 | +| cert | u8[1024] | DER-encoded ECC384 IDev CERT. |
| 438 | + |
| 439 | +*Table: `POPULATE_IDEV_ECC384_CERT` output arguments* |
| 350 | 440 | |
| 351 | 441 | | **Name** | **Type** | **Description** |
| 352 | 442 | | -------- | -------- | --------------- |
| 353 | 443 | | chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. |
| 354 | 444 | | fips\_status | u32 | Indicates if the command is FIPS approved or an error. |
| 355 | 445 | |
| 356 | | -### GET\_IDEV\_INFO |
| 357 | | - |
| 358 | | -Exposes a command to get an IDEVID public key. |
| 446 | +### POPULATE\_IDEV\_MLDSA87\_CERT |
| 447 | + |
| 448 | +Exposes a command that allows the SoC to provide a DER-encoded |
| 449 | +MLDSA87 IDev certificate on every boot. The MLDSA87 IDev certificate is added |
| 450 | +to the start of the certificate chain. |
| 451 | + |
| 452 | +Command Code: `0x4944_4D50` ("IDMP") |
| 453 | + |
| 454 | +*Table: `POPULATE_IDEV_MLDSA87_CERT` input arguments* |
| 455 | + |
| 456 | +| **Name** | **Type** | **Description** |
| 457 | +| -------- | -------- | --------------- |
| 458 | +| chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. |
| 459 | +| cert\_size | u32 | Size of the DER-encoded MLDSA87 IDev certificate. |
| 460 | +| cert | u8[8192] | DER-encoded MLDSA87 IDev CERT. |
| 461 | + |
| 462 | +*Table: `POPULATE_IDEV_MLDSA87_CERT` output arguments* |
| 463 | + |
| 464 | +| **Name** | **Type** | **Description** |
| 465 | +| -------- | -------- | --------------- |
| 466 | +| chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. |
| 467 | +| fips\_status | u32 | Indicates if the command is FIPS approved or an error. |
| 468 | + |
| 469 | +### GET\_IDEV\_ECC384\_INFO |
| 470 | + |
| 471 | +Exposes a command to get the IDEVID ECC384 public key. |
| 359 | 472 | |
| 360 | 473 | Command Code: `0x4944_4549` ("IDEI") |
| 361 | 474 | |
| 362 | | -Privilege Level: PL0 or PL1 |
| 363 | | - |
| 364 | | -*Table: `GET_IDEV_INFO` input arguments* |
| 475 | +*Table: `GET_IDEV_ECC384_INFO` input arguments* |
| 365 | 476 | |
| 366 | 477 | | **Name** | **Type** | **Description** |
| 367 | 478 | | -------- | -------- | --------------- |
| 368 | 479 | | chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. |
| 369 | 480 | |
| 370 | | -*Table: `GET_IDEV_INFO` output arguments* |
| 481 | +*Table: `GET_IDEV_ECC384_INFO` output arguments* |
| 371 | 482 | |
| 372 | 483 | | **Name** | **Type** | **Description** |
| 373 | 484 | | -------- | -------- | --------------- |
| @@ -376,86 +487,160 @@ |
| 376 | 487 | | idev\_pub\_x | u8[48] | X portion of ECDSA IDevId key. |
| 377 | 488 | | idev\_pub\_y | u8[48] | Y portion of ECDSA IDevId key. |
| 378 | 489 | |
| 379 | | -### GET\_LDEV\_CERT |
| 380 | | - |
| 381 | | -Exposes a command to get an LDevID certificate signed by IDevID. |
| 382 | | - |
| 383 | | -Command Code: `0x4C44_4556` ("LDEV") |
| 384 | | - |
| 385 | | -Privilege Level: PL0 or PL1 |
| 386 | | - |
| 387 | | -*Table: `GET_LDEV_CERT` input arguments* |
| 490 | +### GET\_IDEV\_MLDSA87\_INFO |
| 491 | + |
| 492 | +Exposes a command to get the IDEVID MLDSA87 public key. |
| 493 | + |
| 494 | +Command Code: `0x4944_4D49` ("IDMI") |
| 495 | + |
| 496 | +*Table: `GET_IDEV_MLDSA87_INFO` input arguments* |
| 388 | 497 | |
| 389 | 498 | | **Name** | **Type** | **Description** |
| 390 | 499 | | -------- | -------- | --------------- |
| 391 | 500 | | chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. |
| 392 | 501 | |
| 393 | | -*Table: `GET_LDEV_CERT` output arguments* |
| 502 | +*Table: `GET_IDEV_MLDSA87_INFO` output arguments* |
| 503 | + |
| 504 | +| **Name** | **Type** | **Description** |
| 505 | +| -------- | -------- | --------------- |
| 506 | +| chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. |
| 507 | +| fips\_status | u32 | Indicates if the command is FIPS approved or an error. |
| 508 | +| idev\_pub\_key | u8[2592] | MLDSA IDevId public key. |
| 509 | + |
| 510 | +### GET\_LDEV\_ECC384\_CERT |
| 511 | + |
| 512 | +Exposes a command to get an LDevID ECC384 certificate signed by ECC384 IDevID private key. |
| 513 | + |
| 514 | +Command Code: `0x4C44_4556` ("LDEV") |
| 515 | + |
| 516 | +*Table: `GET_LDEV_ECC384_CERT` input arguments* |
| 517 | + |
| 518 | +| **Name** | **Type** | **Description** |
| 519 | +| -------- | -------- | --------------- |
| 520 | +| chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. |
| 521 | + |
| 522 | +*Table: `GET_LDEV_ECC384_CERT` output arguments* |
| 394 | 523 | |
| 395 | 524 | | **Name** | **Type** | **Description** |
| 396 | 525 | | -------- | -------- | --------------- |
| 397 | 526 | | chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. |
| 398 | 527 | | fips\_status | u32 | Indicates if the command is FIPS approved or an error. |
| 399 | 528 | | data\_size | u32 | Length in bytes of the valid data in the data field. |
| 400 | | -| data | u8[...] | DER-encoded LDevID certificate. |
| 401 | | - |
| 402 | | -### GET\_FMC\_ALIAS\_CERT |
| 403 | | - |
| 404 | | -Exposes a command to get an FMC alias certificate signed by LDevID. |
| 405 | | - |
| 406 | | -Command Code: `0x4345_5246` ("CERF") |
| 407 | | - |
| 408 | | -Privilege Level: PL0 or PL1 |
| 409 | | - |
| 410 | | -*Table: `GET_FMC_ALIAS_CERT` input arguments* |
| 529 | +| data | u8[...] | DER-encoded ECC384 LDevID certificate. |
| 530 | + |
| 531 | +### GET\_LDEV\_MLDSA87\_CERT |
| 532 | + |
| 533 | +Exposes a command to get an LDevID MLDSA87 certificate signed by MLDSA87 IDevID private key. |
| 534 | + |
| 535 | +Command Code: `0x4C44_4D43` ("LDMC") |
| 536 | + |
| 537 | +*Table: `GET_LDEV_MLDSA87_CERT` input arguments* |
| 411 | 538 | |
| 412 | 539 | | **Name** | **Type** | **Description** |
| 413 | 540 | | -------- | -------- | --------------- |
| 414 | 541 | | chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. |
| 415 | 542 | |
| 416 | | -*Table: `GET_FMC_ALIAS_CERT` output arguments* |
| 543 | +*Table: `GET_LDEV_MLDSA87_CERT` output arguments* |
| 417 | 544 | |
| 418 | 545 | | **Name** | **Type** | **Description** |
| 419 | 546 | | -------- | -------- | --------------- |
| 420 | 547 | | chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. |
| 421 | 548 | | fips\_status | u32 | Indicates if the command is FIPS approved or an error. |
| 422 | 549 | | data\_size | u32 | Length in bytes of the valid data in the data field. |
| 423 | | -| data | u8[...] | DER-encoded FMC alias certificate. |
| 424 | | - |
| 425 | | -### GET\_RT\_ALIAS\_CERT |
| 426 | | - |
| 427 | | -Exposes a command to get a Runtime alias certificate signed by the FMC alias. |
| 428 | | - |
| 429 | | -Command Code: `0x4345_5252` ("CERR") |
| 430 | | - |
| 431 | | -Privilege Level: PL0 or PL1 |
| 432 | | - |
| 433 | | -*Table: `GET_RT_ALIAS_CERT` input arguments* |
| 550 | +| data | u8[...] | DER-encoded MLDSA87 LDevID certificate. |
| 551 | + |
| 552 | +### GET\_FMC\_ALIAS\_ECC384\_CERT |
| 553 | + |
| 554 | +Exposes a command to get a FMC alias ECC384 certificate signed by the ECC384 LDevID private key. |
| 555 | + |
| 556 | +Command Code: `0x4345_5246` ("CERF") |
| 557 | + |
| 558 | +*Table: `GET_FMC_ALIAS_ECC384_CERT` input arguments* |
| 434 | 559 | |
| 435 | 560 | | **Name** | **Type** | **Description** |
| 436 | 561 | | -------- | -------- | --------------- |
| 437 | 562 | | chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. |
| 438 | 563 | |
| 439 | | -*Table: `GET_RT_ALIAS_CERT` output arguments* |
| 564 | +*Table: `GET_FMC_ALIAS_ECC384_CERT` output arguments* |
| 440 | 565 | |
| 441 | 566 | | **Name** | **Type** | **Description** |
| 442 | 567 | | -------- | -------- | --------------- |
| 443 | 568 | | chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. |
| 444 | 569 | | fips\_status | u32 | Indicates if the command is FIPS approved or an error. |
| 445 | 570 | | data\_size | u32 | Length in bytes of the valid data in the data field. |
| 446 | | -| data | u8[...] | DER-encoded Runtime alias certificate. |
| 571 | +| data | u8[...] | DER-encoded FMC alias ECC384 certificate. |
| 572 | + |
| 573 | +### GET\_FMC\_ALIAS\_MLDSA87\_CERT |
| 574 | + |
| 575 | +Exposes a command to get a FMC alias MLDSA87 certificate signed by the MLDSA87 LDevID private key. |
| 576 | + |
| 577 | +Command Code: `0x434D_4346` ("CMCF") |
| 578 | + |
| 579 | +*Table: `GET_FMC_ALIAS_MLDSA87_CERT` input arguments* |
| 580 | + |
| 581 | +| **Name** | **Type** | **Description** |
| 582 | +| -------- | -------- | --------------- |
| 583 | +| chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. |
| 584 | + |
| 585 | +*Table: `GET_FMC_ALIAS_MLDSA87_CERT` output arguments* |
| 586 | + |
| 587 | +| **Name** | **Type** | **Description** |
| 588 | +| -------- | -------- | --------------- |
| 589 | +| chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. |
| 590 | +| fips\_status | u32 | Indicates if the command is FIPS approved or an error. |
| 591 | +| data\_size | u32 | Length in bytes of the valid data in the data field. |
| 592 | +| data | u8[...] | DER-encoded FMC alias MLDSA87 certificate. |
| 593 | + |
| 594 | +### GET\_RT\_ALIAS\_ECC384\_CERT |
| 595 | + |
| 596 | +Exposes a command to get a Runtime alias ECC384 certificate signed by the ECC384 FMC alias private key. |
| 597 | + |
| 598 | +Command Code: `0x4345_5252` ("CERR") |
| 599 | + |
| 600 | +*Table: `GET_RT_ALIAS_ECC384_CERT` input arguments* |
| 601 | + |
| 602 | +| **Name** | **Type** | **Description** |
| 603 | +| -------- | -------- | --------------- |
| 604 | +| chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. |
| 605 | + |
| 606 | +*Table: `GET_RT_ALIAS_ECC384_CERT` output arguments* |
| 607 | + |
| 608 | +| **Name** | **Type** | **Description** |
| 609 | +| -------- | -------- | --------------- |
| 610 | +| chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. |
| 611 | +| fips\_status | u32 | Indicates if the command is FIPS approved or an error. |
| 612 | +| data\_size | u32 | Length in bytes of the valid data in the data field. |
| 613 | +| data | u8[...] | DER-encoded Runtime alias ECC384 certificate. |
| 614 | + |
| 615 | +### GET\_RT\_ALIAS\_MLDSA87\_CERT |
| 616 | + |
| 617 | +Exposes a command to get a Runtime alias MLDSA87 certificate signed by the MLDSA87 FMC alias private key. |
| 618 | + |
| 619 | +Command Code: `0x434D_4352` ("CMCR") |
| 620 | + |
| 621 | +*Table: `GET_RT_ALIAS_MLDSA87_CERT` input arguments* |
| 622 | + |
| 623 | +| **Name** | **Type** | **Description** |
| 624 | +| -------- | -------- | --------------- |
| 625 | +| chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. |
| 626 | + |
| 627 | +*Table: `GET_RT_ALIAS_MLDSA87_CERT` output arguments* |
| 628 | + |
| 629 | +| **Name** | **Type** | **Description** |
| 630 | +| -------- | -------- | --------------- |
| 631 | +| chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. |
| 632 | +| fips\_status | u32 | Indicates if the command is FIPS approved or an error. |
| 633 | +| data\_size | u32 | Length in bytes of the valid data in the data field. |
| 634 | +| data | u8[...] | DER-encoded Runtime alias MLDSA87 certificate. |
| 447 | 635 | |
| 448 | 636 | ### ECDSA384\_SIGNATURE\_VERIFY |
| 449 | 637 | |
| 450 | | -Verifies an ECDSA P-384 signature. The hash to be verified is taken from |
| 451 | | -Caliptra's SHA384 accelerator peripheral. |
| 638 | +Verifies an ECDSA P-384 signature. The hash to be verified is taken from the input (new in 2.0). |
| 452 | 639 | |
| 453 | 640 | In the event of an invalid signature, the mailbox command will report CMD_FAILURE |
| 454 | 641 | and the cause will be logged as a non-fatal error. |
| 455 | 642 | |
| 456 | | -Command Code: `0x5349_4756` ("SIGV") |
| 457 | | - |
| 458 | | -Privilege Level: PL0 or PL1 |
| 643 | +Command Code: `0x4543_5632` ("ECV2") |
| 459 | 644 | |
| 460 | 645 | *Table: `ECDSA384_SIGNATURE_VERIFY` input arguments* |
| 461 | 646 | |
| @@ -466,6 +651,7 @@ |
| 466 | 651 | | pub\_key\_y | u8[48] | Y portion of ECDSA verification key. |
| 467 | 652 | | signature\_r | u8[48] | R portion of signature to verify. |
| 468 | 653 | | signature\_s | u8[48] | S portion of signature to verify. |
| 654 | +| hash | u8[48] | SHA384 digest to verify. |
| 469 | 655 | |
| 470 | 656 | *Table: `ECDSA384_SIGNATURE_VERIFY` output arguments* |
| 471 | 657 | |
| @@ -476,8 +662,7 @@ |
| 476 | 662 | |
| 477 | 663 | ### LMS\_SIGNATURE\_VERIFY |
| 478 | 664 | |
| 479 | | -Verifies an LMS signature. The hash to be verified is taken from |
| 480 | | -Caliptra's SHA384 accelerator peripheral. |
| 665 | +Verifies an LMS signature. The hash to be verified is taken from the input (new in 2.0). |
| 481 | 666 | |
| 482 | 667 | In the event of an invalid signature, the mailbox command will report CMD_FAILURE |
| 483 | 668 | and the cause will be logged as a non-fatal error. |
| @@ -492,9 +677,7 @@ |
| 492 | 677 | | w | 4 | Width (in bits) of the Winternitz coefficient |
| 493 | 678 | | h | 15 | Height of the tree |
| 494 | 679 | |
| 495 | | -Command Code: `0x4C4D_5356` ("LMSV") |
| 496 | | - |
| 497 | | -Privilege Level: PL0 or PL1 |
| 680 | +Command Code: `0x4C4D_5632` ("LMV2") |
| 498 | 681 | |
| 499 | 682 | *Table: `LMS_SIGNATURE_VERIFY` input arguments* |
| 500 | 683 | |
| @@ -509,6 +692,7 @@ |
| 509 | 692 | | signature\_ots | u8[1252] | LM-OTS signature |
| 510 | 693 | | signature\_tree\_type | u8[4] | LMS signature Algorithm type. Must equal 12. |
| 511 | 694 | | signature\_tree\_path | u8[360] | Path through the tree from the leaf associated with the LM-OTS signature to the root |
| 695 | +| hash | u8[48] | SHA384 digest to verify. |
| 512 | 696 | |
| 513 | 697 | *Table: `LMS_SIGNATURE_VERIFY` output arguments* |
| 514 | 698 | |
| @@ -517,40 +701,57 @@ |
| 517 | 701 | | chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. |
| 518 | 702 | | fips\_status | u32 | Indicates if the command is FIPS approved or an error. |
| 519 | 703 | |
| 520 | | -### MLDSA87\_SIGNATURE\_VERIFY |
| 521 | | - |
| 522 | | -Verifies an ML-DSA-87 (FIPS 204) signature. As with the ECDSA and LMS |
| 523 | | -verify commands, the message digest to be verified is taken from |
| 524 | | -Caliptra's SHA384 accelerator peripheral. Callers must stream the |
| 525 | | -message through the SHA accelerator before issuing this command; |
| 526 | | -carrying the raw message in-band would put hashing outside the FIPS |
| 527 | | -module boundary and is therefore disallowed. |
| 528 | | - |
| 529 | | -ML-DSA-87 is stateless and does not have the per-key signature budget that |
| 530 | | -LMS does, which is the primary motivation for adding this command alongside |
| 531 | | -the existing `LMS_SIGNATURE_VERIFY`. |
| 532 | | - |
| 533 | | -In the event of an invalid signature, the mailbox command will report |
| 534 | | -`CMD_FAILURE` and the cause will be logged as a non-fatal error. |
| 535 | | - |
| 536 | | -Command Code: `0x4D44_5356` ("MDSV") |
| 537 | | - |
| 538 | | -Privilege Level: PL0 or PL1 |
| 704 | +### MLDSA87_SIGNATURE_VERIFY |
| 705 | + |
| 706 | +Verifies the signature against the message and MLDSA-87 public key. |
| 707 | + |
| 708 | +The public key and signature formats are described in [FIPS 204](https://csrc.nist.gov/pubs/fips/204/final). |
| 709 | + |
| 710 | +The command will only return a success if the signature is valid. |
| 711 | + |
| 712 | +Command Code: `0x4D4C_5632` ("MLV2") |
| 539 | 713 | |
| 540 | 714 | *Table: `MLDSA87_SIGNATURE_VERIFY` input arguments* |
| 541 | | - |
| 542 | | -| **Name** | **Type** | **Description** |
| 543 | | -| -------- | --------- | --------------- |
| 544 | | -| chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. |
| 545 | | -| pub\_key | u8[2592] | Encoded ML-DSA-87 public key (FIPS 204). |
| 546 | | -| signature | u8[4627] | Encoded ML-DSA-87 signature (FIPS 204). |
| 715 | +| **Name** | **Type** | **Description** | |
| 716 | +| --------- | ------------ | ------------------ | |
| 717 | +| chksum | u32 || |
| 718 | +| pub_key | u8[2592] | Public key | |
| 719 | +| signature | u8[4627] | Signature to check | |
| 720 | +| padding | u8[1] || |
| 721 | +| data len | u32 | Length of message | |
| 722 | +| data | u8[data len] | Message to check | |
| 723 | + |
| 724 | + |
| 547 | 725 | |
| 548 | 726 | *Table: `MLDSA87_SIGNATURE_VERIFY` output arguments* |
| 549 | | - |
| 550 | | -| **Name** | **Type** | **Description** |
| 551 | | -| -------- | -------- | --------------- |
| 552 | | -| chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. |
| 553 | | -| fips\_status | u32 | Indicates if the command is FIPS approved or an error. |
| 727 | +| **Name** | **Type** | **Description** | |
| 728 | +| ----------- | -------- | -------------------------- | |
| 729 | +| chksum | u32 || |
| 730 | +| fips_status | u32 | FIPS approved or an error | |
| 731 | + |
| 732 | + |
| 733 | + |
| 734 | +### INSTALL\_OWNER\_PK\_HASH |
| 735 | + |
| 736 | +Exposes a command to save the owner public key hash in persistent data. |
| 737 | + |
| 738 | +Command Code: `0x4F57_4E50` ("OWNP") |
| 739 | + |
| 740 | +*Table: `INSTALL_OWNER_PK_HASH` input arguments* |
| 741 | + |
| 742 | +| **Name** | **Type** | **Description** |
| 743 | +| -------- | -------- | --------------- |
| 744 | +| chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. |
| 745 | +| digest | u32[12] | Owner public key hash. |
| 746 | + |
| 747 | +*Table: `INSTALL_OWNER_PK_HASH` output arguments* |
| 748 | + |
| 749 | +| **Name** | **Type** | **Description** |
| 750 | +| -------- | -------- | --------------- |
| 751 | +| chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. |
| 752 | +| fips\_status | u32 | Indicates if the command is FIPS approved or an error. |
| 753 | +| dpe\_result | u32 | Result code, 0 on success. |
| 754 | + |
| 554 | 755 | |
| 555 | 756 | ### STASH\_MEASUREMENT |
| 556 | 757 | |
| @@ -560,10 +761,9 @@ |
| 560 | 761 | * Call the DPE DeriveContext command with the DefaultContext in the locality of |
| 561 | 762 | the PL0 PAUSER. |
| 562 | 763 | * Extend the measurement into PCR31 (`PCR_ID_STASH_MEASUREMENT`). |
| 764 | +* **Note**: This command can only be called in the locality of the PL0 PAUSER. |
| 563 | 765 | |
| 564 | 766 | Command Code: `0x4D45_4153` ("MEAS") |
| 565 | | - |
| 566 | | -Privilege Level: PL0 |
| 567 | 767 | |
| 568 | 768 | *Table: `STASH_MEASUREMENT` input arguments* |
| 569 | 769 | |
| @@ -600,8 +800,6 @@ |
| 600 | 800 | |
| 601 | 801 | Command Code: `0x4453_424C` ("DSBL") |
| 602 | 802 | |
| 603 | | -Privilege Level: PL0 |
| 604 | | - |
| 605 | 803 | *Table: `DISABLE_ATTESTATION` input arguments* |
| 606 | 804 | |
| 607 | 805 | | **Name** | **Type** | **Description** |
| @@ -620,8 +818,6 @@ |
| 620 | 818 | Invokes a serialized DPE command. |
| 621 | 819 | |
| 622 | 820 | Command Code: `0x4450_4543` ("DPEC") |
| 623 | | - |
| 624 | | -Privilege Level: PL0 or PL1; a subset of DPE commands requires PL0 (see [Mailbox command privilege levels](#mailbox-command-privilege-levels)) |
| 625 | 821 | |
| 626 | 822 | *Table: `INVOKE_DPE_COMMAND` input arguments* |
| 627 | 823 | |
| @@ -640,16 +836,14 @@ |
| 640 | 836 | | data\_size | u32 | Length in bytes of the valid data in the data field. |
| 641 | 837 | | data | u8[...] | DPE response structure as defined in the DPE iRoT profile. |
| 642 | 838 | |
| 643 | | -### QUOTE\_PCRS |
| 644 | | - |
| 645 | | -Generates a signed quote over all Caliptra hardware PCRs that are using the Caliptra PCR quoting key. |
| 839 | +### QUOTE\_PCRS\_ECC384 |
| 840 | + |
| 841 | +Generates a signed quote over all Caliptra hardware PCRs using the Caliptra PCR ECC384 quoting key. |
| 646 | 842 | All PCR values are hashed together with the nonce to produce the quote. |
| 647 | 843 | |
| 648 | 844 | Command Code: `0x5043_5251` ("PCRQ") |
| 649 | 845 | |
| 650 | | -Privilege Level: PL0 or PL1 |
| 651 | | - |
| 652 | | -*Table: `QUOTE_PCRS` input arguments* |
| 846 | +*Table: `QUOTE_PCRS_ECC384` input arguments* |
| 653 | 847 | |
| 654 | 848 | | **Name** | **Type** | **Description** |
| 655 | 849 | | -------- | -------- | --------------- |
| @@ -658,28 +852,52 @@ |
| 658 | 852 | |
| 659 | 853 | PcrValue is defined as u8[48] |
| 660 | 854 | |
| 661 | | -*Table: `QUOTE_PCRS` output arguments* |
| 662 | | - |
| 663 | | -| **Name** | **Type** | **Description** |
| 664 | | -| -------- | -------- | --------------- |
| 665 | | -| chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. |
| 666 | | -| fips\_status | u32 | Indicates if the command is FIPS approved or an error. |
| 667 | | -| PCRs | PcrValue[32] | Values of all PCRs. |
| 668 | | -| nonce | u8[32] | Return the nonce used as input for convenience. |
| 669 | | -| digest | u8[48] | Return the digest over the PCR values and the nonce. |
| 670 | | -| reset\_ctrs | u32[32] | Reset counters for all PCRs. |
| 671 | | -| signature\_r | u8[48] | R portion of the signature over the PCR quote. |
| 672 | | -| signature\_s | u8[48] | S portion of the signature over the PCR quote. |
| 855 | +*Table: `QUOTE_PCRS_ECC384` output arguments* |
| 856 | + |
| 857 | +| **Name** | **Type** | **Description** |
| 858 | +| -------- | -------- | --------------- |
| 859 | +| chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. |
| 860 | +| fips\_status | u32 | Indicates if the command is FIPS approved or an error. |
| 861 | +| PCRs | PcrValue[32] | Values of all PCRs. |
| 862 | +| nonce | u8[32] | Return the nonce used as input for convenience. |
| 863 | +| reset\_ctrs | u32[32] | Reset counters for all PCRs. |
| 864 | +| digest | u8[48] | Return the lower 48 bytes of SHA2-512 digest over the PCR values and the nonce. |
| 865 | +| signature\_r | u8[48] | ECC P-384 R portion of the signature over the `ecc_digest`. </br> The FMC Alias ECC P-384 private key stored in Key Vault slot 7 is utilized for the signing operation. |
| 866 | +| signature\_s | u8[48] | ECC P-384 S portion of the signature over the `ecc_digest`. |
| 867 | + |
| 868 | +### QUOTE\_PCRS\_MLDSA87 |
| 869 | + |
| 870 | +Generates a signed quote over all Caliptra hardware PCRs that are using the Caliptra PCR Mldsa87 quoting key. |
| 871 | +All PCR values are hashed together with the nonce to produce the quote. |
| 872 | + |
| 873 | +Command Code: `0x5043_524D` ("PCRM") |
| 874 | + |
| 875 | +*Table: `QUOTE_PCRS_MLDSA87` input arguments* |
| 876 | + |
| 877 | +| **Name** | **Type** | **Description** |
| 878 | +| -------- | -------- | --------------- |
| 879 | +| chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. |
| 880 | +| nonce | u8[32] | Caller-supplied nonce to be included in signed data. |
| 881 | + |
| 882 | +PcrValue is defined as u8[48] |
| 883 | + |
| 884 | +*Table: `QUOTE_PCRS_MLDSA87` output arguments* |
| 885 | + |
| 886 | +| **Name** | **Type** | **Description** |
| 887 | +| -------- | -------- | --------------- |
| 888 | +| chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. |
| 889 | +| fips\_status | u32 | Indicates if the command is FIPS approved or an error. |
| 890 | +| PCRs | PcrValue[32] | Values of all PCRs. |
| 891 | +| nonce | u8[32] | Return the nonce used as input for convenience. |
| 892 | +| reset\_ctrs | u32[32] | Reset counters for all PCRs. |
| 893 | +| digest | u8[64] | Return the SHA2-512 digest over the PCR values and the nonce, in byte reversed order. |
| 894 | +| signature | u8[4628] | MLDSA-87 signature over the `digest` (4627 bytes + 1 Reserved byte). </br> The FMC Alias MLDSA seed stored in Key Vault slot 8 is utilized to generate the private key, which is subsequently used for the signing operation. |
| 673 | 895 | |
| 674 | 896 | ### EXTEND\_PCR |
| 675 | 897 | |
| 676 | | -Extends a Caliptra hardware PCR. This command is restricted to the PL0 PAUSER. |
| 677 | | -PCR0 through PCR3 are reserved and cannot be extended with this command. PCR31 |
| 678 | | -is available to PL0 for MCU-managed SoC firmware measurements. |
| 898 | +Extends a Caliptra hardware PCR. |
| 679 | 899 | |
| 680 | 900 | Command Code: `0x5043_5245` ("PCRE") |
| 681 | | - |
| 682 | | -Privilege Level: PL0 or PL1 |
| 683 | 901 | |
| 684 | 902 | *Table: `EXTEND_PCR` input arguments* |
| 685 | 903 | |
| @@ -696,10 +914,6 @@ |
| 696 | 914 | | chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. |
| 697 | 915 | | fips\_status | u32 | Indicates if the command is FIPS approved or an error. |
| 698 | 916 | |
| 699 | | -PCRs 0-3 (the FMC/RT current and journey PCRs) and PCR31 (the stash-measurement |
| 700 | | -PCR) are reserved for Caliptra's own use and cannot be extended through this |
| 701 | | -command by any caller; requests targeting them fail with `RUNTIME_PCR_RESERVED`. |
| 702 | | - |
| 703 | 917 | Note that extensions made into Caliptra's PCRs are _not_ appended to Caliptra's internal PCR log. |
| 704 | 918 | |
| 705 | 919 | ### GET\_PCR\_LOG |
| @@ -707,8 +921,6 @@ |
| 707 | 921 | Gets Caliptra's internal PCR log. |
| 708 | 922 | |
| 709 | 923 | Command Code: `0x504C_4F47` ("PLOG") |
| 710 | | - |
| 711 | | -Privilege Level: PL0 or PL1 |
| 712 | 924 | |
| 713 | 925 | *Table: `GET_PCR_LOG` input arguments* |
| 714 | 926 | |
| @@ -737,8 +949,6 @@ |
| 737 | 949 | |
| 738 | 950 | Command Code: `0x5043_5252` ("PCRR") |
| 739 | 951 | |
| 740 | | -Privilege Level: PL0 or PL1 |
| 741 | | - |
| 742 | 952 | *Table: `INCREMENT_PCR_RESET_COUNTER` input arguments* |
| 743 | 953 | |
| 744 | 954 | | **Name** | **Type** | **Description** |
| @@ -758,8 +968,6 @@ |
| 758 | 968 | Associates a unique tag with a DPE context. |
| 759 | 969 | |
| 760 | 970 | Command Code: `0x5451_4754` ("TAGT") |
| 761 | | - |
| 762 | | -Privilege Level: PL0 or PL1; tags only contexts in the caller's own locality |
| 763 | 971 | |
| 764 | 972 | *Table: `DPE_TAG_TCI` input arguments* |
| 765 | 973 | |
| @@ -780,9 +988,11 @@ |
| 780 | 988 | |
| 781 | 989 | Retrieves the TCI measurements corresponding to the tagged DPE context. |
| 782 | 990 | |
| 991 | +NOTE: Additional fields and info may be appended to the response in subsequent FW |
| 992 | +versions. Appending changes the response length and therefore its checksum, so |
| 993 | +the caller and firmware are expected to be updated in lockstep. |
| 994 | + |
| 783 | 995 | Command Code: `0x4754_4744` ("GTGD") |
| 784 | | - |
| 785 | | -Privilege Level: PL0 or PL1; not locality-scoped, either level can read any tagged TCI |
| 786 | 996 | |
| 787 | 997 | *Table: `DPE_GET_TAGGED_TCI` input arguments* |
| 788 | 998 | |
| @@ -799,6 +1009,7 @@ |
| 799 | 1009 | | fips\_status | u32 | Indicates if the command is FIPS approved or an error. |
| 800 | 1010 | | tci\_cumulative | u8[48] | Hash of all of the input data provided to the context. |
| 801 | 1011 | | tci\_current | u8[48] | Most recent measurement made into the context. |
| 1012 | +| svn | u32 | Security Version Number of the tagged DPE context. |
| 802 | 1013 | |
| 803 | 1014 | ### FW\_INFO |
| 804 | 1015 | |
| @@ -808,40 +1019,49 @@ |
| 808 | 1019 | |
| 809 | 1020 | Command Code: `0x494E_464F` ("INFO") |
| 810 | 1021 | |
| 811 | | -Privilege Level: PL0 or PL1 |
| 812 | | - |
| 813 | 1022 | *Table: `FW_INFO` input arguments* |
| 814 | 1023 | |
| 815 | | -| **Name** | **Type** | **Description** |
| 816 | | -| -------- | -------- | --------------- |
| 817 | | -| chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. |
| 1024 | +| **Name** | **Type** | **Description** | |
| 1025 | +| -------- | -------- | --------------------------------------------------------------------------- | |
| 1026 | +| chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. | |
| 1027 | + |
| 818 | 1028 | |
| 819 | 1029 | *Table: `FW_INFO` output arguments* |
| 820 | 1030 | |
| 821 | | -| **Name** | **Type** | **Description** |
| 822 | | -| -------- | -------- | --------------- |
| 823 | | -| chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. |
| 824 | | -| fips\_status | u32 | Indicates if the command is FIPS approved or an error. |
| 825 | | -| pl0_pauser | u32 | PAUSER with PL0 privileges (from image header). |
| 826 | | -| runtime_svn | u32 | Runtime SVN. |
| 827 | | -| min_runtime_svn | u32 | Min Runtime SVN. |
| 828 | | -| fmc_manifest_svn | u32 | FMC SVN. |
| 829 | | -| attestation_disabled | u32 | State of attestation disable. |
| 830 | | -| rom_revision | u8[20] | Revision (Git commit ID) of ROM build. |
| 831 | | -| fmc_revision | u8[20] | Revision (Git commit ID) of FMC build. |
| 832 | | -| runtime_revision | u8[20] | Revision (Git commit ID) of runtime build. |
| 833 | | -| rom_sha256_digest | u32[8] | Digest of ROM binary. |
| 834 | | -| fmc_sha384_digest | u32[12] | Digest of FMC binary. |
| 835 | | -| runtime_sha384_digest | u32[12] | Digest of runtime binary. |
| 836 | | -| owner_pub_key_hash | u32[12] | Hash of the owner public keys provided in the image bundle manifest. |
| 1031 | +| **Name** | **Type** | **Description** | |
| 1032 | +| --------------------------- | -------- | --------------------------------------------------------------------------------------------------------------------------------------------------- | |
| 1033 | +| chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. | |
| 1034 | +| fips\_status | u32 | Indicates if the command is FIPS approved or an error. | |
| 1035 | +| pl0_pauser | u32 | PAUSER with PL0 privileges (from image header). | |
| 1036 | +| firmware_svn | u32 | Firmware SVN. | |
| 1037 | +| min_firmware_svn | u32 | Min Firmware SVN. | |
| 1038 | +| cold_boot_fw_svn | u32 | Cold-boot Firmware SVN. | |
| 1039 | +| attestation_disabled | u32 | State of attestation disable. | |
| 1040 | +| rom_revision | u8[20] | Revision (Git commit ID) of ROM build. | |
| 1041 | +| fmc_revision | u8[20] | Revision (Git commit ID) of FMC build. | |
| 1042 | +| runtime_revision | u8[20] | Revision (Git commit ID) of runtime build. | |
| 1043 | +| rom_sha256_digest | u32[8] | Digest of ROM binary. See [Byte order of cryptographic fields](#byte-order-of-cryptographic-fields). | |
| 1044 | +| fmc_sha384_digest | u32[12] | Digest of FMC binary. See [Byte order of cryptographic fields](#byte-order-of-cryptographic-fields). | |
| 1045 | +| runtime_sha384_digest | u32[12] | Digest of runtime binary. See [Byte order of cryptographic fields](#byte-order-of-cryptographic-fields). | |
| 1046 | +| owner_pub_key_hash | u32[12] | Hash of the owner public keys provided in the image bundle manifest. See [Byte order of cryptographic fields](#byte-order-of-cryptographic-fields). | |
| 1047 | +| authman_sha384_digest | u32[12] | Hash of the authorization manifest provided by SET_AUTH_MANIFEST. See [Byte order of cryptographic fields](#byte-order-of-cryptographic-fields). | |
| 1048 | +| most_recent_fw_error | u32 | Most recent FW non-fatal error (shows current non-fatal error if non-zero) | |
| 1049 | +| vendor_pub_key_hash | u32[12] | Hash of the vendor public key used to verify firmware. **Only present in FW 2.0.2+ and 2.1.1+.** | |
| 1050 | +| image_manifest_pqc_type | u32 | PQC key type from image manifest. **Only present in FW 2.0.2+ and 2.1.1+.** | |
| 1051 | +| vendor_ecc384_pub_key_index | u32 | Index of the vendor ECC public key used for verification. **Only present in FW 2.0.2+ and 2.1.1+.** | |
| 1052 | +| vendor_pqc_pub_key_index | u32 | Index of the vendor PQC public key used for verification. **Only present in FW 2.0.2+ and 2.1.1+.** | |
| 1053 | +| soc_manifest_current_svn | u32 | SVN of the authorization manifest accepted by `SET_AUTH_MANIFEST`, or zero if none has been accepted. | |
| 1054 | +| soc_manifest_min_svn | u32 | Minimum SoC manifest SVN encoded in `FUSE_SOC_MANIFEST_SVN` and enforced by `SET_AUTH_MANIFEST` when anti-rollback checks are enabled. | |
| 1055 | +| owner_auth_manifest_current_svn | u32 | SVN of the owner authorization manifest accepted by `SET_OWNER_AUTH_MANIFEST`, or zero if none has been accepted. | |
| 1056 | +| owner_auth_manifest_min_svn | u32 | Minimum owner authorization manifest SVN encoded in `SS_STRAP_GENERIC[3][15:8]` and enforced by `SET_OWNER_AUTH_MANIFEST` when anti-rollback checks are enabled. | |
| 1057 | +| debug_policy | u32 | Active vendor-authorized debug policy. Bit 0 (`DEBUG_FIRMWARE_ACTIVE`) indicates that the active firmware bundle is marked as debug. Bit 1 (`DEBUG_AUTH_MANIFEST_ACTIVE`) indicates that the installed SoC authorization manifest is marked as debug. Bits 31:2 are zero. | |
| 1058 | + |
| 837 | 1059 | |
| 838 | 1060 | ### VERSION |
| 839 | 1061 | |
| 840 | 1062 | FIPS command to get version info for the module |
| 841 | 1063 | |
| 842 | 1064 | Command Code: `0x4650_5652` ("FPVR") |
| 843 | | - |
| 844 | | -Privilege Level: PL0 or PL1 |
| 845 | 1065 | |
| 846 | 1066 | Table: `VERSION` input arguments |
| 847 | 1067 | |
| @@ -865,8 +1085,6 @@ |
| 865 | 1085 | |
| 866 | 1086 | Command Code: `0x4650_4C54` |
| 867 | 1087 | |
| 868 | | -Privilege Level: PL0 or PL1 |
| 869 | | - |
| 870 | 1088 | Table: `SELF_TEST_START` input arguments |
| 871 | 1089 | |
| 872 | 1090 | | **Name** | **Type** | **Description** |
| @@ -886,8 +1104,6 @@ |
| 886 | 1104 | |
| 887 | 1105 | Command Code: `0x4650_4C67` |
| 888 | 1106 | |
| 889 | | -Privilege Level: PL0 or PL1 |
| 890 | | - |
| 891 | 1107 | Table: `SELF_TEST_GET_RESULTS` input arguments |
| 892 | 1108 | |
| 893 | 1109 | | **Name** | **Type** | **Description** |
| @@ -907,8 +1123,6 @@ |
| 907 | 1123 | |
| 908 | 1124 | Command Code: `0x4650_5344` ("FPSD") |
| 909 | 1125 | |
| 910 | | -Privilege Level: PL0 or PL1 |
| 911 | | - |
| 912 | 1126 | Table: `SHUTDOWN` input arguments |
| 913 | 1127 | |
| 914 | 1128 | | **Name** | **Type** | **Description** |
| @@ -924,15 +1138,13 @@ |
| 924 | 1138 | |
| 925 | 1139 | ### ADD\_SUBJECT\_ALT\_NAME |
| 926 | 1140 | |
| 927 | | -Provides a subject alternative name otherName. Whenever CERTIFY_KEY_EXTENDED is called with the |
| 928 | | -DMTF_OTHER_NAME flag after ADD_SUBJECT_ALT_NAME is called, the resulting DPE CSR or leaf certificate |
| 929 | | -will contain a subject alternative name extension containing the provided otherName, which must be a |
| 930 | | -DMTF device info. All such certificates produced by CERTIFY_KEY_EXTENDED will continue to have the |
| 1141 | +Provides a subject alternative name otherName. Whenever CERTIFY_KEY_EXTENDED is called with the |
| 1142 | +DMTF_OTHER_NAME flag after ADD_SUBJECT_ALT_NAME is called, the resulting DPE CSR or leaf certificate |
| 1143 | +will contain a subject alternative name extension containing the provided otherName, which must be a |
| 1144 | +DMTF device info. All such certificates produced by CERTIFY_KEY_EXTENDED will continue to have the |
| 931 | 1145 | DMTF otherName subject alternative name extension until reset. |
| 932 | 1146 | |
| 933 | 1147 | Command Code: `0x414C_544E` ("ALTN") |
| 934 | | - |
| 935 | | -Privilege Level: PL0 or PL1 |
| 936 | 1148 | |
| 937 | 1149 | *Table: `ADD_SUBJECT_ALT_NAME` input arguments* |
| 938 | 1150 | |
| @@ -955,190 +1167,1518 @@ |
| 955 | 1167 | |
| 956 | 1168 | Command Code: `0x434B_4558` ("CKEX") |
| 957 | 1169 | |
| 958 | | -Privilege Level: PL0 |
| 959 | | - |
| 960 | 1170 | *Table: `CERTIFY_KEY_EXTENDED` input arguments* |
| 961 | 1171 | |
| 962 | | -| **Name** | **Type** | **Description** |
| 963 | | -| -------- | -------- | --------------- |
| 964 | | -| chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. |
| 965 | | -| certify\_key\_req | u8[72] | Certify Key Request. |
| 966 | | -| flags | u32 | Flags determining which custom extensions to include in the certificate. |
| 1172 | +| **Name** | **Type** | **Description** | |
| 1173 | +| ----------------- | -------- | --------------------------------------------------------------------------- | |
| 1174 | +| chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. | |
| 1175 | +| certify\_key\_req | u8[72] | Certify Key Request. | |
| 1176 | +| flags | u32 | Flags determining which custom extensions to include in the certificate. | |
| 1177 | + |
| 967 | 1178 | |
| 968 | 1179 | *Table: `CERTIFY_KEY_EXTENDED` input flags* |
| 969 | 1180 | |
| 970 | | -| **Name** | **Offset** |
| 971 | | -| -------- | ---------- |
| 972 | | -| DMTF_OTHER_NAME | 1 << 31 |
| 1181 | +| **Name** | **Offset** | |
| 1182 | +| --------------- | ---------- | |
| 1183 | +| DMTF_OTHER_NAME | 1 << 31 | |
| 1184 | + |
| 973 | 1185 | |
| 974 | 1186 | *Table: `CERTIFY_KEY_EXTENDED` output arguments* |
| 1187 | + |
| 1188 | +| **Name** | **Type** | **Description** | |
| 1189 | +| ------------------ | -------- | -------------------------------------------------------------------------- | |
| 1190 | +| chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. | |
| 1191 | +| fips\_status | u32 | Indicates if the command is FIPS approved or an error. | |
| 1192 | +| certify\_key\_resp | u8[2176] | Certify Key Response. | |
| 1193 | + |
| 1194 | + |
| 1195 | +### CERTIFY\_KEY\_CHUNKS |
| 1196 | + |
| 1197 | +Invokes a DPE `CertifyKey` command (ECC-P384 or ML-DSA-87) and returns the response in chunks. This is useful when the DPE response (which contains a certificate or CSR) is larger than the mailbox size or larger than the caller can easily consume. |
| 1198 | + |
| 1199 | +The handler re-executes the full DPE `CertifyKey` operation on every call and then returns the requested `[offset, offset+max_size)` window of the freshly generated response. Each call rotates the context handle, if needed. The new handle is returned in the per-chunk response header and must be used for the next call. |
| 1200 | + |
| 1201 | +Command Code: `0x434B_4348` ("CKCH") |
| 1202 | + |
| 1203 | +*Table: `CERTIFY_KEY_CHUNKS` input arguments* |
| 1204 | + |
| 1205 | +| **Name** | **Type** | **Description** | |
| 1206 | +| ----------------- | -------- | ------------------------------------------------------------------------------------- | |
| 1207 | +| chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. | |
| 1208 | +| flags | u32 | Flags. | |
| 1209 | +| reserved | u32 | Reserved. | |
| 1210 | +| max\_size | u32 | The maximum length of the chunk the caller wants to receive. If 0, defaults to 15360. | |
| 1211 | +| offset | u32 | Offset into the full CertifyKey response to read from. | |
| 1212 | +| certify\_key\_req | u8[72] | The serialized DPE `CertifyKey` command. | |
| 1213 | + |
| 1214 | + |
| 1215 | +*Table: `CERTIFY_KEY_CHUNKS` input flags* |
| 1216 | + |
| 1217 | +| **Name** | **Offset** | |
| 1218 | +| --------- | ---------- | |
| 1219 | +| USE_MLDSA | 1 << 31 | |
| 1220 | + |
| 1221 | + |
| 1222 | +When `USE_MLDSA` is set, the command operates on the ML-DSA-87 DPE profile; otherwise, it operates on the ECC-P384 profile. |
| 1223 | + |
| 1224 | +*Table: `CERTIFY_KEY_CHUNKS` output arguments* |
| 1225 | + |
| 1226 | +| **Name** | **Type** | **Description** | |
| 1227 | +| ------------------ | --------- | -------------------------------------------------------------------------- | |
| 1228 | +| chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. | |
| 1229 | +| fips\_status | u32 | Indicates if the command is FIPS approved or an error. | |
| 1230 | +| context\_handle | u8[16] | The new DPE context handle returned by the `CertifyKey` command. | |
| 1231 | +| chunk\_len | u32 | The length of the chunk returned in `certify_key_resp`. | |
| 1232 | +| remaining | u32 | The number of bytes remaining in the full response after this chunk. | |
| 1233 | +| certify\_key\_resp | u8[15360] | The chunk of the DPE `CertifyKey` response. | |
| 1234 | + |
| 1235 | + |
| 1236 | +### SET_AUTH_MANIFEST |
| 1237 | + |
| 1238 | +The SoC uses this command and `SET_IMAGE_METADTA` to program an image manifest for Manifest-Based Image Authorization to Caliptra. In response to these commands, the Caliptra Runtime will verify the manifest by authenticating the public keys and in turn using them to authenticate the IMC. On successful verification, the Runtime will store the IMEs into DCCM for future use. Every active `fw_id` must be unique within this manifest and must not appear in the installed owner-only manifest. A collision rejects the command without replacing either active collection. |
| 1239 | + |
| 1240 | +Command Code: `0x4154_4D4E` ("ATMN") |
| 1241 | + |
| 1242 | +*Table: `SET_AUTH_MANIFEST` input arguments* |
| 975 | 1243 | |
| 976 | 1244 | | **Name** | **Type** | **Description** |
| 977 | 1245 | | -------- | -------- | --------------- |
| 978 | | -| chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. |
| 979 | | -| fips\_status | u32 | Indicates if the command is FIPS approved or an error. |
| 980 | | -| certify\_key\_resp | u8[2176] | Certify Key Response. |
| 981 | | - |
| 982 | | -### SET\_AUTH\_MANIFEST |
| 983 | | - |
| 984 | | -Command Code: `0x4154_4D4E` ("ATMN") |
| 985 | | - |
| 986 | | -Privilege Level: PL0 |
| 987 | | - |
| 988 | | -*Table: `SET_AUTH_MANIFEST` input arguments* |
| 989 | | - |
| 990 | | -| **Name** | **Type** | **Description** | |
| 991 | | -| ------------------------------ | ------------------ | --------------- | |
| 992 | 1246 | | chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. | |
| 993 | 1247 | | manifest size | u32 | The size of the full Authentication Manifest | |
| 994 | | -| manifest\_marker | u32 | Marker needs to be 0x4154_4D4E for the preamble to be valid | |
| 1248 | +| preamble\_marker | u32 | Marker needs to be 0x4154_4D4E for the preamble to be valid | |
| 995 | 1249 | | preamble\_size | u32 | Size of the preamble | |
| 996 | | -| manifest\_version | u32 | Version of the preamble | |
| 997 | | -| manifest\_flags | u32 | Manifest flags. See `AUTH_MANIFEST_FLAGS` below. | |
| 998 | | -| manifest\_vendor\_ecc384\_key | u32[24] | Manifest Vendor ECC P-384 public key used to verify the IMC Signature. <br> **X-Coordinate:** Public Key X-Coordinate (48 bytes) <br> **Y-Coordinate:** Public Key Y-Coordinate (48 bytes) | |
| 999 | | -| manifest\_vendor\_lms\_key | u32[12] | Manifest Vendor LMS public key used to verify the IMC Signature. <br> **tree_type:** LMS Algorithm Type (4 bytes) <br> **otstype:** LMS Ots Algorithm Type (4 bytes) <br> **id:** (16 bytes) <br> **digest:** (24 bytes) <br> Note: If LMS validation is not required, this should field should be zeroed out. | |
| 1000 | | -| manifest\_vendor\_ecc384\_sig | u32[24] | Manifest Vendor ECDSA P-384 signature of the Version, Flags, Vendor ECC and LMS public keys, hashed using SHA2-384. <br> **R-Coordinate:** Random Point (48 bytes) <br> **S-Coordinate:** Proof (48 bytes) | |
| 1001 | | -| manifest\_vendor\_LMS\_sig | u32[405] | Vendor LMS signature of the Version, Flags, Vendor ECC and LMS public keys, hashed using SHA2-384. <br> **q:** Leaf of the Merkle tree where the OTS public key appears (4 bytes) <br> **ots:** Lmots Signature (1252 bytes) <br> **tree_type:** Lms Algorithm Type (4 bytes) <br> **tree_path:** Path through the tree from the leaf associated with the LM-OTS signature to the root. (360 bytes) <br> Note: If LMS validation is not required, this should field should be zeroed out. | |
| 1002 | | -| manifest\_owner\_ecc384\_key | u32[24] | Manifest Owner ECC P-384 public key used to verify the IMC Signature. <br> **X-Coordinate:** Public Key X-Coordinate (48 bytes) <br> **Y-Coordinate:** Public Key Y-Coordinate (48 bytes) | |
| 1003 | | -| manifest\_owner\_lms\_key | u32[12] | Manifest Owner LMS public key used to verify the IMC Signature. <br> **tree_type:** LMS Algorithm Type (4 bytes) <br> **otstype:** LMS Ots Algorithm Type (4 bytes) <br> **id:** (16 bytes) <br> **digest:** (24 bytes) <br> Note: If LMS validation is not required, this should field should be zeroed out. | |
| 1004 | | -| manifest\_owner\_ecc384\_sig | u32[24] | Owner ECDSA P-384 signature of the Owner ECC and LMS public keys, hashed using SHA2-384. <br> **R-Coordinate:** Random Point (48 bytes) <br> **S-Coordinate:** Proof (48 bytes) | |
| 1005 | | -| manifest\_owner\_LMS\_sig | u32[405] | Owner LMS signature of the Version, Flags, Owner ECC and LMS public keys, hashed using SHA2-384. <br> **q:** Leaf of the Merkle tree where the OTS public key appears (4 bytes) <br> **ots:** Lmots Signature (1252 bytes) <br> **tree_type:** Lms Algorithm Type (4 bytes) <br> **tree_path:** Path through the tree from the leaf associated with the LM-OTS signature to the root. (360 bytes) <br> Note: If LMS validation is not required, this should field should be zeroed out. | |
| 1006 | | -| metadata\_vendor\_ecc384\_sig | u32[24] | Metadata Vendor ECC384 signature over the image metadata collection using the manifest vendor ecc384 key. | |
| 1007 | | -| metadata\_vendor\_LMS\_sig | u32[405] | Metadata Vendor LMOTS-SHA192-W4 signature over the image metadata collection using the manifest vendor LMS key. | |
| 1008 | | -| metadata\_owner\_ecc384\_sig | u32[24] | Metadata Owner ECC384 signature over the image metadata collection using the manifest owner ecc384 key. | |
| 1009 | | -| metadata\_owner\_LMS\_sig | u32[405] | Metadata Owner LMOTS-SHA192-W4 signature over the image metadata collection manifest owner LMS key. | |
| 1250 | +| preamble\_version | u32 | Version of the preamble | |
| 1251 | +| preamble\_flags | u32 | Manifest flags. See AUTH_MANIFEST_FLAGS below | |
| 1252 | +| preamble\_vendor\_ecc384\_key | u32[24] | Vendor ECC384 key with X and Y coordinates in that order | |
| 1253 | +| preamble\_vendor\_pqc\_key | u32[648] | Vendor MLDSA-87 or LMS-SHA192-H15 key | |
| 1254 | +| preamble\_vendor\_ecc384\_sig | u32[24] | Vendor ECC384 signature | |
| 1255 | +| preamble\_vendor\_PQC\_sig | u32[1157] | Vendor MLDSA-87 or LMOTS-SHA192-W4 signature | |
| 1256 | +| preamble\_owner\_ecc384\_key | u32[24] | Owner ECC384 key with X and Y coordinates in that order | |
| 1257 | +| preamble\_owner\_pqc\_key | u32[648] | Owner MLDSA-87 or LMS-SHA192-H15 key | |
| 1258 | +| preamble\_owner\_ecc384\_sig | u32[24] | Owner ECC384 signature | |
| 1259 | +| preamble\_owner\_PQC\_sig | u32[1157] | Owner MLDSA-87 or LMOTS-SHA192-W4 signature | |
| 1260 | +| metadata\_vendor\_ecc384\_sig | u32[24] | Metadata Vendor ECC384 signature | |
| 1261 | +| metadata\_vendor\_PQC\_sig | u32[1157] | Metadata Vendor MLDSA-87 or LMOTS-SHA192-W4 signature | |
| 1262 | +| metadata\_owner\_ecc384\_sig | u32[24] | Metadata Owner ECC384 signature | |
| 1263 | +| metadata\_owner\_PQC\_sig | u32[1157] | Metadata Owner MLDSA-87 or LMOTS-SHA192-W4 signature | |
| 1010 | 1264 | | metadata\_entry\_entry\_count | u32 | number of metadata entries | |
| 1011 | | -| metadata\_entries | MetaData[127] | The max number of metadata entries is 127 but less can be used | |
| 1265 | +| metadata\_entries | Metadata[80] | The max number of metadata entries is 80 but less can be used | |
| 1012 | 1266 | |
| 1013 | 1267 | |
| 1014 | 1268 | |
| 1015 | 1269 | *Table: `AUTH_MANIFEST_FLAGS` input flags* |
| 1016 | | - |
| 1017 | 1270 | | **Name** | **Value** | |
| 1018 | | -| --------------------------- | ----------- | |
| 1271 | +| ------------------------- | --------- | |
| 1019 | 1272 | | VENDOR_SIGNATURE_REQUIRED | 1 << 0 | |
| 1020 | | - |
| 1273 | +| DEBUG_IMAGE | 1 << 1 | |
| 1274 | + |
| 1275 | + |
| 1276 | +`DEBUG_IMAGE` is valid only when `VENDOR_SIGNATURE_REQUIRED` is also set. Runtime rejects an invalid combination with `RUNTIME_AUTH_MANIFEST_INVALID_FLAGS`. Runtime rejects a debug manifest unless it is running in subsystem mode with `SS_DEBUG_INTENT` asserted and `SS_STRAP_GENERIC[3][31]` clear, returning `RUNTIME_AUTH_MANIFEST_DEBUG_IMAGE_NOT_ALLOWED`. Existing vendor and owner authentication remain required. |
| 1277 | + |
| 1278 | +After a successful `SET_AUTH_MANIFEST`, Runtime sets `FW_INFO.debug_policy[1]` for a debug manifest and clears it for a normal manifest. Failed installations and `VERIFY_AUTH_MANIFEST` do not change the active bit. The bit survives warm and update resets, is cleared on cold reset, and is not modified by `SET_OWNER_AUTH_MANIFEST`. |
| 1021 | 1279 | |
| 1022 | 1280 | *Table: `AUTH_MANIFEST_METADATA_ENTRY` digest entries* |
| 1023 | 1281 | |
| 1024 | | -| **Name** | **Type** | **Description** | |
| 1025 | | -| --------------- | ---------- | ---------------------------------- | |
| 1026 | | -| fw\_id | u32 | Id of the image | |
| 1027 | | -| flags | u32 | See `METADATA_ENTRY_FLAGS` below | |
| 1028 | | -| digest | u32[48] | Digest of the image | |
| 1029 | | - |
| 1030 | | - |
| 1031 | | - |
| 1032 | | -*Table: `METADATA_ENTRY_FLAGS` input flags* |
| 1033 | | - |
| 1034 | | -| **Name** | **Size (Bits)** | **Description** | |
| 1035 | | -| --------------------- | ----------------- | ----------------- | |
| 1036 | | -| image\_source | 2 | 1: InRequest | |
| 1037 | | -| ignore\_auth\_check | 1 | If set, the image digest is not compared for the firmware id | |
| 1038 | | - |
| 1039 | | - |
| 1040 | | -*Table: `SET_AUTH_MANIFEST` output arguments* |
| 1041 | | - |
| 1042 | | -| **Name** | **Type** | **Description** | |
| 1043 | | -| -------- | -------- | --------------- | |
| 1044 | | -| chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. | |
| 1045 | | -| fips\_status | u32 | Indicates if the command is FIPS approved or an error. | |
| 1046 | | - |
| 1282 | + |
| 1283 | +| **Name** | **Type** | **Description** | |
| 1284 | +| ------------------------ | --------- | ---------------- | |
| 1285 | +| Image Hash | u8[48] | SHA2-384 hash of a SOC image. | |
| 1286 | + |
| 1287 | +| Image_id | u32 | This corresponds to the `Image Identifier` field in the [SoC Manifest](https://github.com/chipsalliance/caliptra-sw/blob/main-2.x/auth-manifest/README.md) |
| 1288 | +| Component_id | u32 | This corresponds to the `Component Id` field in the [SoC Manifest](https://github.com/chipsalliance/caliptra-sw/blob/main-2.x/auth-manifest/README.md) |
| 1289 | +| flags | u32 | This corresponds to the `flags` field in the [SoC Manifest](https://github.com/chipsalliance/caliptra-sw/blob/main-2.x/auth-manifest/README.md) |
| 1290 | +| Image Load Address High | u32 | This corresponds to the `Image Load Address High` field in the [SoC Manifest](https://github.com/chipsalliance/caliptra-sw/blob/main-2.x/auth-manifest/README.md) |
| 1291 | +| Image Load Address Low | u32 | This corresponds to the `Image Load Address Low` field in the [SoC Manifest](https://github.com/chipsalliance/caliptra-sw/blob/main-2.x/auth-manifest/README.md) |
| 1292 | +| Staging Address High | u32 | This corresponds to the `Staging Address High` field in the [SoC Manifest](https://github.com/chipsalliance/caliptra-sw/blob/main-2.x/auth-manifest/README.md) |
| 1293 | +| Staging Address Low | u32 | This corresponds to the `Staging Address Low` field in the [SoC Manifest](https://github.com/chipsalliance/caliptra-sw/blob/main-2.x/auth-manifest/README.md) |
| 1294 | +| Classification | u32 | This corresponds to the `Classification` field in the [SoC Manifest](https://github.com/chipsalliance/caliptra-sw/blob/main-2.x/auth-manifest/README.md) |
| 1295 | +| Version Number | u32 | This corresponds to the `Version Number` field in the [SoC Manifest](https://github.com/chipsalliance/caliptra-sw/blob/main-2.x/auth-manifest/README.md) |
| 1296 | +| Version String | u8[32] | This corresponds to the `Version String` field in the [SoC Manifest](https://github.com/chipsalliance/caliptra-sw/blob/main-2.x/auth-manifest/README.md) |
| 1297 | + |
| 1298 | +### VERIFY_AUTH_MANIFEST |
| 1299 | + |
| 1300 | +This command verifies the integrity and authenticity of the provided image manifest, including the `DEBUG_IMAGE` policy described above. Unlike `SET_AUTH_MANIFEST`, it performs validation only and does not persist the manifest in DCCM or modify `FW_INFO.debug_policy`. It also rejects a `fw_id` collision with the currently installed owner-only manifest. |
| 1301 | + |
| 1302 | +Command Code: `0x4154_564D` ("ATVM") |
| 1303 | + |
| 1304 | +The input arguments are the same as the `SET_AUTH_MANIFEST` command. |
| 1305 | + |
| 1306 | + |
| 1307 | +### SET_OWNER_AUTH_MANIFEST |
| 1308 | + |
| 1309 | +The SoC uses this command to program an Owner Authorization Manifest, an owner-only authorization document stored independently from the manifest loaded by `SET_AUTH_MANIFEST`. The runtime parses the manifest, verifies its policy fields and Image Metadata Collection (IMC) signatures, and stores the IMC into a dedicated DCCM region. The vendor + owner collection populated by `SET_AUTH_MANIFEST` is never modified by this command. |
| 1310 | + |
| 1311 | +Command Code: `0x4F41_4D4E` ("OAMN") |
| 1312 | + |
| 1313 | +Verification chain: |
| 1314 | + |
| 1315 | +1. The manifest's `owner_pub_keys` are signed by the firmware-image owner key (latched from FMC at boot via `manifest1.preamble.owner_pub_keys`). This signature also covers the policy fields `version`, `svn`, `flags`, and `owner_pub_keys`. |
| 1316 | +2. The manifest's IMC is signed by the manifest's own `owner_pub_keys`, which were just verified to chain to the firmware-image owner key. |
| 1317 | +3. The manifest's `svn` is checked against the floor encoded in `SS_STRAP_GENERIC[3][15:8]` (subsystem mode only). The check is skipped when the lifecycle is `Unprovisioned` or anti-rollback is disabled. |
| 1318 | + |
| 1319 | +#### Owner Authorization Manifest Minimum SVN |
| 1320 | + |
| 1321 | +`SS_STRAP_GENERIC[3][15:8]` carries a binary value in the range `0..255`; it does not carry a fuse bitmap. Before Caliptra starts, MCU firmware is responsible for deriving the owner-manifest minimum SVN from the platform's monotonic storage and programming the resulting integer into this strap. The strap is then locked by `CPTRA_FUSE_WR_DONE`. |
| 1322 | + |
| 1323 | +This software interface does not define a new Caliptra fuse field. If a platform uses the same thermometer encoding as the existing SVN fuses, a 256-bit-aligned platform field can use bits 0 through 254 to encode SVN values 1 through 255, with all zeros encoding SVN 0 and bit 255 reserved. The authoritative physical fuse allocation belongs to the SoC/platform fuse-controller specification. |
| 1324 | + |
| 1325 | +The maximum IMC capacity is 32 entries. Every active `fw_id` must be unique within this manifest and must not appear in the installed vendor + owner manifest. A collision rejects the command without replacing either active collection. Each successful call replaces the existing owner-only collection. |
| 1326 | + |
| 1327 | +*Table: `SET_OWNER_AUTH_MANIFEST` input arguments* |
| 1328 | + |
| 1329 | +| **Name** | **Type** | **Description** | |
| 1330 | +| ------------------------------------- | ------------ | --------------- | |
| 1331 | +| chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. | |
| 1332 | +| manifest size | u32 | The size of the full Owner Authorization Manifest. | |
| 1333 | +| preamble\_marker | u32 | Marker needs to be `0x4D4F_574F` ("OWOM" little-endian) for the preamble to be valid. | |
| 1334 | +| preamble\_size | u32 | Size of the Owner Authorization Manifest Preamble. | |
| 1335 | +| preamble\_version | u32 | Version of the preamble. | |
| 1336 | +| preamble\_svn | u32 | Security version, range `[0, 255]`. Checked against `SS_STRAP_GENERIC[3][15:8]`. | |
| 1337 | +| preamble\_flags | u32 | Reserved. Must be zero. | |
| 1338 | +| preamble\_owner\_ecc384\_key | u32[24] | Owner ECC384 public key carried in the manifest. | |
| 1339 | +| preamble\_owner\_pqc\_key | u32[648] | Owner MLDSA-87 or LMS-SHA192-H15 public key carried in the manifest. | |
| 1340 | +| preamble\_owner\_pub\_keys\_ecc\_sig | u32[24] | ECC384 signature by the firmware-image owner key over `version..=owner_pub_keys`. | |
| 1341 | +| preamble\_owner\_pub\_keys\_pqc\_sig | u32[1157] | PQC signature by the firmware-image owner key over `version..=owner_pub_keys`. | |
| 1342 | +| preamble\_owner\_imc\_ecc\_sig | u32[24] | ECC384 signature by the manifest's own owner key over the IMC. | |
| 1343 | +| preamble\_owner\_imc\_pqc\_sig | u32[1157] | PQC signature by the manifest's own owner key over the IMC. | |
| 1344 | +| metadata\_entry\_count | u32 | Number of metadata entries. Must be `1..=32`. | |
| 1345 | +| metadata\_entries | Metadata[32] | Image Metadata Entries. Per-entry layout is identical to `SET_AUTH_MANIFEST` (see `AUTH_MANIFEST_METADATA_ENTRY` above). | |
| 1346 | + |
| 1347 | + |
| 1348 | +The response is a `MailboxRespHeader` (no payload). |
| 1047 | 1349 | |
| 1048 | 1350 | |
| 1049 | 1351 | ### AUTHORIZE_AND_STASH |
| 1050 | 1352 | |
| 1353 | +The SoC uses this command to request authorization of its various SoC images. This command has the option to receive the image hash directly from SoC or from an external source (e.g., SHA Acc). |
| 1354 | + |
| 1355 | +The SoC uses this command repeatedly to ask for authorization to run its different images. The Runtime will verify that the image hash is contained in the IMC and will allow or reject the image based on that check. The command also enables stashing of the image hash by default with an option to skip stashing if needed. The SVN field is intended for anti-rollback protection. |
| 1356 | + |
| 1357 | + |
| 1051 | 1358 | Command Code: `0x4154_5348` ("ATSH") |
| 1052 | 1359 | |
| 1053 | | -Privilege Level: PL0 or PL1; stashing the measurement requires PL0, so a PL1 caller must set the `SKIP_STASH` flag |
| 1054 | | - |
| 1055 | 1360 | *Table: `AUTHORIZE_AND_STASH` input arguments* |
| 1056 | 1361 | |
| 1057 | | -| **Name** | **Type** | **Description** | |
| 1058 | | -| ------------ | -------- | --------------- | |
| 1362 | +| **Name** | **Type** | **Description** |
| 1363 | +| ------------| -------- | --------------- |
| 1059 | 1364 | | chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. | |
| 1060 | 1365 | | fw_id | u8[4] | Firmware id of the image, in little-endian format | |
| 1061 | | -| measurement | u8[48] | Digest of the image requested for authorization | |
| 1366 | +| measurement | u8[48] | Digest of the image requested for authorization. The `source` field needs to be set to '1` for InRequest, otherwise<br />this field is ignored. | |
| 1062 | 1367 | | context | u8[48] | Context field for `svn`; e.g., a hash of the public key that authenticated the SVN. | |
| 1063 | | -| svn | u32 | SVN | |
| 1368 | +| svn | u32 | The version of the image | |
| 1064 | 1369 | | flags | u32 | See AUTHORIZE_AND_STASH_FLAGS below | |
| 1065 | | -| source | u32 | Enumeration values: { InRequest(1) } | |
| 1370 | +| source | u32 | This field identifies the source of the digest to be used to compare with the SoC's<br />SHA digest in the SoC Manifest<br /><br />Values<br />1 - InRequest - Use the hash in the 'measurement' field of this command<br /><br />2 - LoadAddress - The image located in the `ImageLoadAddress` will be streamed to the SHA Accelerator to <br /> retrieve the digest that will be used for authorization.<br />3 - ImageStagingAddress - The image located in the `StagingAddress` will be streamed to the SHA Accelerator to<br /> retrieve the digest that will be used for authorization | |
| 1371 | +| image_size | u32 | The size of the image to hash. Only valid if source is `ImageLoadAddress` or `StagingAddress` | |
| 1066 | 1372 | |
| 1067 | 1373 | |
| 1068 | 1374 | *Table: `AUTHORIZE_AND_STASH_FLAGS` input flags* |
| 1069 | | - |
| 1070 | 1375 | | **Name** | **Value** | |
| 1071 | | -| ------------ | ------------ | |
| 1376 | +| ----------- | --------- | |
| 1072 | 1377 | | SKIP\_STASH | 1 << 0 | |
| 1073 | 1378 | |
| 1074 | 1379 | |
| 1075 | 1380 | *Table: `AUTHORIZE_AND_STASH` output arguments* |
| 1076 | | -| **Name** | **Type** | **Description** |
| 1077 | | -| ----------------| -------- | --------------- |
| 1381 | +| **Name** | **Type** | **Description** | |
| 1382 | +| --------------- | -------- | -------------------------------------------------------------------------- | |
| 1078 | 1383 | | chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. | |
| 1079 | 1384 | | fips_status | u32 | Indicates if the command is FIPS approved or an error. | |
| 1080 | | -| auth_req_result | u32 | AUTHORIZE_IMAGE (0xDEADC0DE), IMAGE_NOT_AUTHORIZED (0x21523F21) or IMAGE_HASH_MISMATCH (0x8BFB95CB) | |
| 1081 | | - |
| 1082 | | - |
| 1083 | | -### GET\_IDEVID\_CSR |
| 1084 | | - |
| 1085 | | -Command Code: `0x4944_4352` ("IDCR") |
| 1086 | | - |
| 1087 | | -Privilege Level: PL0 or PL1 |
| 1088 | | - |
| 1089 | | -*Table: `GET_IDEVID_CSR` input arguments* |
| 1385 | +| auth_req_result | u32 | IMAGE_AUTHORIZED_VENDOR_OWNER (0xDEADC0DE, alias of legacy `AUTHORIZE_IMAGE`/`IMAGE_AUTHORIZED`), IMAGE_AUTHORIZED_OWNER_ONLY (0xC0DEDEAD), IMAGE_NOT_AUTHORIZED (0x21523F21) or IMAGE_HASH_MISMATCH (0x8BFB95CB). Lookup order: vendor + owner collection first, then owner-only collection populated by `SET_OWNER_AUTH_MANIFEST`. Active firmware IDs are unique across the collections, and the success value indicates which collection produced the match. | |
| 1386 | + |
| 1387 | + |
| 1388 | +### GET_IMAGE_INFO |
| 1389 | + |
| 1390 | +The MCU uses this command to retrieve the active Image Metadata Entry for a |
| 1391 | +firmware ID. The Runtime searches the vendor + owner Image Metadata Collection |
| 1392 | +first, then the owner-only collection installed by |
| 1393 | +[`SET_OWNER_AUTH_MANIFEST`](#set_owner_auth_manifest). Active firmware IDs are |
| 1394 | +unique across the collections, so the response is unambiguous. |
| 1395 | + |
| 1396 | +Command Code: `0x494D_4530` ("IME0") |
| 1397 | + |
| 1398 | +*Table: `GET_IMAGE_INFO` input arguments* |
| 1399 | + |
| 1400 | +| **Name** | **Type** | **Description** | |
| 1401 | +| -------------- | -------------- | ------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- | |
| 1402 | +| chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. | |
| 1403 | + |
| 1404 | +| fw_id | u32 | Firmware id of the image, in little-endian format |
| 1405 | + |
| 1406 | +*Table: `GET_IMAGE_INFO` output arguments* |
| 1407 | + |
| 1408 | +| **Name** | **Type** | **Description** | |
| 1409 | +| -------------- | -------------- | ------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- | |
| 1410 | +| chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. | |
| 1411 | +| fips_status | u32 | Indicates if the command is FIPS approved or an error. | |
| 1412 | +| Component_id | u32 | This corresponds to the `Component Id` field in the [SoC Manifest](https://github.com/chipsalliance/caliptra-sw/blob/caliptra-2.0/auth-manifest/README.md) | |
| 1413 | +| flags | u32 | This corresponds to the `flags` field in the [SoC Manifest](https://github.com/chipsalliance/caliptra-sw/blob/caliptra-2.0/auth-manifest/README.md) | |
| 1414 | +| Image Load Address High | u32 | This corresponds to the `Image Load Address High` field in the [SoC Manifest](https://github.com/chipsalliance/caliptra-sw/blob/caliptra-2.0/auth-manifest/README.md) | |
| 1415 | +| Image Load Address Low | u32 | This corresponds to the `Image Load Address Low` field in the [SoC Manifest](https://github.com/chipsalliance/caliptra-sw/blob/caliptra-2.0/auth-manifest/README.md) | |
| 1416 | +| Staging Address High | u32 | This corresponds to the `Staging Address High` field in the [SoC Manifest](https://github.com/chipsalliance/caliptra-sw/blob/caliptra-2.0/auth-manifest/README.md) | |
| 1417 | +| Staging Address Low | u32 | This corresponds to the `Staging Address Low` field in the [SoC Manifest](https://github.com/chipsalliance/caliptra-sw/blob/caliptra-2.0/auth-manifest/README.md) | |
| 1418 | +| digest | u8[48] | SHA-384 digest of the image. **Only present in FW 2.0.2+ and 2.1.1+.** | |
| 1419 | + |
| 1420 | + |
| 1421 | +### ACTIVATE_FIRMWARE |
| 1422 | + |
| 1423 | +The MCU uses this command to 'activate' the image that has been previously downloaded through PLDM - T5. |
| 1424 | +For the full behavior of this command, refer to the [Subsystem Support for Hitless Updates](https://github.com/chipsalliance/Caliptra/blob/main/doc/Caliptra.md#subsystem-support-for-hitless-updates) specification. |
| 1425 | + |
| 1426 | +Command Code: `0x4143_5446` ("ACTF") |
| 1427 | + |
| 1428 | +*Table: `ACTIVATE_FIRMWARE` input arguments* |
| 1429 | + |
| 1430 | +| **Name** | **Type** | **Description** | |
| 1431 | +| -------------- | -------------- | --------------------------------------------------------------------------- | |
| 1432 | +| chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. | |
| 1433 | +| count | u32 | Number of image_ids to activate. Item count of image_ids array parameter | |
| 1434 | +| mcu_image_size | u32 | Size of MCU image, if included in the activation | |
| 1435 | +| image_ids | Array of u8[4] | Array of Image ids in little-endian format | |
| 1436 | + |
| 1437 | + |
| 1438 | +*Table: `ACTIVATE_FIRMWARE` output arguments* |
| 1439 | + |
| 1440 | +| **Name** | **Type** | **Description** | |
| 1441 | +| -------------- | -------------- | -------------------------------------------------------------------------- | |
| 1442 | +| chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. | |
| 1443 | +| fips_status | u32 | Indicates if the command is FIPS approved or an error. | |
| 1444 | + |
| 1445 | + |
| 1446 | +## Mailbox commands: Cryptographic Mailbox (2.0) |
| 1447 | + |
| 1448 | +These commands are used by the [Cryptograhic Mailbox](#cryptographic-mailbox-commands-new-in-20) system. |
| 1449 | + |
| 1450 | +### CM_SHA_INIT |
| 1451 | + |
| 1452 | +This starts the computation of a SHA hash of data, which may be larger than a single mailbox command allows. It also supports additional algorithms. |
| 1453 | + |
| 1454 | +**Note:** ROM provides a simpler one-shot `CM_SHA` command for hashing data in a single operation. However, that command is ROM-only and is not available in runtime. For runtime, use these streaming commands (CM_SHA_INIT, CM_SHA_UPDATE, CM_SHA_FINAL) which support contexts and incremental hashing of large data. |
| 1455 | + |
| 1456 | +The sequence to use these are: |
| 1457 | +* 1 `CM_SHA_INIT` command |
| 1458 | +* 0 or more `CM_SHA_UPDATE` commands |
| 1459 | +* 1 `CM_SHA_FINAL` command |
| 1460 | + |
| 1461 | +For each command, the context from the previous command's output must be passed as an input. |
| 1462 | + |
| 1463 | +The `SHA_CONTEXT_SIZE` is always exactly 200 bytes long. |
| 1464 | + |
| 1465 | +The maximum supported data size for the SHA commands is 4096 bytes. |
| 1466 | + |
| 1467 | +Command Code: `0x434D_5349` ("CMSI") |
| 1468 | + |
| 1469 | +*Table: `CM_SHA_INIT` input arguments* |
| 1470 | + |
| 1471 | +| **Name** | **Type** | **Description** | |
| 1472 | +| -------------- | ------------- | ------------------ | |
| 1473 | +| chksum | u32 || |
| 1474 | +| hash algorithm | u32 | Enum. | |
| 1475 | +||| Value 0 = reserved | |
| 1476 | +||| Value 1 = SHA2-384 | |
| 1477 | +||| Value 2 = SHA2-512 | |
| 1478 | +| data size | u32 || |
| 1479 | +| data | u8[data size] | Data to hash | |
| 1480 | + |
| 1481 | + |
| 1482 | +*Table: `CM_SHA_INIT` output arguments* |
| 1483 | +| **Name** | **Type** | **Description** | |
| 1484 | +| ------------ | -------------------- | ------------------------------------------ | |
| 1485 | +| chksum | u32 || |
| 1486 | +| fips_status | u32 | FIPS approved or an error | |
| 1487 | +| context | u8[SHA_CONTEXT_SIZE] | Passed to `CM_SHA_UPDATE` / `CM_SHA_FINAL` | |
| 1488 | + |
| 1489 | + |
| 1490 | +*Table: `CM_SHA_INIT` / `CM_SHA_UPDATE` / `CM_SHA_FINAL` internal context* |
| 1491 | +| **Name** | **Type** | **Description** | |
| 1492 | +| ----------------- | -------- | --------------- | |
| 1493 | +| input buffer | u8[128] || |
| 1494 | +| intermediate hash | u8[64] || |
| 1495 | +| length | u32 || |
| 1496 | +| hash algorithm | u32 || |
| 1497 | + |
| 1498 | + |
| 1499 | +### CM_SHA_UPDATE |
| 1500 | + |
| 1501 | +This continues a SHA computation started by `CM_SHA_INIT` or from another `CM_SHA_UPDATE`. |
| 1502 | + |
| 1503 | +The context MUST be passed in from `CM_SHA_INIT` or `CM_SHA_UPDATE`. |
| 1504 | + |
| 1505 | +Command Code: `0x434D_5355` ("CMSU") |
| 1506 | + |
| 1507 | +*Table: `CM_SHA_UPDATE` input arguments* |
| 1508 | +| **Name** | **Type** | **Description** | |
| 1509 | +| ------------ | -------------------- | ------------------------------------ | |
| 1510 | +| chksum | u32 || |
| 1511 | +| context | u8[SHA_CONTEXT_SIZE] | From `CM_SHA_INIT` / `CM_SHA_UPDATE` | |
| 1512 | +| data size | u32 || |
| 1513 | +| data | u8[data size] | Data to hash | |
| 1514 | + |
| 1515 | + |
| 1516 | +*Table: `CM_SHA_UPDATE` output arguments* |
| 1517 | +| **Name** | **Type** | **Description** | |
| 1518 | +| ------------ | -------------------- | ------------------------------------------ | |
| 1519 | +| chksum | u32 || |
| 1520 | +| fips_status | u32 | FIPS approved or an error | |
| 1521 | +| context | u8[SHA_CONTEXT_SIZE] | Passed to `CM_SHA_UPDATE` / `CM_SHA_FINAL` | |
| 1522 | + |
| 1523 | + |
| 1524 | +### CM_SHA_FINAL |
| 1525 | + |
| 1526 | +This finalizes the computation of a SHA and produces the hash of all of the data. |
| 1527 | + |
| 1528 | +The context MUST be passed in from `CM_SHA_INIT` or `CMA_SHA_UPDATE`. |
| 1529 | + |
| 1530 | +Command Code: `0x434D_5346` ("CMSF") |
| 1531 | + |
| 1532 | +*Table: `CM_SHA_FINAL` input arguments* |
| 1533 | +| **Name** | **Type** | **Description** | |
| 1534 | +| ------------ | -------------------- | ------------------------------------ | |
| 1535 | +| chksum | u32 || |
| 1536 | +| context | u8[SHA_CONTEXT_SIZE] | From `CM_SHA_INIT` / `CM_SHA_UPDATE` | |
| 1537 | +| data size | u32 | May be 0 | |
| 1538 | +| data | u8[data size] | Data to hash | |
| 1539 | + |
| 1540 | + |
| 1541 | +*Table: `CM_SHA_FINAL` output arguments* |
| 1542 | +| **Name** | **Type** | **Description** | |
| 1543 | +| ----------- | ------------- | ------------------------- | |
| 1544 | +| chksum | u32 || |
| 1545 | +| fips_status | u32 | FIPS approved or an error | |
| 1546 | +| hash size | u32 || |
| 1547 | +| hash | u8[hash size] || |
| 1548 | + |
| 1549 | + |
| 1550 | +### CM\_HMAC |
| 1551 | + |
| 1552 | +Computes an HMAC according to [RFC 2104](https://datatracker.ietf.org/doc/html/rfc2104) with select SHA algorithm support. The data must fit into a single mailbox command. |
| 1553 | + |
| 1554 | +The CMK must have been created for HMAC / HKDF usage. |
| 1555 | + |
| 1556 | +Command Code: `0x434D_484D` ("CMHM") |
| 1557 | + |
| 1558 | +*Table: `CM_HMAC` input arguments* |
| 1559 | +| **Name** | **Type** | **Description** | |
| 1560 | +| -------------- | ------------- | ----------------- | |
| 1561 | +| chksum | u32 || |
| 1562 | +| CMK | CMK | CMK to use as key | |
| 1563 | +| hash algorithm | u32 | Enum. | |
| 1564 | +||| 0 = reserved | |
| 1565 | +||| 1 = SHA2-384 | |
| 1566 | +||| 2 = SHA2-512 | |
| 1567 | +| data size | u32 || |
| 1568 | +| data | u8[data size] | Data to MAC | |
| 1569 | + |
| 1570 | + |
| 1571 | + |
| 1572 | +*Table: `CM_HMAC` output arguments* |
| 1573 | +| **Name** | **Type** | **Description** | |
| 1574 | +| ----------- | ------------ | ------------------------- | |
| 1575 | +| chksum | u32 || |
| 1576 | +| fips_status | u32 | FIPS approved or an error | |
| 1577 | +| mac size | u32 || |
| 1578 | +| mac | u8[mac size] || |
| 1579 | + |
| 1580 | + |
| 1581 | +### CM_HMAC_KDF_COUNTER |
| 1582 | + |
| 1583 | +Implements HMAC KDF in Counter Moder as specified in as specified in [RFC 5869](https://www.rfc-editor.org/rfc/rfc5869.html) and [NIST SP800-108](https://csrc.nist.gov/pubs/sp/800/108/r1/upd1/final) Section 4.1 (KDF in Counter Mode, Section 4.1). |
| 1584 | + |
| 1585 | +The CMK must have been created for HMAC usage. |
| 1586 | + |
| 1587 | +The output length will be automatically chosen to match the key usage. |
| 1588 | + |
| 1589 | +Command Code: `0x434D_4B43` ("CMKC") |
| 1590 | + |
| 1591 | +*Table: `CM_HMAC_KDF_COUNTER` input arguments* |
| 1592 | +| **Name** | **Type** | **Description** | |
| 1593 | +| -------------- | -------------- | ------------------------- | |
| 1594 | +| chksum | u32 || |
| 1595 | +| KIN CMK | CMK | Input key | |
| 1596 | +| hash algorithm | u32 | Enum. | |
| 1597 | +||| Value 0 = reserved | |
| 1598 | +||| Value 1 = SHA2-384 | |
| 1599 | +||| Value 2 = SHA2-512 | |
| 1600 | +| key usage | u32 | usage tag of output key | |
| 1601 | +| key size | u32 | size (in bytes) for the output key; MUST be valid for the key usage | |
| 1602 | +| label size | u32 || |
| 1603 | +| label | u8[label size] || |
| 1604 | + |
| 1605 | + |
| 1606 | +*Table: `CM_HMAC_KDF_COUNTER` output arguments* |
| 1607 | +| **Name** | **Type** | **Description** | |
| 1608 | +| ----------- | -------- | --------------------------------------- | |
| 1609 | +| chksum | u32 || |
| 1610 | +| fips_status | u32 | FIPS approved or an error | |
| 1611 | +| KOUT CMK | CMK | CMK that stores the output key material | |
| 1612 | + |
| 1613 | + |
| 1614 | +### CM_HKDF_EXTRACT |
| 1615 | + |
| 1616 | +Implements HKDF-Extract as specified in [RFC 5869](https://www.rfc-editor.org/rfc/rfc5869.html). |
| 1617 | + |
| 1618 | +The CMKs for IKM and salt must have been created for HMAC usage. The output will be tagged for HMAC usage. |
| 1619 | + |
| 1620 | +Use CM_IMPORT to import non-secret (plaintext) salt or IKMs to use |
| 1621 | +with HKDF-Extract after right-padding to 48 or 64 bytes with zeros. |
| 1622 | + |
| 1623 | +Command Code: `0x434D_4B54` ("CMKT") |
| 1624 | + |
| 1625 | +*Table: `CM_HKDF_EXTRACT` input arguments* |
| 1626 | +| **Name** | **Type** | **Description** | |
| 1627 | +| -------------- | -------- | ------------------------- | |
| 1628 | +| chksum | u32 || |
| 1629 | +| hash algorithm | u32 | Enum. | |
| 1630 | +||| Value 0 = reserved | |
| 1631 | +||| Value 1 = SHA2-384 | |
| 1632 | +||| Value 2 = SHA2-512 | |
| 1633 | +| salt CMK | CMK | Salt CMK. | |
| 1634 | +| IKM CMK | CMK | Input key material CMK | |
| 1635 | + |
| 1636 | + |
| 1637 | +*Table: `CM_HKDF_EXTRACT` output arguments* |
| 1638 | +| **Name** | **Type** | **Description** | |
| 1639 | +| ----------- | -------- | --------------------------------------- | |
| 1640 | +| chksum | u32 || |
| 1641 | +| fips_status | u32 | FIPS approved or an error | |
| 1642 | +| PRK CMK | u8[32] | CMK that stores the output (PRK) to use | |
| 1643 | +||| with HKDF-Expand | |
| 1644 | + |
| 1645 | + |
| 1646 | +### CM_HKDF_EXPAND |
| 1647 | + |
| 1648 | +Implements HKDF-Expand as specified in [RFC 5869](https://www.rfc-editor.org/rfc/rfc5869.html). |
| 1649 | + |
| 1650 | +The CMK must have been created for HMAC usage. |
| 1651 | + |
| 1652 | +The output length will be automatically chosen to match the key usage. |
| 1653 | + |
| 1654 | +Command Code: `0x434D_4B50` ("CMKP") |
| 1655 | + |
| 1656 | +*Table: `CM_HKDF_EXPAND` input arguments* |
| 1657 | +| **Name** | **Type** | **Description** | |
| 1658 | +| -------------- | ------------- | ------------------------------- | |
| 1659 | +| chksum | u32 || |
| 1660 | +| PRK CMK | CMK || |
| 1661 | +| hash algorithm | u32 | Enum. | |
| 1662 | +||| Value 0 = reserved | |
| 1663 | +||| Value 1 = SHA2-384 | |
| 1664 | +||| Value 2 = SHA2-512 | |
| 1665 | +| key usage | u32 | usage tag of output key | |
| 1666 | +| key size | u32 | size (in bytes) for the OKM; | |
| 1667 | +||| MUST be valid for the key usage | |
| 1668 | +| info size | u32 || |
| 1669 | +| info | u8[info size] || |
| 1670 | + |
| 1671 | + |
| 1672 | +*Table: `CM_HKDF_EXPAND` output arguments* |
| 1673 | +Command Code: `0x434D_4B43` ("CMKC") |
| 1674 | + |
| 1675 | +| **Name** | **Type** | **Description** | |
| 1676 | +| ----------- | -------- | --------------------------------------- | |
| 1677 | +| chksum | u32 || |
| 1678 | +| fips_status | u32 | FIPS approved or an error | |
| 1679 | +| OKM CMK | CMK | CMK that stores the output key material | |
| 1680 | + |
| 1681 | + |
| 1682 | + |
| 1683 | +### CM_MLDSA_PUBLIC_KEY |
| 1684 | + |
| 1685 | +Returns the public key associated with the MLDSA-87 key (seed) in a CMK. |
| 1686 | + |
| 1687 | +The public key format is described in [FIPS 204](https://csrc.nist.gov/pubs/fips/204/final). |
| 1688 | + |
| 1689 | +Command Code: `0x434D_4D50` ("CMMP") |
| 1690 | + |
| 1691 | +*Table: `CM_MLDSA_PUBLIC_KEY` input arguments* |
| 1692 | +| **Name** | **Type** | **Description** | |
| 1693 | +| -------- | -------- | ----------------- | |
| 1694 | +| chksum | u32 || |
| 1695 | +| CMK | CMK | Private key seed | |
| 1696 | + |
| 1697 | + |
| 1698 | +*Table: `CM_MLDSA_PUBLIC_KEY` output arguments* |
| 1699 | +| **Name** | **Type** | **Description** | |
| 1700 | +| ----------- | -------- | -------------------------- | |
| 1701 | +| chksum | u32 || |
| 1702 | +| fips_status | u32 | FIPS approved or an error | |
| 1703 | +| Public key | u8[2592] | Public key | |
| 1704 | + |
| 1705 | + |
| 1706 | +### CM_MLDSA_SIGN |
| 1707 | + |
| 1708 | +Signs the message with the MLDSA-87 key. |
| 1709 | + |
| 1710 | +The signature format is described in [FIPS 204](https://csrc.nist.gov/pubs/fips/204/final). |
| 1711 | + |
| 1712 | +Command Code: `0x434D_4D53` ("CMMS") |
| 1713 | + |
| 1714 | +*Table: `CM_MLDSA_SIGN` input arguments* |
| 1715 | +| **Name** | **Type** | **Description** | |
| 1716 | +| -------- | ------------ | ----------------- | |
| 1717 | +| chksum | u32 || |
| 1718 | +| CMK | CMK | Private key seed | |
| 1719 | +| data len | u32 | Length of message | |
| 1720 | +| data | u8[data len] | Message to sign | |
| 1721 | + |
| 1722 | + |
| 1723 | +*Table: `CM_MLDSA_SIGN` output arguments* |
| 1724 | +| **Name** | **Type** | **Description** | |
| 1725 | +| ----------- | -------- | -------------------------- | |
| 1726 | +| chksum | u32 || |
| 1727 | +| fips_status | u32 | FIPS approved or an error | |
| 1728 | +| signature | u8[4627] | Signature | |
| 1729 | +| padding | u8[1] || |
| 1730 | + |
| 1731 | + |
| 1732 | +### CM_MLDSA_VERIFY |
| 1733 | + |
| 1734 | +Verifies the signature against the message and MLDSA-87 key. |
| 1735 | + |
| 1736 | +The signature format is described in [FIPS 204](https://csrc.nist.gov/pubs/fips/204/final). |
| 1737 | + |
| 1738 | +The command will only return a success if the signature is valid. |
| 1739 | + |
| 1740 | +Command Code: `0x434D_4D56` ("CMMV") |
| 1741 | + |
| 1742 | +*Table: `CM_MLDSA_VERIFY` input arguments* |
| 1743 | +| **Name** | **Type** | **Description** | |
| 1744 | +| --------- | ------------ | ------------------ | |
| 1745 | +| chksum | u32 || |
| 1746 | +| CMK | CMK | Private key seed | |
| 1747 | +| signature | u8[4627] | Signature to check | |
| 1748 | +| padding | u8[1] || |
| 1749 | +| data len | u32 | Length of message | |
| 1750 | +| data | u8[data len] | Message to check | |
| 1751 | + |
| 1752 | + |
| 1753 | +*Table: `CM_MLDSA_VERIFY` output arguments* |
| 1754 | +| **Name** | **Type** | **Description** | |
| 1755 | +| ----------- | -------- | -------------------------- | |
| 1756 | +| chksum | u32 || |
| 1757 | +| fips_status | u32 | FIPS approved or an error | |
| 1758 | + |
| 1759 | + |
| 1760 | +### CM_ECDSA_PUBLIC_KEY |
| 1761 | + |
| 1762 | +Returns the public key associated with the ECDSA-384 key seed in a CMK. |
| 1763 | + |
| 1764 | +The public key consists of its `x` and `y` values described in [FIPS 186-5](https://csrc.nist.gov/pubs/fips/186-5/final) encoded in big-endian byte order. |
| 1765 | + |
| 1766 | +Command Code: `0x434D_4550` ("CMEP") |
| 1767 | + |
| 1768 | +*Table: `CM_ECDSA_PUBLIC_KEY` input arguments* |
| 1769 | +| **Name** | **Type** | **Description** | |
| 1770 | +| -------- | -------- | ----------------- | |
| 1771 | +| chksum | u32 || |
| 1772 | +| CMK | CMK | Private key seed | |
| 1773 | + |
| 1774 | + |
| 1775 | +*Table: `CM_ECDSA_PUBLIC_KEY` output arguments* |
| 1776 | +| **Name** | **Type** | **Description** | |
| 1777 | +| ----------- | -------- | -------------------------- | |
| 1778 | +| chksum | u32 || |
| 1779 | +| fips_status | u32 | FIPS approved or an error | |
| 1780 | +| pubkey_x | u8[48] | The X BigNum of the ECDSA public key generated from the seed | |
| 1781 | +| pubkey_y | u8[48] | The Y BigNum of the ECDSA public key generated from the seed | |
| 1782 | + |
| 1783 | + |
| 1784 | +### CM_ECDSA_SIGN |
| 1785 | + |
| 1786 | +Signs the SHA384 hash of the message with the ECDSA-384 key. |
| 1787 | + |
| 1788 | +The signature consists of its `r` and `s` values described in [FIPS 186-5](https://csrc.nist.gov/pubs/fips/186-5/final) encoded in big-endian byte order. |
| 1789 | + |
| 1790 | +Command Code: `0x434D_5D53` ("CMES") |
| 1791 | + |
| 1792 | +*Table: `CM_ECDSA_SIGN` input arguments* |
| 1793 | +| **Name** | **Type** | **Description** | |
| 1794 | +| -------- | ------------ | ----------------- | |
| 1795 | +| chksum | u32 || |
| 1796 | +| CMK | CMK | Private key seed | |
| 1797 | +| data len | u32 | Length of message | |
| 1798 | +| data | u8[data len] | Message to sign | |
| 1799 | + |
| 1800 | + |
| 1801 | +*Table: `CM_ECDSA_SIGN` output arguments* |
| 1802 | +| **Name** | **Type** | **Description** | |
| 1803 | +| ------------ | -------- | ------------------------------------ | |
| 1804 | +| chksum | u32 || |
| 1805 | +| fips_status | u32 | FIPS approved or an error | |
| 1806 | +| signature_r | u8[48] | The R BigNum of the ECDSA signature | |
| 1807 | +| signature_s | u8[48] | The S BigNum of the ECDSA signature | |
| 1808 | + |
| 1809 | + |
| 1810 | +### CM_ECDSA_VERIFY |
| 1811 | + |
| 1812 | +Verifies the signature against the SHA384 hash of the message and ECDSA-384 key. |
| 1813 | + |
| 1814 | +The signature consists of its `r` and `s` values described in [FIPS 186-5](https://csrc.nist.gov/pubs/fips/186-5/final) encoded in big-endian byte order. |
| 1815 | + |
| 1816 | +The command will only return a success if the signature is valid. |
| 1817 | + |
| 1818 | +Command Code: `0x434D_4556` ("CMEV") |
| 1819 | + |
| 1820 | +*Table: `CM_ECDSA_VERIFY` input arguments* |
| 1821 | +| **Name** | **Type** | **Description** | |
| 1822 | +| ------------ | ------------ | ----------------------------------- | |
| 1823 | +| chksum | u32 || |
| 1824 | +| CMK | CMK | Private key seed | |
| 1825 | +| signature_r | u8[48] | The R BigNum of an ECDSA signature | |
| 1826 | +| signature_s | u8[48] | The S BigNum of an ECDSA signature | |
| 1827 | +| data len | u32 | Length of message | |
| 1828 | +| data | u8[data len] | Message to check | |
| 1829 | + |
| 1830 | + |
| 1831 | +*Table: `CM_ECDSA_VERIFY` output arguments* |
| 1832 | +| **Name** | **Type** | **Description** | |
| 1833 | +| ----------- | -------- | -------------------------- | |
| 1834 | +| chksum | u32 || |
| 1835 | +| fips_status | u32 | FIPS approved or an error | |
| 1836 | + |
| 1837 | + |
| 1838 | +### CM_AES_ENCRYPT_INIT |
| 1839 | + |
| 1840 | +Generic AES operation for unauthenticated AES operations. |
| 1841 | +AES GCM operations use separate commands elsewhere. |
| 1842 | + |
| 1843 | +AES-256-CBC only supports using a random 128-bit IV. |
| 1844 | + |
| 1845 | +For CBC, the size must be a multiple of 16 bytes. |
| 1846 | +CTR mode supports input of any size up to the maximum cryptographic mailbox size. |
| 1847 | + |
| 1848 | +The CMK must have been created for AES usage. |
| 1849 | + |
| 1850 | +Command Code: `0x434D_4349` ("CMCI") |
| 1851 | + |
| 1852 | +*Table: `CM_AES_ENCRYPT_INIT` input arguments* |
| 1853 | +| **Name** | **Type** | **Description** | |
| 1854 | +| -------------- | ------------------ | ------------------------------------- | |
| 1855 | +| chksum | u32 || |
| 1856 | +| CMK | CMK | CMK of the key to use to encrypt | |
| 1857 | +| mode/flags | u32 | Requested mode and flags. | |
| 1858 | +||| 0 = Reserved | |
| 1859 | +||| 1 = CBC | |
| 1860 | +||| 2 = CTR | |
| 1861 | +| plaintext size | u32 | MUST be non-zero | |
| 1862 | +| plaintext | u8[plaintext size] | Data to encrypt | |
| 1863 | + |
| 1864 | + |
| 1865 | +*Table: `CM_AES_ENCRYPT_INIT` output arguments* |
| 1866 | +| **Name** | **Type** | **Description** | |
| 1867 | +| --------------- | ------------------- | -------------------------------- | |
| 1868 | +| chksum | u32 || |
| 1869 | +| fips_status | u32 | FIPS approved or an error | |
| 1870 | +| context | AES_CONTEXT || |
| 1871 | +| iv | u8[16] || |
| 1872 | +| ciphertext size | u32 || |
| 1873 | +| ciphertext | u8[ciphertext size] | Output encrypted data | |
| 1874 | + |
| 1875 | + |
| 1876 | +The encrypted and authenticated context's internal structure will be: |
| 1877 | + |
| 1878 | +*Table: internal context for CM_AES_* operations* |
| 1879 | +| **Name** | **Type** | **Description** | |
| 1880 | +| -------------- | -------- | ------------------------------ | |
| 1881 | +| mode | u32 || |
| 1882 | +| key | u8[32] || |
| 1883 | +| iv | u8[16] || |
| 1884 | +| fips_status | u8 | 1 = FIPS valid | |
| 1885 | +| reserved | u8[75] | Reserved for additional fields | |
| 1886 | + |
| 1887 | + |
| 1888 | +The size of the (encrypted) context is always exactly 156 bytes, |
| 1889 | +and we will use the type `AES_CONTEXT` to represent `u8[156]`. |
| 1890 | + |
| 1891 | +### CM_AES_ENCRYPT_UPDATE |
| 1892 | + |
| 1893 | +This continues (or finishes) an AES computation started by `CM_AES_ENCRYPT_INIT` or from another `CM_AES_ENCRYPT_UPDATE`. |
| 1894 | + |
| 1895 | +There is no `CM_AES_ENCRYPT_FINISH` since unauthenticated AES modes do not output a final tag. |
| 1896 | + |
| 1897 | +The context MUST be passed in from `CM_AES_ENCRYPT_INIT` or `CM_AES_ENCRYPT_UPDATE`. |
| 1898 | + |
| 1899 | +For CBC, the size must be a multiple of 16 bytes. |
| 1900 | +CTR mode supports input of any size up to the maximum cryptographic mailbox size. |
| 1901 | + |
| 1902 | +Command Code: `0x434D_4355` ("CMCU") |
| 1903 | + |
| 1904 | +*Table: `CM_AES_ENCRYPT_UPDATE` input arguments* |
| 1905 | +| **Name** | **Type** | **Description** | |
| 1906 | +| -------------- | ------------------ | ---------------- | |
| 1907 | +| chksum | u32 || |
| 1908 | +| context | AES_CONTEXT || |
| 1909 | +| plaintext size | u32 | MUST be non-zero | |
| 1910 | +| plaintext | u8[plaintext size] | Data to encrypt | |
| 1911 | + |
| 1912 | + |
| 1913 | +*Table: `CM_AES_ENCRYPT_UPDATE` output arguments* |
| 1914 | +| **Name** | **Type** | **Description** | |
| 1915 | +| -------------- | ------------------- | ------------------------- | |
| 1916 | +| chksum | u32 || |
| 1917 | +| fips_status | u32 | FIPS approved or an error | |
| 1918 | +| context | AES_CONTEXT || |
| 1919 | +| cipertext size | u32 || |
| 1920 | +| ciphertext | u8[ciphertext size] || |
| 1921 | + |
| 1922 | + |
| 1923 | +### CM_AES_DECRYPT_INIT |
| 1924 | + |
| 1925 | +Starts an AES-256 unauthenaticed decryption computation. |
| 1926 | + |
| 1927 | +The CMK must have been created for AES usage. |
| 1928 | + |
| 1929 | +For CBC, the size must be a multiple of 16 bytes. |
| 1930 | +CTR mode supports input of any size up to the maximum cryptographic mailbox size. |
| 1931 | + |
| 1932 | +The IV must match what was passed and returned from the initial encryption operation. |
| 1933 | + |
| 1934 | +Command Code: `0x434D_414A` ("CMAJ") |
| 1935 | + |
| 1936 | +*Table: `CM_AES_DECRYPT_INIT` input arguments* |
| 1937 | +| **Name** | **Type** | **Description** | |
| 1938 | +| --------------- | ------------------- | ------------------------- | |
| 1939 | +| chksum | u32 || |
| 1940 | +| CMK | CMK | CMK to use for decryption | |
| 1941 | +| mode/flags | u32 | Requested mode and flags. | |
| 1942 | +||| 0 = Reserved | |
| 1943 | +||| 1 = CBC | |
| 1944 | +||| 2 = CTR | |
| 1945 | +| iv | u8[16] || |
| 1946 | +| ciphertext size | u32 | MUST be non-zero | |
| 1947 | +| ciphertext | u8[ciphertext size] | Data to decrypt | |
| 1948 | + |
| 1949 | + |
| 1950 | +*Table: `CM_AES_DECRYPT_INIT` output arguments* |
| 1951 | +| **Name** | **Type** | **Description** | |
| 1952 | +| -------------- | ------------------ | ------------------------- | |
| 1953 | +| chksum | u32 || |
| 1954 | +| fips_status | u32 | FIPS approved or an error | |
| 1955 | +| context | AES_CONTEXT || |
| 1956 | +| plaintext size | u32 || |
| 1957 | +| plaintext | u8[plaintext size] | Decrypted data | |
| 1958 | + |
| 1959 | + |
| 1960 | +The encrypted and authenticated context's internal structure will be the same as for encryption. |
| 1961 | + |
| 1962 | +### CM_AES_DECRYPT_UPDATE |
| 1963 | + |
| 1964 | +This continues an AES computation started by `CM_AES_DECRYPT_INIT` or from another `CM_AES_DECRYPT_UPDATE`. |
| 1965 | + |
| 1966 | +There is no `CM_AES_DECRYPT_FINISH` since unauthenticated modes do not output a final tag. |
| 1967 | + |
| 1968 | +The context MUST be passed in from `CM_AES_DECRYPT_INIT` or `CM_AES_DECRYPT_UPDATE`. |
| 1969 | + |
| 1970 | +For CBC, the size must be a multiple of 16 bytes. |
| 1971 | +CTR mode supports input of any size up to the maximum cryptographic mailbox size. |
| 1972 | + |
| 1973 | +Command Code: `0x434D_4155` ("CMAU") |
| 1974 | + |
| 1975 | +*Table: `CM_AES_DECRYPT_UPDATE` input arguments* |
| 1976 | +| **Name** | **Type** | **Description** | |
| 1977 | +| --------------- | ------------------- | ---------------- | |
| 1978 | +| chksum | u32 || |
| 1979 | +| context | AES_CONTEXT || |
| 1980 | +| ciphertext size | u32 | MUST be non-zero | |
| 1981 | +| ciphertext | u8[ciphertext size] | Data to decrypt | |
| 1982 | + |
| 1983 | + |
| 1984 | +*Table: `CM_AES_DECRYPT_UPDATE` output arguments* |
| 1985 | +| **Name** | **Type** | **Description** | |
| 1986 | +| -------------- | ------------------ | ------------------------- | |
| 1987 | +| chksum | u32 || |
| 1988 | +| fips_status | u32 | FIPS approved or an error | |
| 1989 | +| context | AES_CONTEXT || |
| 1990 | +| plaintext size | u32 || |
| 1991 | +| plaintext | u8[plaintext size] | Decrypted data | |
| 1992 | + |
| 1993 | + |
| 1994 | +### CM_AES_GCM_ENCRYPT_INIT |
| 1995 | + |
| 1996 | +Currently only supports AES-256-GCM with a random 96-bit IV. |
| 1997 | + |
| 1998 | +Additional authenticated data (AAD) can only be passed during the `INIT` command, so is limited to the maximum cryptographic mailbox data size (4096 bytes). |
| 1999 | + |
| 2000 | +The CMK must have been created for AES usage, except if the SPDM mode flag has been used, in which case the CMK must have been created for HMAC usage. |
| 2001 | + |
| 2002 | +Command Code: `0x434D_4749` ("CMGI") |
| 2003 | + |
| 2004 | +*Table: `CM_AES_GCM_ENCRYPT_INIT` input arguments* |
| 2005 | +| **Name** | **Type** | **Description** | |
| 2006 | +| -------------- | ------------------ | -------------------------------- | |
| 2007 | +| chksum | u32 || |
| 2008 | +| reserved | u32 || |
| 2009 | +| CMK | CMK | CMK of the key to use to encrypt | |
| 2010 | +| aad size | u32 || |
| 2011 | +| aad | u8[aad size] | Additional authenticated data | |
| 2012 | + |
| 2013 | + |
| 2014 | +*Table: `CM_AES_GCM_ENCRYPT_INIT` output arguments* |
| 2015 | +| **Name** | **Type** | **Description** | |
| 2016 | +| -------------- | ------------------- | -------------------------------- | |
| 2017 | +| chksum | u32 || |
| 2018 | +| fips_status | u32 | FIPS approved or an error | |
| 2019 | +| context | AES_GCM_CONTEXT || |
| 2020 | +| iv | u8[12] || |
| 2021 | + |
| 2022 | + |
| 2023 | +The encrypted and authenticated context's internal structure will be: |
| 2024 | + |
| 2025 | +*Table: internal context for CM_AES_GCM_ENCRYPT_* operations* |
| 2026 | +| **Name** | **Type** | **Description** | |
| 2027 | +| -------------- | -------- | --------------------------- | |
| 2028 | +| key | u8[32] || |
| 2029 | +| iv | u8[12] || |
| 2030 | +| aad length | u32 || |
| 2031 | +| GHASH state | u8[16] || |
| 2032 | +| current length | u32 | value mod 16 is buffer size | |
| 2033 | +| buffer | u8[16] || |
| 2034 | +| fips_status | u8 | 1 = FIPS valid | |
| 2035 | +| reserved | u8[15] || |
| 2036 | + |
| 2037 | + |
| 2038 | +The size of the (encrypted) context is always exactly 128 bytes, |
| 2039 | +and we will use the type `AES_GCM_CONTEXT` to represent `u8[128]` below. |
| 2040 | + |
| 2041 | + |
| 2042 | +### CM_AES_GCM_SPDM_ENCRYPT_INIT |
| 2043 | + |
| 2044 | +Derives the AES key and IV following the [SPDM 1.4](https://www.dmtf.org/dsp/dsp0274) and [Secured Messages using SPDM 1.1](https://www.dmtf.org/dsp/dsp0277) specifications. |
| 2045 | + |
| 2046 | +Currently only supports AES-256-GCM. |
| 2047 | + |
| 2048 | +Additional authenticated data (AAD) can only be passed during the `INIT` command, so is limited to the maximum cryptographic mailbox data size (4096 bytes). |
| 2049 | + |
| 2050 | +The CMK must have been created for **HMAC** usage. |
| 2051 | + |
| 2052 | +The CMK passed in should be the SPDM major secret CMK created for HMAC usage. The key and IV used for encryption shall follow the [SPDM 1.4](https://www.dmtf.org/dsp/dsp0274) section 12.7 derivation with `key_length` equal to 32 bytes and `iv_length` equal to 12 bytes. |
| 2053 | + |
| 2054 | +``` |
| 2055 | +EncryptionKey = HKDF-Expand(major-secret, bin_str5, key_length); |
| 2056 | +IV = HKDF-Expand(major-secret, bin_str6, iv_length); |
| 2057 | +bin_str5 = BinConcat(key_length, Version, "key", null); |
| 2058 | +bin_str6 = BinConcat(iv_length, Version, "iv", null); |
| 2059 | +``` |
| 2060 | + |
| 2061 | +The provided 64-bit message counter will be XOR'd with the IV to produce the message IV. The Secure SPDM standard requires the counter endianness flag to be little, but big endian is also supported to aid in compatibility with some implementations. |
| 2062 | + |
| 2063 | +Note that it is **critical** that the same CMK and counter never be used more than once when encrypting or decrypting in SPDM mode as doing so could compromise the plaintext of the messages. |
| 2064 | + |
| 2065 | +For the update and final operations, there are not any SPDM-specific commands; `CM_AES_GCM_ENCRYPT_UPDATE` and `CM_AES_GCM_ENCRYPT_FINAL` should be used. |
| 2066 | + |
| 2067 | +Command Code: `0x434D_5345` ("CMSE") |
| 2068 | + |
| 2069 | +*Table: `CM_AES_GCM_SPDM_ENCRYPT_INIT` input arguments* |
| 2070 | +| **Name** | **Type** | **Description** | |
| 2071 | +| ------------------ | ------------------ | --------------------------------- | |
| 2072 | +| chksum | u32 || |
| 2073 | +| spdm version | u8 | The value should be equal to the | |
| 2074 | +||| byte representation of the SPDM | |
| 2075 | +||| version, e.g., 0x13 = SPDM 1.3 | |
| 2076 | +| counter endianness | u8 | XOR the counter with the IV using | |
| 2077 | +||| the given endianness. | |
| 2078 | +||| 0 = Little endian (standard) | |
| 2079 | +||| 1 = Big endian | |
| 2080 | +| reserved | u8[2] | Reserved | |
| 2081 | +| counter | u8[8] | 8-byte counter in little-endian | |
| 2082 | +||| format that is XOR'd into the IV | |
| 2083 | +| CMK | CMK | CMK of the key to use to encrypt | |
| 2084 | +| aad size | u32 || |
| 2085 | +| aad | u8[aad size] | Additional authenticated data | |
| 2086 | + |
| 2087 | + |
| 2088 | +*Table: `CM_AES_GCM_SPDM_ENCRYPT_INIT` output arguments* |
| 2089 | +| **Name** | **Type** | **Description** | |
| 2090 | +| -------------- | ------------------- | -------------------------------- | |
| 2091 | +| chksum | u32 || |
| 2092 | +| fips_status | u32 | FIPS approved or an error | |
| 2093 | +| context | AES_GCM_CONTEXT || |
| 2094 | + |
| 2095 | + |
| 2096 | +Unlike in the standard AES GCM encrypt init command, the IV is *not* returned. |
| 2097 | + |
| 2098 | +The encrypted and authenticated context's internal structure will be the same as for described in [CM_AES_GCM_ENCRYPT_INIT](#CM_AES_GCM_ENCRYPT_INIT). |
| 2099 | + |
| 2100 | +### CM_AES_GCM_ENCRYPT_UPDATE |
| 2101 | + |
| 2102 | +This continues an AES computation started by `CM_AES_GCM_ENCRYPT_INIT` or from another `CM_AES_GCM_ENCRYPT_UPDATE`. |
| 2103 | + |
| 2104 | +The context MUST be passed in from `CM_AES_GCM_ENCRYPT_INIT` or `CM_AES_GCM_ENCRYPT_UPDATE`. |
| 2105 | + |
| 2106 | +Command Code: `0x434D_4755` ("CMGU") |
| 2107 | + |
| 2108 | +*Table: `CM_AES_GCM_ENCRYPT_UPDATE` input arguments* |
| 2109 | +| **Name** | **Type** | **Description** | |
| 2110 | +| -------------- | ------------------ | ---------------- | |
| 2111 | +| chksum | u32 || |
| 2112 | +| context | AES_GCM_CONTEXT || |
| 2113 | +| plaintext size | u32 | MUST be non-zero | |
| 2114 | +| plaintext | u8[plaintext size] | Data to encrypt | |
| 2115 | + |
| 2116 | + |
| 2117 | +*Table: `CM_AES_GCM_ENCRYPT_UPDATE` output arguments* |
| 2118 | +| **Name** | **Type** | **Description** | |
| 2119 | +| -------------- | ------------------- | ------------------------------- | |
| 2120 | +| chksum | u32 || |
| 2121 | +| fips_status | u32 | FIPS approved or an error | |
| 2122 | +| context | AES_GCM_CONTEXT || |
| 2123 | +| cipertext size | u32 | could be greater than plaintext by 16 bytes | |
| 2124 | +| ciphertext | u8[ciphertext size] || |
| 2125 | + |
| 2126 | + |
| 2127 | +### CM_AES_GCM_ENCRYPT_FINAL |
| 2128 | + |
| 2129 | +This finalizes the computation of the AES GCM encryption and produces the final ciphertext and tag. |
| 2130 | + |
| 2131 | +The context MUST be passed in from `CM_AES_GCM_ENCRYPT_INIT` or `CM_AES_GCM_ENCRYPT_UPDATE`. |
| 2132 | + |
| 2133 | +Command Code: `0x434D_4746` ("CMGF") |
| 2134 | + |
| 2135 | +*Table: `CM_AES_GCM_ENCRYPT_FINAL` input arguments* |
| 2136 | +| **Name** | **Type** | **Description** | |
| 2137 | +| -------------- | ------------------ | --------------- | |
| 2138 | +| chksum | u32 || |
| 2139 | +| context | AES_GCM_CONTEXT || |
| 2140 | +| plaintext size | u32 | MAY be 0 | |
| 2141 | +| plaintext | u8[plaintext size] | Data to encrypt | |
| 2142 | + |
| 2143 | + |
| 2144 | +*Table: `CM_AES_GCM_ENCRYPT_FINAL` output arguments* |
| 2145 | +| **Name** | **Type** | **Description** | |
| 2146 | +| -------------- | ------------------- | -------------------------------- | |
| 2147 | +| chksum | u32 || |
| 2148 | +| fips_status | u32 | FIPS approved or an error | |
| 2149 | +| tag | u8[16] || |
| 2150 | +| cipertext size | u32 | could be greater than plaintext by 16 bytes | |
| 2151 | +| ciphertext | u8[ciphertext size] || |
| 2152 | + |
| 2153 | + |
| 2154 | +The tag returned will always be 16 bytes. Shorter tags can be constructed by truncating. |
| 2155 | + |
| 2156 | +### CM_AES_GCM_DECRYPT_INIT |
| 2157 | + |
| 2158 | +Starts an AES-256-GCM decryption computation. |
| 2159 | + |
| 2160 | +Currently only supports AES-256-GCM with a 96-bit IV. |
| 2161 | + |
| 2162 | +Additional authenticated data (AAD) can only be passed during the `INIT` command, so is limited to the maximum cryptographic mailbox data size (4096 bytes). |
| 2163 | + |
| 2164 | +The AAD and IV must match what was passed and returned from the encryption operation. |
| 2165 | + |
| 2166 | +The CMK must have been created for **AES** usage. |
| 2167 | + |
| 2168 | +Command Code: `0x434D_4449` ("CMDI") |
| 2169 | + |
| 2170 | +*Table: `CM_AES_GCM_DECRYPT_INIT` input arguments* |
| 2171 | +| **Name** | **Type** | **Description** | |
| 2172 | +| --------------- | ------------ | -------------------------------- | |
| 2173 | +| chksum | u32 || |
| 2174 | +| reserved | u32 | Reserved | |
| 2175 | +| CMK | CMK | CMK to use for decryption | |
| 2176 | +| iv | u8[12] || |
| 2177 | +| aad size | u32 || |
| 2178 | +| aad | u8[aad size] | Additional authenticated data | |
| 2179 | + |
| 2180 | + |
| 2181 | +*Table: `CM_AES_GCM_DECRYPT_INIT` output arguments* |
| 2182 | +| **Name** | **Type** | **Description** | |
| 2183 | +| -------------- | ------------------ | ------------------------- | |
| 2184 | +| chksum | u32 || |
| 2185 | +| fips_status | u32 | FIPS approved or an error | |
| 2186 | +| context | AES_GCM_CONTEXT || |
| 2187 | + |
| 2188 | + |
| 2189 | +The encrypted and authenticated context's internal structure will be the same as for encryption. |
| 2190 | + |
| 2191 | +### CM_AES_SPDM_GCM_DECRYPT_INIT |
| 2192 | + |
| 2193 | +Starts an AES-256-GCM decryption computation in SPDM mode. |
| 2194 | + |
| 2195 | +Currently only supports AES-256-GCM with a 96-bit IV. |
| 2196 | + |
| 2197 | +Additional authenticated data (AAD) can only be passed during the `INIT` command, so is limited to the maximum cryptographic mailbox data size (4096 bytes). |
| 2198 | + |
| 2199 | +The AAD must match what was passed and returned from the encryption operation. |
| 2200 | + |
| 2201 | +The CMK must have been created for **HMAC** usage. |
| 2202 | + |
| 2203 | +The CMK passed in should be the SPDM major secret CMK created for HMAC usage. The key and IV used for encryption shall follow the [SPDM 1.4](https://www.dmtf.org/dsp/dsp0274) section 12.7 derivation with `key_length` 256 and `iv_length` 96. |
| 2204 | + |
| 2205 | +``` |
| 2206 | +EncryptionKey = HKDF-Expand(major-secret, bin_str5, key_length); |
| 2207 | +IV = HKDF-Expand(major-secret, bin_str6, iv_length); |
| 2208 | +bin_str5 = BinConcat(key_length, Version, "key", null); |
| 2209 | +bin_str6 = BinConcat(iv_length, Version, "iv", null); |
| 2210 | +``` |
| 2211 | + |
| 2212 | +The provided 64-bit message counter will be XOR'd with the IV to produce the message IV. The Secure SPDM standard requires the counter endianness flag to be little, but big endian is also supported to aid in compatibility with some implementations. |
| 2213 | + |
| 2214 | +Note that it is **critical** that the same CMK and counter never be used more than once when encrypting or decrypting in SPDM mode as doing so could compromise the plaintext of the messages. |
| 2215 | + |
| 2216 | +Command Code: `0x434D_5344` ("CMSD") |
| 2217 | + |
| 2218 | +*Table: `CM_AES_GCM_SPDM_DECRYPT_INIT` input arguments* |
| 2219 | +| **Name** | **Type** | **Description** | |
| 2220 | +| ------------------ | ------------------ | --------------------------------- | |
| 2221 | +| chksum | u32 || |
| 2222 | +| spdm version | u8 | The value should be equal to the | |
| 2223 | +||| byte representation of the SPDM | |
| 2224 | +||| version, e.g., 0x13 = SPDM 1.3 | |
| 2225 | +| counter endianness | u8 | XOR the counter with the IV using | |
| 2226 | +||| the given endianness. | |
| 2227 | +||| 0 = Little endian (standard) | |
| 2228 | +||| 1 = Big endian | |
| 2229 | +| reserved | u8[2] | Reserved | |
| 2230 | +| counter | u8[8] | 8-byte counter in little-endian | |
| 2231 | +||| format that is XOR'd into the IV | |
| 2232 | +| CMK | CMK | CMK to use for decryption | |
| 2233 | +| aad size | u32 || |
| 2234 | +| aad | u8[aad size] | Additional authenticated data | |
| 2235 | + |
| 2236 | + |
| 2237 | +*Table: `CM_AES_GCM_SPDM_DECRYPT_INIT` output arguments* |
| 2238 | +| **Name** | **Type** | **Description** | |
| 2239 | +| -------------- | ------------------ | ------------------------- | |
| 2240 | +| chksum | u32 || |
| 2241 | +| fips_status | u32 | FIPS approved or an error | |
| 2242 | +| context | AES_GCM_CONTEXT || |
| 2243 | + |
| 2244 | + |
| 2245 | +The encrypted and authenticated context's internal structure will be the same as for encryption. |
| 2246 | + |
| 2247 | +### CM_AES_GCM_DECRYPT_UPDATE |
| 2248 | + |
| 2249 | +This continues an AES computation started by `CM_AES_GCM_DECRYPT_INIT` or from another `CM_AES_GCM_DECRYPT_UPDATE`. |
| 2250 | + |
| 2251 | +The context MUST be passed in from `CM_AES_GCM_DECRYPT_INIT` or `CM_AES_GCM_DECRYPT_UPDATE`. |
| 2252 | + |
| 2253 | +Command Code: `0x434D_4455` ("CMDU") |
| 2254 | + |
| 2255 | +*Table: `CM_AES_GCM_DECRYPT_UPDATE` input arguments* |
| 2256 | +| **Name** | **Type** | **Description** | |
| 2257 | +| --------------- | ------------------- | ---------------- | |
| 2258 | +| chksum | u32 || |
| 2259 | +| context | AES_GCM_CONTEXT || |
| 2260 | +| ciphertext size | u32 | MUST be non-zero | |
| 2261 | +| ciphertext | u8[ciphertext size] | Data to decrypt | |
| 2262 | + |
| 2263 | + |
| 2264 | +*Table: `CM_AES_GCM_DECRYPT_UPDATE` output arguments* |
| 2265 | +| **Name** | **Type** | **Description** | |
| 2266 | +| -------------- | ------------------ | ------------------------- | |
| 2267 | +| chksum | u32 || |
| 2268 | +| fips_status | u32 | FIPS approved or an error | |
| 2269 | +| context | AES_GCM_CONTEXT || |
| 2270 | +| plaintext size | u32 | MAY be 0 | |
| 2271 | +| plaintext | u8[plaintext size] || |
| 2272 | + |
| 2273 | + |
| 2274 | +### CM_AES_GCM_DECRYPT_FINAL |
| 2275 | + |
| 2276 | +This finalizes the computation of the AES GCM decryption and produces the final ciphertext. |
| 2277 | + |
| 2278 | +The context MUST be passed in from `CM_AES_GCM_DECRYPT_INIT` or `CM_AES_GCM_DECRYPT_UPDATE`. |
| 2279 | + |
| 2280 | +Tags between 0 and 16 bytes are supported but must be passed (on the right) with zeroes to 16 bytes. |
| 2281 | + |
| 2282 | +The caller MUST verify that the tag verified field is set to 1 before using the result. |
| 2283 | + |
| 2284 | +Command Code: `0x434D_4446` ("CMDF") |
| 2285 | + |
| 2286 | +*Table: `CM_AES_GCM_DECRYPT_FINAL` input arguments* |
| 2287 | +| **Name** | **Type** | **Description** | |
| 2288 | +| --------------- | ------------------- | --------------------------------- | |
| 2289 | +| chksum | u32 || |
| 2290 | +| context | AES_GCM_CONTEXT || |
| 2291 | +| tag size | u32 | Can be 8, 9, ..., 16 | |
| 2292 | +| tag | u8[16] | Right-padded with zeroes | |
| 2293 | +| ciphertext size | u32 | MAY be 0 | |
| 2294 | +| ciphertext | u8[ciphertext size] | Data to decrypt | |
| 2295 | + |
| 2296 | + |
| 2297 | +*Table: `CM_AES_GCM_DECRYPT_FINAL` output arguments* |
| 2298 | +| **Name** | **Type** | **Description** | |
| 2299 | +| -------------- | ------------------ | ------------------------------------ | |
| 2300 | +| chksum | u32 || |
| 2301 | +| fips_status | u32 | FIPS approved or an error | |
| 2302 | +| tag verified | u32 | 1 if tags matched, 0 if they did not | |
| 2303 | +| plaintext size | u32 | MAY be 0 | |
| 2304 | +| plaintext | u8[plaintext size] || |
| 2305 | + |
| 2306 | + |
| 2307 | +### CM_ECDH_GENERATE |
| 2308 | + |
| 2309 | +This computes the first half of an Elliptic Curve Diffie-Hellman exchange to compute an ephemeral shared key pair with another party. |
| 2310 | + |
| 2311 | +Currently only supports the NIST P-384 curve. |
| 2312 | + |
| 2313 | +The returned context must be passed to the `CM_ECDH_FINISH` command. The context contains the (encrypted) secret coefficient. |
| 2314 | + |
| 2315 | +The returned exchange data format is the concatenation of the x- and y-coordinates of the public point encoded as big-endian integers, padded to 48 bytes each. |
| 2316 | + |
| 2317 | +Command Code: `0x434D_4547` ("CMEG") |
| 2318 | + |
| 2319 | +*Table: `CM_ECDH_GENERATE` input arguments* |
| 2320 | +| **Name** | **Type** | **Description** | |
| 2321 | +| ----------- | -------- | -------------------- | |
| 2322 | +| chksum | u32 || |
| 2323 | + |
| 2324 | + |
| 2325 | +*Table: `CM_ECDH_GENERATE` output arguments* |
| 2326 | +| **Name** | **Type** | **Description** | |
| 2327 | +| ------------- | -------- | ------------------------------------- | |
| 2328 | +| chksum | u32 || |
| 2329 | +| fips_status | u32 | FIPS approved or an error | |
| 2330 | +| context | u8[76] | Used as the input to `CM_ECDH_FINISH` | |
| 2331 | +| exchange data | u8[96] | i.e., the public point | |
| 2332 | + |
| 2333 | + |
| 2334 | +*Table: `CM_ECDH_GENERATE` / `CM_ECDH_FINISH` internal context* |
| 2335 | +| **Name** | **Type** | **Description** | |
| 2336 | +| ------------------ | -------- | --------------- | |
| 2337 | +| Secret coefficient | u8[48] || |
| 2338 | + |
| 2339 | + |
| 2340 | +The encrypted context size (76 bytes) is the size of the internal context (48 bytes) plus as 12-byte IV and a 16-byte authentication tag. |
| 2341 | + |
| 2342 | +### CM_ECDH_FINISH |
| 2343 | + |
| 2344 | +This computes the second half of an Elliptic Curve Diffie-Hellman exchange. |
| 2345 | + |
| 2346 | +Currently only supports the NIST P-384 curve. |
| 2347 | + |
| 2348 | +The context must be passed from the `CM_ECDH_GENERATE` command. |
| 2349 | + |
| 2350 | +The incoming exchange data MUST be the concatenation of the x- and y- coordinates of the other side's public point, encoded as big-endian integers, padded to 48 bytes each. |
| 2351 | + |
| 2352 | +The produced shared secret is 384 bits. |
| 2353 | + |
| 2354 | +Command Code: `0x434D_4546` ("CMEF") |
| 2355 | + |
| 2356 | +*Table: `CM_ECDH_FINISH` input arguments* |
| 2357 | +| **Name** | **Type** | **Description** | |
| 2358 | +| ---------------------- | -------- | -------------------------------------------------------- | |
| 2359 | +| chksum ||| |
| 2360 | +| context | u8[76] | This MUST come from the output of the `CM_ECDH_GENERATE` | |
| 2361 | +| key usage | u32 | usage tag of the kind of key that will be output | |
| 2362 | +| incoming exchange data | u8[96] | the other side's public point | |
| 2363 | + |
| 2364 | + |
| 2365 | +The context used as an input is the same as the output context from `CM_ECDH_GENERATE` above. |
| 2366 | + |
| 2367 | +*Table: `CM_ECDH_FINISH` output arguments* |
| 2368 | +| **Name** | **Type** | **Description** | |
| 2369 | +| ----------- | -------- | ------------------------------- | |
| 2370 | +| chksum | u32 || |
| 2371 | +| fips_status | u32 | FIPS approved or an error | |
| 2372 | +| output CMK | CMK | Output CMK of the shared secret | |
| 2373 | + |
| 2374 | + |
| 2375 | + |
| 2376 | +### CM_RANDOM_STIR |
| 2377 | + |
| 2378 | +This allows additional entropy to be added to the underlying deterministic random bit generator, if the hardware is using a CSRNG DRBG. |
| 2379 | + |
| 2380 | +Command Code: `0x434D_5253` ("CMRS") |
| 2381 | + |
| 2382 | +*Table: `CM_RANDOM_STIR` input arguments* |
| 2383 | + |
| 2384 | +| **Name** | **Type** | **Description** | |
| 2385 | +| ---------- | -------------- | --------------- | |
| 2386 | +| chksum | u32 || |
| 2387 | +| input size | u32 || |
| 2388 | +| input | u8[input size] || |
| 2389 | + |
| 2390 | + |
| 2391 | +*Table: `CM_RANDOM_STIR` output arguments* |
| 2392 | +| **Name** | **Type** | **Description** | |
| 2393 | +| ----------- | -------- | ------------------------- | |
| 2394 | +| chksum | u32 || |
| 2395 | +| fips_status | u32 | FIPS approved or an error | |
| 2396 | + |
| 2397 | + |
| 2398 | +### CM_RANDOM_GENERATE |
| 2399 | + |
| 2400 | +This generates random bytes that are returned from the internal RNG. |
| 2401 | + |
| 2402 | +Command Code: `0x434D_5247` ("CMRG") |
| 2403 | + |
| 2404 | +*Table: `CM_RANDOM_GENERATE` input arguments* |
| 2405 | + |
| 2406 | +| **Name** | **Type** | **Description** | |
| 2407 | +| ------------------- | -------- | --------------- | |
| 2408 | +| chksum | u32 || |
| 2409 | +| data size to return | u32 || |
| 2410 | + |
| 2411 | + |
| 2412 | + |
| 2413 | +*Table: `CM_RANDOM_GENERATE` output arguments* |
| 2414 | +| **Name** | **Type** | **Description** | |
| 2415 | +| ----------- | --------------- | ------------------------- | |
| 2416 | +| chksum | u32 || |
| 2417 | +| fips_status | u32 | FIPS approved or an error | |
| 2418 | +| output size | u32 | size of output | |
| 2419 | +| output | u8[output size] || |
| 2420 | + |
| 2421 | + |
| 2422 | +### CM\_DERIVE\_STABLE\_KEY |
| 2423 | + |
| 2424 | +Derives an HMAC key that has a stable value across resets from either |
| 2425 | +IDevId or LDevId. |
| 2426 | + |
| 2427 | +The (interior) value of the returned CMK will be the stable across resets as it is derived indirectly from the IDevId or LDevId CDIs. |
| 2428 | +The actual encrypted bytes of the CMK will *not* be the same, and |
| 2429 | +the encrypted CMK itself cannot be used across resets. So, the key |
| 2430 | +will always need to be re-derived after every *cold* reset. |
| 2431 | + |
| 2432 | +If a key usage other than HMAC is desired, then the KDF or HKDF |
| 2433 | +mailbox functions can be used to derive a key from the returned CMK. |
| 2434 | + |
| 2435 | +Note that in Caliptra 2.0 in subsystem mode, derived stable keys, their derivatives, and commands using them will be marked with a FIPS status of invalid since the UDS and FE cannot be completely zeroized. |
| 2436 | + |
| 2437 | +The command derivation is summarized below: |
| 2438 | + |
| 2439 | +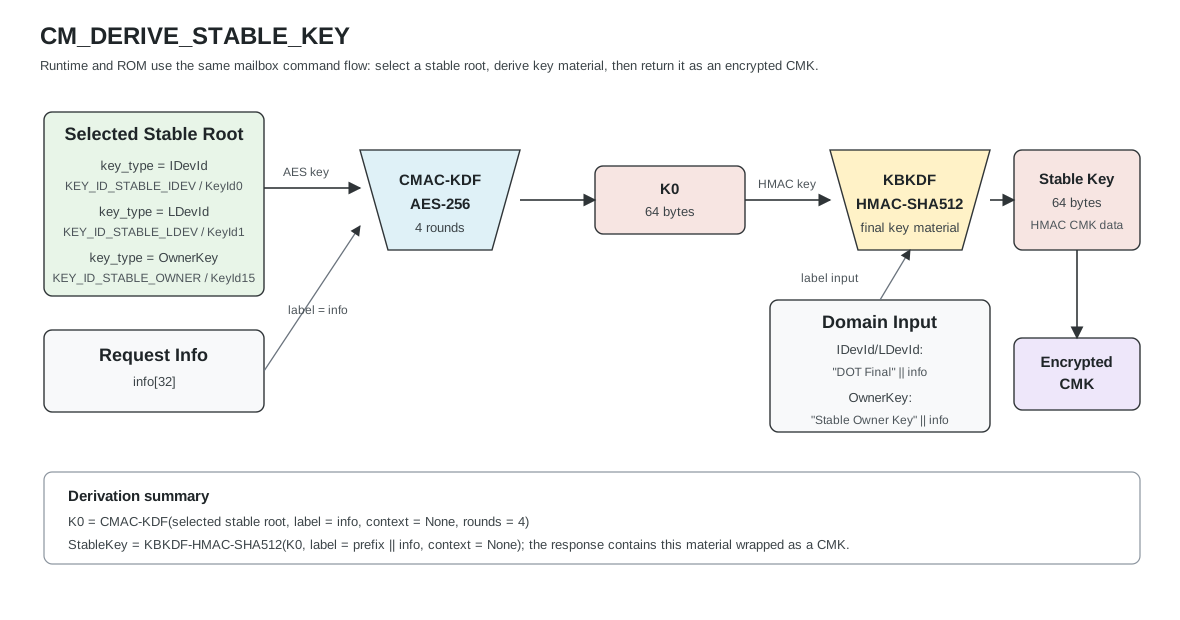 |
| 2440 | + |
| 2441 | +Command Code: `0x434D_4453` ("CMDS") |
| 2442 | + |
| 2443 | +*Table: `CM_DERIVE_STABLE_KEY` input arguments* |
| 1090 | 2444 | |
| 1091 | 2445 | | **Name** | **Type** | **Description** |
| 1092 | 2446 | | -------- | -------- | --------------- |
| 1093 | 2447 | | chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. | |
| 1094 | | - |
| 1095 | | - |
| 1096 | | -*Table: `GET_IDEVID_CSR` output arguments* |
| 2448 | +| key_type | u32 | Source key to derive the stable key from. **0x0000_0001:** IDevId <br> **0x0000_0002:** LDevId | |
| 2449 | +| info | u8[32] | Data to use in the key derivation. | |
| 2450 | + |
| 2451 | + |
| 2452 | +*Table: `CM_DERIVE_STABLE_KEY` output arguments* |
| 2453 | +| **Name** | **Type** | **Description** |
| 2454 | +| -------- | -------- | --------------- |
| 2455 | +| chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. | |
| 2456 | +| cmk | CMK | CMK that stores the stable key material | |
| 2457 | + |
| 2458 | + |
| 2459 | +### CM_IMPORT |
| 2460 | + |
| 2461 | +Imports the specified key and returns a CMK for it. |
| 2462 | + |
| 2463 | +Usage information is required so that the key can be verified and used appropriately. |
| 2464 | + |
| 2465 | +Note that it is the caller's responsibility to ensure that the source |
| 2466 | +key material meets FIPS requirements, such as zeroization. |
| 2467 | + |
| 2468 | +Command Code: `0x434D_494D` ("CMIM") |
| 2469 | + |
| 2470 | +*Table: `CM_IMPORT` input arguments* |
| 2471 | + |
| 2472 | +| **Name** | **Type** | **Description** | |
| 2473 | +| ---------- | -------------- | --------------------------------------- | |
| 2474 | +| chksum | u32 || |
| 2475 | +| key usage | u32 | Tag to specify how the data can be used | |
| 2476 | +| input size | u32 | This MUST agree with the key usage | |
| 2477 | +| input | u8[input size] || |
| 2478 | + |
| 2479 | + |
| 2480 | +*Table: `CM_IMPORT` output arguments* |
| 2481 | +| **Name** | **Type** | **Description** | |
| 2482 | +| ----------- | -------- | --------------------------- | |
| 2483 | +| chksum | u32 || |
| 2484 | +| fips_status | u32 | FIPS approved or an error | |
| 2485 | +| CMK | CMK | CMK containing imported key | |
| 2486 | + |
| 2487 | + |
| 2488 | +### CM_DELETE |
| 2489 | + |
| 2490 | +Deletes the object stored with the given mailbox ID. |
| 2491 | + |
| 2492 | +Command Code: `0x434D_444C` ("CMDL") |
| 2493 | + |
| 2494 | +*Table: `CM_DELETE` input arguments* |
| 2495 | + |
| 2496 | +| **Name** | **Type** | **Description** | |
| 2497 | +| -------- | -------- | --------------- | |
| 2498 | +| chksum | u32 || |
| 2499 | +| CMK | CMK | CMK to delete | |
| 2500 | + |
| 2501 | + |
| 2502 | +*Table: `CM_DELETE` output arguments* |
| 2503 | +| **Name** | **Type** | **Description** | |
| 2504 | +| ----------- | -------- | ------------------------- | |
| 2505 | +| chksum | u32 || |
| 2506 | +| fips_status | u32 | FIPS approved or an error | |
| 2507 | + |
| 2508 | + |
| 2509 | +### CM_CLEAR |
| 2510 | + |
| 2511 | +The entire contents of the CMK storage is wiped. All known keys will be invalidated. |
| 2512 | + |
| 2513 | +Command Code: `0x434D_434C` ("CMCL") |
| 2514 | + |
| 2515 | +`CM_CLEAR` takes no input arguments. |
| 2516 | + |
| 2517 | +*Table: `CM_CLEAR` output arguments* |
| 2518 | +| **Name** | **Type** | **Description** | |
| 2519 | +| ----------- | -------- | ------------------------- | |
| 2520 | +| chksum | u32 || |
| 2521 | +| fips_status | u32 | FIPS approved or an error | |
| 2522 | + |
| 2523 | + |
| 2524 | +### CM_STATUS |
| 2525 | + |
| 2526 | +Queries the status cryptographic mailbox system. |
| 2527 | + |
| 2528 | +The usage storage records the number of entries used and total for for usage tracking. |
| 2529 | +Usage tracking is only currently implemented for AES, so this is is effectively the number of AES keys used and total potential available AES keys. |
| 2530 | + |
| 2531 | +Command Code: `0x434D_5354` ("CMST") |
| 2532 | + |
| 2533 | +`CM_STATUS` takes no input arguments. |
| 2534 | + |
| 2535 | +*Table: `CM_STATUS` output arguments* |
| 2536 | +| **Name** | **Type** | **Description** | |
| 2537 | +| ------------------- | -------- | ------------------------------------ | |
| 2538 | +| chksum | u32 || |
| 2539 | +| fips_status | u32 | FIPS approved or an error | |
| 2540 | +| used usage storage | u32 | CMK usage storage (in entries) | |
| 2541 | +| total usage storage | u32 | Total CMK usage storage (in entries) | |
| 2542 | + |
| 2543 | + |
| 2544 | + |
| 2545 | +### GET\_IDEV\_ECC384\_CSR |
| 2546 | + |
| 2547 | +Command Code: `0x4944_4352` ("IDCR") |
| 2548 | + |
| 2549 | +*Table: `GET_IDEV_ECC384_CSR` input arguments* |
| 2550 | + |
| 2551 | +| **Name** | **Type** | **Description** |
| 2552 | +| -------- | -------- | --------------- |
| 2553 | +| chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. | |
| 2554 | + |
| 2555 | + |
| 2556 | +*Table: `GET_IDEV_ECC384_CSR` output arguments* |
| 1097 | 2557 | | **Name** | **Type** | **Description** |
| 1098 | 2558 | | -------- | -------- | --------------- |
| 1099 | 2559 | | chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. | |
| 1100 | 2560 | | data\_size | u32 | Length in bytes of the valid data in the data field. | |
| 1101 | | -| data | u8[...] | DER-encoded IDevID certificate signing request. | |
| 1102 | | - |
| 1103 | | - |
| 1104 | | -The `mfg_flag_gen_idev_id_csr` manufacturing flag **MUST** have been set to generate a CSR. |
| 1105 | | - |
| 1106 | | -When called from ROM, if the CSR was not previously provisioned this command will return `FW_PROC_MAILBOX_UNPROVISIONED_CSR(0x0102000A)`. |
| 1107 | | - |
| 1108 | | -When called from runtime, if the CSR was not previously provisioned this command will return `RUNTIME_GET_IDEV_ID_UNPROVISIONED(0x000E0051)`. If the ROM did not support CSR generation, this command will return `RUNTIME_GET_IDEV_ID_UNSUPPORTED_ROM(0x000E0052)`. |
| 1109 | | - |
| 1110 | | - |
| 1111 | | - |
| 1112 | | -When the `mfg_flag_gen_idev_id_csr` flag has been set, the SoC **MUST** wait for the `flow_status_set_idevid_csr_ready` bit to be set by Caliptra. Once set, the SoC **MUST** clear the `mfg_flag_gen_idev_id_csr` flag for Caliptra to progress. |
| 1113 | | - |
| 1114 | | -### GET\_FMC\_ALIAS\_CSR |
| 1115 | | - |
| 1116 | | -Command Code: `0x464D_4352` ("FMCR") |
| 1117 | | - |
| 1118 | | -Privilege Level: PL0 or PL1 |
| 1119 | | - |
| 1120 | | -*Table: `GET_FMC_ALIAS_CSR` input arguments* |
| 2561 | +| data | u8[...] | DER-encoded ECC384 IDevID certificate signing request. | |
| 2562 | + |
| 2563 | + |
| 2564 | +### GET\_IDEV\_MLDSA87\_CSR |
| 2565 | + |
| 2566 | +Command Code: `0x4944_4d52` ("IDMR") |
| 2567 | + |
| 2568 | +*Table: `GET_IDEV_MLDSA87_CSR` input arguments* |
| 1121 | 2569 | |
| 1122 | 2570 | | **Name** | **Type** | **Description** |
| 1123 | 2571 | | -------- | -------- | --------------- |
| 1124 | 2572 | | chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. | |
| 1125 | 2573 | |
| 1126 | 2574 | |
| 1127 | | -*Table: `GET_FMC_ALIAS_CSR` output arguments* |
| 2575 | +*Table: `GET_IDEV_MLDSA87_CSR` output arguments* |
| 1128 | 2576 | | **Name** | **Type** | **Description** |
| 1129 | 2577 | | -------- | -------- | --------------- |
| 1130 | 2578 | | chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. | |
| 1131 | 2579 | | data\_size | u32 | Length in bytes of the valid data in the data field. | |
| 1132 | | -| data | u8[...] | DER-encoded FMC ALIAS certificate signing request. | |
| 1133 | | - |
| 1134 | | - |
| 1135 | | -The FMC Alias CSR is generated unconditionally on every cold boot. |
| 2580 | +| data | u8[...] | DER-encoded MLDSA87 IDevID certificate signing request. | |
| 2581 | + |
| 2582 | + |
| 2583 | +The `mfg_flag_gen_idev_id_csr` manufacturing flag **MUST** have been set to generate a CSR. |
| 2584 | + |
| 2585 | +When called from ROM, if the CSR was not previously provisioned this command will return `FW_PROC_MAILBOX_UNPROVISIONED_CSR(0x0102000A)`. |
| 2586 | + |
| 2587 | +When called from runtime, if the CSR was not previously provisioned this command will return `RUNTIME_GET_IDEV_ID_UNPROVISIONED(0x000E0051)`. If the ROM did not support CSR generation, this command will return `RUNTIME_GET_IDEV_ID_UNSUPPORTED_ROM(0x000E0052)`. |
| 2588 | + |
| 2589 | +When the `mfg_flag_gen_idev_id_csr` flag has been set, the SoC **MUST** wait for the `flow_status_set_idevid_csr_ready` bit to be set by Caliptra. Once set, the SoC **MUST** clear the `mfg_flag_gen_idev_id_csr` flag for Caliptra to progress. |
| 2590 | + |
| 2591 | +### GET\_FMC\_ALIAS\_ECC384\_CSR |
| 2592 | + |
| 2593 | +Command Code: `0x464D_4352` ("FMCR") |
| 2594 | + |
| 2595 | +*Table: `GET_FMC_ALIAS_ECC384_CSR` input arguments* |
| 2596 | + |
| 2597 | +| **Name** | **Type** | **Description** |
| 2598 | +| -------- | -------- | --------------- |
| 2599 | +| chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. | |
| 2600 | + |
| 2601 | + |
| 2602 | +*Table: `GET_FMC_ALIAS_ECC384_CSR` output arguments* |
| 2603 | +| **Name** | **Type** | **Description** |
| 2604 | +| -------- | -------- | --------------- |
| 2605 | +| chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. | |
| 2606 | +| data\_size | u32 | Length in bytes of the valid data in the data field. | |
| 2607 | +| data | u8[...] | DER-encoded ECC384 FMC Alias certificate signing request. | |
| 2608 | + |
| 2609 | + |
| 2610 | +### GET\_FMC\_ALIAS\_MLDSA87\_CSR |
| 2611 | + |
| 2612 | +Command Code: `0x464d_4452` ("FMDR") |
| 2613 | + |
| 2614 | +*Table: `GET_FMC_ALIAS_MLDSA87_CSR` input arguments* |
| 2615 | + |
| 2616 | +| **Name** | **Type** | **Description** |
| 2617 | +| -------- | -------- | --------------- |
| 2618 | +| chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. | |
| 2619 | + |
| 2620 | + |
| 2621 | +*Table: `GET_FMC_ALIAS_MLDSA87_CSR` output arguments* |
| 2622 | +| **Name** | **Type** | **Description** |
| 2623 | +| -------- | -------- | --------------- |
| 2624 | +| chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. | |
| 2625 | +| data\_size | u32 | Length in bytes of the valid data in the data field. | |
| 2626 | +| data | u8[...] | DER-encoded MLDSA87 FMC Alias certificate signing request. | |
| 2627 | + |
| 2628 | + |
| 2629 | +### GET\_ATTESTED\_ECC384\_CSR |
| 2630 | + |
| 2631 | +Generates an attested ECC384 certificate signing request (CSR) in Entity Attestation Token (EAT) format as per the [OCP Device Identity Provisioning](https://opencomputeproject.github.io/Security/device-identity-provisioning/HEAD/) specification, signed by the `RT Alias` key for the requested Device Identity Key. |
| 2632 | + |
| 2633 | +Command Code: `0x4145_4352` ("AECR") |
| 2634 | + |
| 2635 | +*Table: `GET_ATTESTED_ECC384_CSR` input arguments* |
| 2636 | + |
| 2637 | +| **Name** | **Type** | **Description** |
| 2638 | +| -------- | -------- | --------------- |
| 2639 | +| chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. | |
| 2640 | +| key_id | u32 | Key ID for which CSR is requested.<br> **0x0000_0001:** LDevId <br> **0x0000_0002:** FMC Alias <br> **0x0000_0003:** RT Alias | |
| 2641 | +| nonce | u8[32] | Nonce to be included in the CSR EAT. | |
| 2642 | + |
| 2643 | + |
| 2644 | +*Table: `GET_ATTESTED_ECC384_CSR` output arguments* |
| 2645 | + |
| 2646 | +| **Name** | **Type** | **Description** |
| 2647 | +| -------- | -------- | --------------- |
| 2648 | +| chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. | |
| 2649 | +| data\_size | u32 | Length in bytes of the valid data in the data field. | |
| 2650 | +| data | u8[...] | DER-encoded ECC384 attested certificate signing request. | |
| 2651 | + |
| 2652 | + |
| 2653 | +### GET\_ATTESTED\_MLDSA87\_CSR |
| 2654 | + |
| 2655 | +Generates an attested MLDSA87 certificate signing request (CSR) in Entity Attestation Token (EAT) format as per the [OCP Device Identity Provisioning](https://opencomputeproject.github.io/Security/device-identity-provisioning/HEAD/) specification, signed by the `RT Alias` key for the requested Device Identity Key. |
| 2656 | + |
| 2657 | +Command Code: `0x414D_4352` ("AMCR") |
| 2658 | + |
| 2659 | +*Table: `GET_ATTESTED_MLDSA87_CSR` input arguments* |
| 2660 | + |
| 2661 | +| **Name** | **Type** | **Description** |
| 2662 | +| -------- | -------- | --------------- |
| 2663 | +| chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. | |
| 2664 | +| key_id | u32 | Key ID for which CSR is requested.<br> **0x0000_0001:** LDevId <br> **0x0000_0002:** FMC Alias <br> **0x0000_0003:** RT Alias | |
| 2665 | +| nonce | u8[32] | Nonce to be included in the CSR EAT. | |
| 2666 | + |
| 2667 | + |
| 2668 | +*Table: `GET_ATTESTED_MLDSA87_CSR` output arguments* |
| 2669 | + |
| 2670 | +| **Name** | **Type** | **Description** |
| 2671 | +| -------- | -------- | --------------- |
| 2672 | +| chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. | |
| 2673 | +| data\_size | u32 | Length in bytes of the valid data in the data field. | |
| 2674 | +| data | u8[...] | DER-encoded MLDSA87 attested certificate signing request. | |
| 2675 | + |
| 1136 | 2676 | |
| 1137 | 2677 | ### SIGN\_WITH\_EXPORTED\_ECDSA |
| 1138 | 2678 | |
| 1139 | 2679 | Command Code: `0x5357_4545` ("SWEE") |
| 1140 | 2680 | |
| 1141 | | -Privilege Level: PL0 |
| 2681 | +**Note**: This command is only available in the locality of the PL0 PAUSER. |
| 1142 | 2682 | |
| 1143 | 2683 | *Table: `SIGN_WITH_EXPORTED_ECDSA` input arguments* |
| 1144 | 2684 | |
| @@ -1158,13 +2698,13 @@ |
| 1158 | 2698 | | signature_s | u8[48] | The S BigNum of an ECDSA signature. | |
| 1159 | 2699 | |
| 1160 | 2700 | |
| 1161 | | -The `exported_cdi_handle` can be created by calling `DeriveContext` with the `export-cdi` and `create-certificate` flags. |
| 2701 | +The `exported_cdi` can be created by calling `DeriveContext` with the `export-cdi` and `create-certificate` flags. |
| 1162 | 2702 | |
| 1163 | 2703 | ### REVOKE\_EXPORTED\_CDI\_HANDLE |
| 1164 | 2704 | |
| 1165 | 2705 | Command Code: `5256_4348` ("RVCH") |
| 1166 | 2706 | |
| 1167 | | -Privilege Level: PL0 |
| 2707 | +**Note**: This command is only available in the locality of the PL0 PAUSER. |
| 1168 | 2708 | |
| 1169 | 2709 | *Table: `REVOKE_EXPORTED_CDI_HANDLE` input arguments* |
| 1170 | 2710 | |
| @@ -1174,16 +2714,16 @@ |
| 1174 | 2714 | | exported_cdi_handle | u8[32] | The Exported CDI handle returned by the DPE `DeriveContext` command. Little endian. | |
| 1175 | 2715 | |
| 1176 | 2716 | |
| 1177 | | -The `exported_cdi_handle` can be created by calling `DeriveContext` with the `export-cdi` and `create-certificate` flags. |
| 2717 | +The `exported_cdi` can be created by calling `DeriveContext` with the `export-cdi` and `create-certificate` flags. |
| 1178 | 2718 | |
| 1179 | 2719 | The `exported_cdi_handle` is no longer usable after calling `REVOKE_EXPORTED_CDI_HANDLE` with it. After the `exported_cdi_handle` |
| 1180 | | -has been revoked, a new exported CDI handle can be created by calling `DeriveContext` with the `export-cdi` and `create-certificate` flags. |
| 2720 | +has been revoked, a new exported CDI can be created by calling `DeriveContext` with the `export-cdi` and `create-certificate` flags. |
| 1181 | 2721 | |
| 1182 | 2722 | ### REALLOCATE\_DPE\_CONTEXT\_LIMITS |
| 1183 | 2723 | |
| 1184 | 2724 | Command Code: '5243_5458` ("RCTX") |
| 1185 | 2725 | |
| 1186 | | -Privilege Level: PL0 |
| 2726 | +**Note**: This command is only available in the locality of the PL0 PAUSER. |
| 1187 | 2727 | |
| 1188 | 2728 | *Table: `REALLOCATE_DPE_CONTEXT_LIMITS` input arguments* |
| 1189 | 2729 | |
| @@ -1206,215 +2746,9 @@ |
| 1206 | 2746 | |
| 1207 | 2747 | **Note**: 2 PL0 contexts are used by Caliptra itself during initialization. |
| 1208 | 2748 | |
| 1209 | | -## PQC (ML-DSA-87) commands |
| 1210 | | - |
| 1211 | | -The following commands implement the `PQ.DevID` post-quantum identity retrofit described in [Software-based PQC features](https://github.com/chipsalliance/Caliptra/blob/main/doc/caliptra_1x/Caliptra.md#software-based-pqc-features-caliptra-13). All ML-DSA-87 cryptography is implemented in software; there is no hardware PQC accelerator on Caliptra 1.x silicon. |
| 1212 | | -The availability of these commands is advertised to the SoC via the `RT_MLDSA_ATTESTATION` bit in the [`CAPABILITIES`](#capabilities) output. |
| 1213 | | - |
| 1214 | | -### SET\_PQ\_SEED |
| 1215 | | - |
| 1216 | | -Delivers `PQ.DevID.Seed` from the SoC to Caliptra. Caliptra derives `PQ.DevID.CDI` from the seed via an HMAC-based KDF, derives the ML-DSA-87 `PQ.DevID` keypair, and caches the public key digest in persistent data. |
| 1217 | | - |
| 1218 | | -Command Code: `0x5051_5344` ("PQSD") |
| 1219 | | - |
| 1220 | | -Privilege Level: PL0 |
| 1221 | | - |
| 1222 | | -*Table: `SET_PQ_SEED` input arguments* |
| 1223 | | - |
| 1224 | | -| **Name** | **Type** | **Description** |
| 1225 | | -| -------- | --------- | --------------- |
| 1226 | | -| chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. |
| 1227 | | -| seed | u8[48] | `PQ.DevID.Seed`. Per-device unique symmetric seed, provided by the SoC. |
| 1228 | | - |
| 1229 | | -*Table: `SET_PQ_SEED` output arguments* |
| 1230 | | - |
| 1231 | | -| **Name** | **Type** | **Description** |
| 1232 | | -| -------- | -------- | --------------- |
| 1233 | | -| chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. |
| 1234 | | -| fips\_status | u32 | Indicates if the command is FIPS approved or an error. |
| 1235 | | - |
| 1236 | | -Deriving `PQ.DevID.CDI` and the ML-DSA-87 key material can exceed the default mailbox command watchdog budget; Runtime Firmware extends the watchdog for this command. |
| 1237 | | -The production `PQ.DevID.Seed` must never be delivered while Caliptra is `DebugUnlocked`. |
| 1238 | | -Integrators may still call `SET_PQ_SEED` with a non-production seed while `DebugUnlocked` for local bring-up and debug. |
| 1239 | | - |
| 1240 | | -### GET\_PQ\_CSR |
| 1241 | | - |
| 1242 | | -Returns a CSR for the `PQ.DevID` ML-DSA-87 public key, for collection during manufacturing/provisioning, mirroring [`GET_IDEVID_CSR`](#get_idevid_csr). |
| 1243 | | - |
| 1244 | | -Command Code: `0x5051_4353` ("PQCS") |
| 1245 | | - |
| 1246 | | -Privilege Level: PL0 or PL1 |
| 1247 | | - |
| 1248 | | -*Table: `GET_PQ_CSR` input arguments* |
| 1249 | | - |
| 1250 | | -| **Name** | **Type** | **Description** |
| 1251 | | -| -------- | -------- | --------------- |
| 1252 | | -| chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. |
| 1253 | | - |
| 1254 | | -*Table: `GET_PQ_CSR` output arguments* |
| 1255 | | - |
| 1256 | | -| **Name** | **Type** | **Description** |
| 1257 | | -| -------- | --------- | --------------- |
| 1258 | | -| chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. |
| 1259 | | -| fips\_status | u32 | Indicates if the command is FIPS approved or an error. |
| 1260 | | -| data\_size | u32 | Length in bytes of the valid data in the data field, with a maximum of 12800. |
| 1261 | | -| data | u8[12800] | DER-encoded ML-DSA-87 `PQ.DevID` certificate signing request. |
| 1262 | | - |
| 1263 | | -### GET\_PQ\_INFO |
| 1264 | | - |
| 1265 | | -Returns the raw ML-DSA-87 `PQ.DevID` public key. |
| 1266 | | - |
| 1267 | | -Command Code: `0x5051_494E` ("PQIN") |
| 1268 | | - |
| 1269 | | -Privilege Level: PL0 or PL1 |
| 1270 | | - |
| 1271 | | -*Table: `GET_PQ_INFO` input arguments* |
| 1272 | | - |
| 1273 | | -| **Name** | **Type** | **Description** |
| 1274 | | -| -------- | -------- | --------------- |
| 1275 | | -| chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. |
| 1276 | | - |
| 1277 | | -*Table: `GET_PQ_INFO` output arguments* |
| 1278 | | - |
| 1279 | | -| **Name** | **Type** | **Description** |
| 1280 | | -| -------- | --------- | --------------- |
| 1281 | | -| chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. |
| 1282 | | -| fips\_status | u32 | Indicates if the command is FIPS approved or an error. |
| 1283 | | -| pq\_pub\_key | u8[2592] | Encoded ML-DSA-87 `PQ.DevID` public key (FIPS 204). |
| 1284 | | - |
| 1285 | | -### POPULATE\_PQ\_CERT |
| 1286 | | - |
| 1287 | | -Allows the SoC to provide a DER-encoded `PQ.DevID` certificate on every boot, once it has been issued by the vendor/owner PQC provisioning CA. Mirrors [`POPULATE_IDEV_CERT`](#populate_idev_cert). |
| 1288 | | - |
| 1289 | | -Command Code: `0x5050_5143` ("PPQC") |
| 1290 | | - |
| 1291 | | -Privilege Level: PL0 |
| 1292 | | - |
| 1293 | | -*Table: `POPULATE_PQ_CERT` input arguments* |
| 1294 | | - |
| 1295 | | -| **Name** | **Type** | **Description** |
| 1296 | | -| -------- | -------- | --------------- |
| 1297 | | -| chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. |
| 1298 | | -| cert\_size | u32 | Size of the DER-encoded `PQ.DevID` certificate, with a maximum of 8192. |
| 1299 | | -| cert | u8[8192] | DER-encoded `PQ.DevID` certificate. |
| 1300 | | - |
| 1301 | | -*Table: `POPULATE_PQ_CERT` output arguments* |
| 1302 | | - |
| 1303 | | -| **Name** | **Type** | **Description** |
| 1304 | | -| -------- | -------- | --------------- |
| 1305 | | -| chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. |
| 1306 | | -| fips\_status | u32 | Indicates if the command is FIPS approved or an error. |
| 1307 | | - |
| 1308 | | -### GET\_PQ\_CERT |
| 1309 | | - |
| 1310 | | -Given a caller-supplied TBS and ML-DSA-87 signature over that TBS, DER-assembles and returns the resulting `PQ.DevID` certificate. Stateless: it does not read the certificate buffer populated by `POPULATE_PQ_CERT`. Mirrors [`GET_IDEV_CERT`](#get_idev_cert). |
| 1311 | | - |
| 1312 | | -Command Code: `0x4750_5143` ("GPQC") |
| 1313 | | - |
| 1314 | | -Privilege Level: PL0 or PL1 |
| 1315 | | - |
| 1316 | | -*Table: `GET_PQ_CERT` input arguments* |
| 1317 | | - |
| 1318 | | -| **Name** | **Type** | **Description** |
| 1319 | | -| -------- | -------- | --------------- |
| 1320 | | -| chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. |
| 1321 | | -| tbs\_size | u32 | Size of the TBS, with a maximum of 3543. |
| 1322 | | -| signature | u8[4627] | ML-DSA-87 signature (FIPS 204) over the TBS, supplied by the caller. Not verified or computed by Caliptra; used as-is to assemble the certificate's `signatureValue`. |
| 1323 | | -| tbs | u8[3543] | TBS. Only bytes up to tbs_size are used. |
| 1324 | | - |
| 1325 | | -*Table: `GET_PQ_CERT` output arguments* |
| 1326 | | - |
| 1327 | | -| **Name** | **Type** | **Description** |
| 1328 | | -| -------- | -------- | --------------- |
| 1329 | | -| chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. |
| 1330 | | -| fips\_status | u32 | Indicates if the command is FIPS approved or an error. |
| 1331 | | -| cert\_size | u32 | Length in bytes of the valid data in the cert field, with a maximum of 8192. |
| 1332 | | -| cert | u8[8192] | DER-encoded `PQ.DevID` certificate. |
| 1333 | | - |
| 1334 | | -### INVOKE\_DPE\_MLDSA87 |
| 1335 | | - |
| 1336 | | -Invokes a DPE command using the ML-DSA-87 crypto backend, mirroring [`INVOKE_DPE_COMMAND`](#invoke_dpe_command) but rooted in the ML-DSA-87 DPE profile. |
| 1337 | | - |
| 1338 | | -Command Code: `0x4D4C_4450` ("MLDP") |
| 1339 | | - |
| 1340 | | -Privilege Level: PL0 or PL1; a subset of DPE commands requires PL0 (see [Mailbox command privilege levels](#mailbox-command-privilege-levels)) |
| 1341 | | - |
| 1342 | | -*Table: `INVOKE_DPE_MLDSA87` input arguments* |
| 1343 | | - |
| 1344 | | -| **Name** | **Type** | **Description** |
| 1345 | | -| -------- | -------- | --------------- |
| 1346 | | -| chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. |
| 1347 | | -| data\_size | u32 | Length in bytes of the valid data in the data field. |
| 1348 | | -| data | u8[512] | Encoded DPE command. Only bytes up to data_size are used. |
| 1349 | | - |
| 1350 | | -*Table: `INVOKE_DPE_MLDSA87` output arguments* |
| 1351 | | - |
| 1352 | | -| **Name** | **Type** | **Description** |
| 1353 | | -| -------- | ----------- | --------------- |
| 1354 | | -| chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. |
| 1355 | | -| fips\_status | u32 | Indicates if the command is FIPS approved or an error. |
| 1356 | | -| data\_size | u32 | Length in bytes of the valid data in the data field. |
| 1357 | | -| data | u8[25168] | Encoded DPE response. Only bytes up to data_size are used. |
| 1358 | | - |
| 1359 | | -### CERTIFY\_KEY\_EXTENDED\_MLDSA87 |
| 1360 | | - |
| 1361 | | -The ML-DSA-87 counterpart to [`CERTIFY_KEY_EXTENDED`](#certify_key_extended): produces a DPE leaf certificate or CSR, signed with ML-DSA-87, containing custom extensions provided by the SoC. |
| 1362 | | - |
| 1363 | | -Command Code: `0x434B_454D` ("CKEM") |
| 1364 | | - |
| 1365 | | -Privilege Level: PL0 |
| 1366 | | - |
| 1367 | | -*Table: `CERTIFY_KEY_EXTENDED_MLDSA87` input arguments* |
| 1368 | | - |
| 1369 | | -| **Name** | **Type** | **Description** |
| 1370 | | -| -------- | -------- | --------------- |
| 1371 | | -| chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. |
| 1372 | | -| flags | u32 | Flags determining which custom extensions to include in the certificate. See [`CERTIFY_KEY_EXTENDED` input flags](#certify_key_extended). |
| 1373 | | -| certify\_key\_req | u8[72] | Certify Key Request. |
| 1374 | | - |
| 1375 | | -*Table: `CERTIFY_KEY_EXTENDED_MLDSA87` output arguments* |
| 1376 | | - |
| 1377 | | -| **Name** | **Type** | **Description** |
| 1378 | | -| -------- | -------- | --------------- |
| 1379 | | -| chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. |
| 1380 | | -| fips\_status | u32 | Indicates if the command is FIPS approved or an error. |
| 1381 | | -| size | u32 | Length in bytes of the valid data in the certify_key_resp field. |
| 1382 | | -| certify\_key\_resp | u8[25152] | Certify Key Response. |
| 1383 | | - |
| 1384 | | -This command can take tens of millions of CPU cycles due to the software ML-DSA-87 implementation; see [Performance considerations](https://github.com/chipsalliance/Caliptra/blob/main/doc/caliptra_1x/Caliptra.md#performance-considerations). |
| 1385 | | - |
| 1386 | | -### SIGN\_WITH\_EXPORTED\_MLDSA |
| 1387 | | - |
| 1388 | | -The ML-DSA-87 counterpart to [`SIGN_WITH_EXPORTED_ECDSA`](#sign_with_exported_ecdsa): signs with an ML-DSA-87 key pair derived from a previously exported DPE CDI handle. |
| 1389 | | - |
| 1390 | | -Command Code: `0x5357_4D4C` ("SWML") |
| 1391 | | - |
| 1392 | | -Privilege Level: PL0 |
| 1393 | | - |
| 1394 | | -*Table: `SIGN_WITH_EXPORTED_MLDSA` input arguments* |
| 1395 | | - |
| 1396 | | -| **Name** | **Type** | **Description** |
| 1397 | | -| -------- | -------- | --------------- |
| 1398 | | -| chksum | u32 | Checksum over other input arguments, computed by the caller. Little endian. |
| 1399 | | -| exported\_cdi\_handle | u8[32] | The Exported CDI handle returned by the DPE `DeriveContext` command. |
| 1400 | | -| sign\_mode | u32 | `0` (`SIGN_MODE_DATA`): `message[..message_size]` is the raw message to sign, and Caliptra computes `mu` internally. `1` (`SIGN_MODE_EXTERNAL_MU`): `message[..MU_SIZE]` is a caller-supplied external `mu`; `message_size` must equal `MU_SIZE`. |
| 1401 | | -| message\_size | u32 | Length in bytes of the valid data in the message field. |
| 1402 | | -| message | u8[1024] | Raw message (`SIGN_MODE_DATA`) or external `mu` (`SIGN_MODE_EXTERNAL_MU`). Only bytes up to message_size are used. |
| 1403 | | - |
| 1404 | | -*Table: `SIGN_WITH_EXPORTED_MLDSA` output arguments* |
| 1405 | | - |
| 1406 | | -| **Name** | **Type** | **Description** |
| 1407 | | -| -------- | --------- | --------------- |
| 1408 | | -| chksum | u32 | Checksum over other output arguments, computed by Caliptra. Little endian. |
| 1409 | | -| fips\_status | u32 | Indicates if the command is FIPS approved or an error. |
| 1410 | | -| derived\_pubkey | u8[2592] | The ML-DSA-87 public key associated with the signing key. |
| 1411 | | -| signature | u8[4627] | The ML-DSA-87 signature. |
| 1412 | | - |
| 1413 | | -The `exported_cdi_handle` can be created by calling `DeriveContext` with the `export-cdi` and `create-certificate` flags, as with `SIGN_WITH_EXPORTED_ECDSA`. |
| 1414 | | - |
| 1415 | 2749 | ## Checksum |
| 1416 | 2750 | |
| 1417 | | -For every command except for FW_LOAD, the request and response feature a checksum. This |
| 2751 | +For every command except for FIRMWARE_LOAD, the request and response feature a checksum. This |
| 1418 | 2752 | mitigates glitches between clients and Caliptra. |
| 1419 | 2753 | |
| 1420 | 2754 | The checksum is a little-endian 32-bit value, defined as: |
| @@ -1439,10 +2773,11 @@ |
| 1439 | 2773 | |
| 1440 | 2774 | *Table: FIPS status codes* |
| 1441 | 2775 | |
| 1442 | | -| **Name** | **Value** | Description |
| 1443 | | -| ------- | ----- | ----------- |
| 1444 | | -| `FIPS_APPROVED` | `0x0000_0000` | Status of command is FIPS approved |
| 1445 | | -| `RESERVED` | `0x0000_0001 - 0xFFFF_FFFF` | Other values reserved, will not be sent by Caliptra |
| 2776 | +| **Name** | **Value** | Description | |
| 2777 | +| --------------- | --------------------------- | --------------------------------------------------- | |
| 2778 | +| `FIPS_APPROVED` | `0x0000_0000` | Status of command is FIPS approved | |
| 2779 | +| `RESERVED` | `0x0000_0001 - 0xFFFF_FFFF` | Other values reserved, will not be sent by Caliptra | |
| 2780 | + |
| 1446 | 2781 | |
| 1447 | 2782 | ## Runtime Firmware updates |
| 1448 | 2783 | |
| @@ -1451,7 +2786,7 @@ |
| 1451 | 2786 | |
| 1452 | 2787 | ### Applying updates |
| 1453 | 2788 | |
| 1454 | | -A Runtime Firmware update is triggered by the `CALIPTRA_FW_LOAD` command. Upon |
| 2789 | +A Runtime Firmware update is triggered by the `FIRMWARE_LOAD` command. Upon |
| 1455 | 2790 | receiving this command, Runtime Firmware does the following: |
| 1456 | 2791 | |
| 1457 | 2792 | 1. Locks the mailbox to writes |
| @@ -1499,16 +2834,15 @@ |
| 1499 | 2834 | * PL0 - High privilege. Only 1 PAUSER in the SoC may be at PL0. The PL0 PAUSER |
| 1500 | 2835 | is denoted in the signed Caliptra firmware image. The PL0 PAUSER may call any |
| 1501 | 2836 | supported DPE commands. Only PL0 can use the CertifyKey command. Success of the |
| 1502 | | - CertifyKey command signifies to the caller that it is at PL0. A number of |
| 1503 | | - mailbox commands are also restricted to PL0; see |
| 1504 | | - [Mailbox command privilege levels](#mailbox-command-privilege-levels). |
| 2837 | + CertifyKey command signifies to the caller that it is at PL0. Only PL0 can use |
| 2838 | + the POPULATE\_IDEV\_ECC384\_CERT and POPULATE\_IDEV\_MLDSA87\_CERT mailbox commands. |
| 1505 | 2839 | * PL1 - Restricted privilege. All other PAUSERs in the SoC are PL1. Caliptra |
| 1506 | 2840 | SHALL fail any calls to the DPE CertifyKey with format=X509 by PL1 callers. |
| 1507 | 2841 | PL1 callers should use the CSR format instead. |
| 1508 | 2842 | |
| 1509 | 2843 | PAUSER and Locality map 1:1. Consequently, only the single DPE Client associated |
| 1510 | | -with PL0 level, is authorized to invoke CertifyKey DPE command with format=x509. |
| 1511 | | -All other DPE Clients have instead restricted privileges associated to PL1 (as |
| 2844 | +with PL0 level, is authorized to invoke CertifyKey DPE command with format=x509. |
| 2845 | +All other DPE Clients have instead restricted privileges associated to PL1 (as |
| 1512 | 2846 | described above). |
| 1513 | 2847 | |
| 1514 | 2848 | #### PAUSER privilege level active context limits |
| @@ -1536,20 +2870,20 @@ |
| 1536 | 2870 | Further, it is not allowed for PL1 to call DeriveContext with the intent to change locality to PL0's locality; this would increase the number |
| 1537 | 2871 | of active contexts in PL0's locality, and hence allow PL1 to DOS PL0. |
| 1538 | 2872 | |
| 1539 | | -### Caliptra DPE Profile |
| 1540 | | - |
| 1541 | | -Caliptra defines the **Caliptra DPE Profile**, which inherits from the [OCP DPE iRoT Profile](https://github.com/opencomputeproject/Security/tree/main/specifications/dpe-irot-profile) (`DPE_PROFILE_IROT_P384_SHA384`) with some modifications. This section describes the profile attributes and specific requirements for the Caliptra DPE implementation. |
| 2873 | +### DPE profile implementation |
| 2874 | + |
| 2875 | +The DPE iRoT profile leaves some choices up to implementers. This section |
| 2876 | +describes specific requirements for the Caliptra DPE implementation. |
| 1542 | 2877 | |
| 1543 | 2878 | | Name | Value | Description | |
| 1544 | 2879 | | -------------------------- | ------------------------------ | ------------------------------------------------------------------------------------------------------ | |
| 1545 | | -| Profile Variant | `Caliptra DPE Profile` | Derived from `DPE_PROFILE_IROT_P384_SHA384`. | |
| 2880 | +| Profile Variant | `DPE_PROFILE_IROT_P384_SHA384` | The profile variant that Caliptra implements. | |
| 1546 | 2881 | | KDF | SP800-108 HMAC-CTR | KDF to use for CDI (tcg.derive.kdf-sha384) and asymmetric key (tcg.derive.kdf-sha384-p384) derivation. | |
| 1547 | 2882 | | Simulation Context Support | Yes | Whether Caliptra implements the optional Simulation Contexts feature. | |
| 1548 | 2883 | | Supports ExtendTci | Yes | Whether Caliptra implements the optional ExtendTci command. | |
| 1549 | 2884 | | Supports Auto Init | Yes | Whether Caliptra will automatically initialize the default DPE context. | |
| 1550 | 2885 | | Supports Rotate Context | Yes | Whether Caliptra supports the optional RotateContextHandle command. | |
| 1551 | 2886 | | CertifyKey Alias Key | Caliptra Runtime Alias Key | The key that will be used to sign certificates that are produced by the DPE CertifyKey command. | |
| 1552 | | -| `export-cdi-format` | KeyVault Slot Handle | Overrides the iRoT profile default (which returns the actual CDI) to return a 32-byte handle to a KeyVault slot instead. | |
| 1553 | 2887 | |
| 1554 | 2888 | |
| 1555 | 2889 | ### Supported DPE commands |
| @@ -1559,8 +2893,7 @@ |
| 1559 | 2893 | * GetProfile |
| 1560 | 2894 | * InitializeContext |
| 1561 | 2895 | * DeriveContext |
| 1562 | | - * **Note**: The value returned when `export-cdi` is requested is a 32-byte handle to a KeyVault slot containing the CDI, not the actual CDI. This overrides the default iRoT profile behavior. |
| 1563 | | - * **Note**: The "export-cdi" flag is only available in the locality of the PL0 PAUSER. |
| 2896 | + * **Note**: The "export-cdi" flag is only available in the locality of the PL0 PAUSER. |
| 1564 | 2897 | * CertifyKey |
| 1565 | 2898 | * Caliptra DPE supports two formats for CertifyKey: X.509 and PKCS#10 CSR. |
| 1566 | 2899 | X.509 is only available to PL0 PAUSERs. |
| @@ -1639,12 +2972,13 @@ |
| 1639 | 2972 | |
| 1640 | 2973 | ### Internal representation of TCI nodes |
| 1641 | 2974 | |
| 1642 | | -| **Byte offset** | **Bits** | **Name** | **Description** |
| 1643 | | -| ----- | ---- | ---------------- | ----------------------------------------------------- |
| 1644 | | -| 0x00 | 383:0 | `TCI_CURRENT` | Current TCI measurement value |
| 1645 | | -| 0x30 | 383:0 | `TCI_CUMULATIVE` | TCI measurement value |
| 1646 | | -| 0x60 | 31:0 | `TYPE` | `TYPE` parameter to the DeriveContext call that created this node |
| 1647 | | -| 0x64 | 31:0 | `LOCALITY` | `TARGET_LOCALITY` parameter to the DeriveContext call that created this node (PAUSER) |
| 2975 | +| **Byte offset** | **Bits** | **Name** | **Description** | |
| 2976 | +| --------------- | -------- | ---------------- | ------------------------------------------------------------------------------------- | |
| 2977 | +| 0x00 | 383:0 | `TCI_CURRENT` | Current TCI measurement value | |
| 2978 | +| 0x30 | 383:0 | `TCI_CUMULATIVE` | TCI measurement value | |
| 2979 | +| 0x60 | 31:0 | `TYPE` | `TYPE` parameter to the DeriveContext call that created this node | |
| 2980 | +| 0x64 | 31:0 | `LOCALITY` | `TARGET_LOCALITY` parameter to the DeriveContext call that created this node (PAUSER) | |
| 2981 | + |
| 1648 | 2982 | |
| 1649 | 2983 | ### Certificate generation |
| 1650 | 2984 | |
| @@ -1652,7 +2986,7 @@ |
| 1652 | 2986 | |
| 1653 | 2987 | The DPE `GET_CERTIFICATE_CHAIN` command shall return the following certificates: |
| 1654 | 2988 | |
| 1655 | | -* IDevID (optionally added by the SoC via POPULATE\_IDEV\_CERT) |
| 2989 | +* IDevID (optionally added by the SoC via POPULATE\_IDEV\_ECC384\_CERT) |
| 1656 | 2990 | * LDevID |
| 1657 | 2991 | * FMC Alias |
| 1658 | 2992 | * Runtime Alias |